Coalition to Reduce Cyber Risk (CR2) is launching the Cyber Risk Management Pledge at the RSA Conference on June 8th 2022. The CRM Pledge promotes risk-based approaches to cybersecurity around the world to mitigate cyber risks and facilitate economic growth. Exiger is proud to join efforts to enhance cyber resiliency and counter evolving cross-border cyber threats, such as the growth of ransomware.
Former assistant director at the US Cybersecurity and Infrastructure Security Agency and current SVP of Critical Infrastructure at Exiger Bob Kolasky has led the charge in not only signing this pledge, but in sharing his industry expertise on navigating cyber risk. In a recent article by The Financial Times and a panel by The Washington Post, he has spoken of the importance of increasing resiliency, including in the government, to prevent cyber attacks.
Exiger has joined the below companies in this groundbreaking pledge:
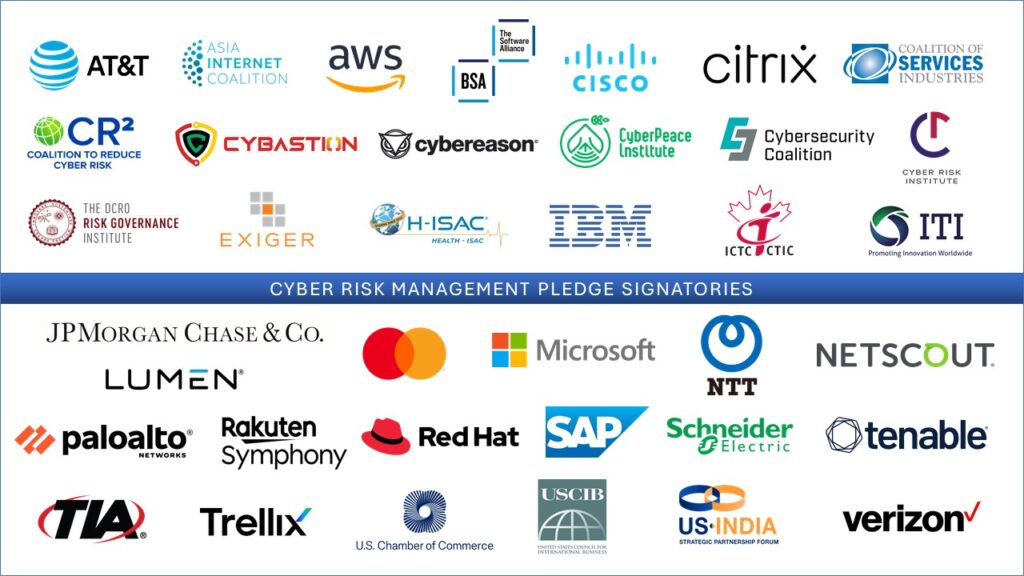
Cyber Risk Management Pledge
The signatories to this pledge understand that in order to enhance cyber resiliency and counter evolving cross-border cyber threats such as the growth of ransomware, we must enable the seamless implementation of risk-based approaches to cybersecurity around the world.
Internationally recognized cybersecurity frameworks and standards that are based upon the principles of risk management and relevant across sectors support such implementation by strengthening consistency and continuity among interconnected sectors and throughout global supply chains.
Increased and ongoing adoption of these frameworks and international standards by companies and governments around the world will mitigate cyber risks and facilitate economic growth. To further advance adoption of international approaches to cybersecurity risk management, we commit to:
- Encourage the development, evolution and implementation of risk-based approaches based on consensus-based frameworks, standards and risk management best practices, such as ISO/IEC 27110 and 27103, or the NIST Cybersecurity Framework;
- Support efforts of our vendors and supply chain contributors to adopt risk-based cybersecurity approaches in order to help small businesses flourish while improving the resiliency of the cyber ecosystem;
- Incorporate ISO/IEC 27110 and 27103, the NIST Cybersecurity Framework, or other widely accepted international cybersecurity standards as a foundation of our cybersecurity policies and controls wherever applicable and feasible; and
- Periodically reassess our cybersecurity policies and controls against revisions to such cybersecurity standards and actively participate in industry-driven initiatives to improve those standards.
A commitment to internationally recognized cyber risk management approaches and frameworks that are relevant across sectors can bring widespread economic benefits, help governments achieve their policy goals, bolster collective security, and enhance cyber resiliency across the ecosystem.