The U.S. Securities and Exchange Commission (SEC) recently announced new rules around cyber risk reporting for public companies, specifically, transparency and accountability for their cybersecurity risk and incidents. These rules have been much discussed, and there are mixed responses across industry and sectors — some are even calling it the “Sarbanes Oxley for cybersecurity.”
Below is a summary of the new rule, possible implications for public companies, and Exiger’s technology for cyber risk management.
New Push to Disclose Material Incidents Related to Cybersecurity
The SEC is expecting boards and executives to understand cybersecurity risk and governance, such as risk treatment plans. Much attention is focused on material incidents — those that a public company’s shareholders would consider important in making an investment decision.
The SEC Chair, Gary Gensler, said, “Whether a company loses a factory in a fire — or millions of files in a cybersecurity incident — it may be material to investors. Currently, many public companies provide cybersecurity disclosure to investors.”
The original proposal from the SEC in March 2022 said that it wanted companies to publicly declare one cybersecurity expert on the board of directors and one within management. These published rules, however, backed off the requirement for the board expert.
Details on How to Report Incidents
Publicly listed companies must now include details about the incident in periodic report filings, specifically on 8-K forms. Here’s a summary of key specifications:
- The disclosure should include information on “nature, scope and timing,” as well as “its material impact or reasonably likely” impact on the company. Registrants also will have to describe their processes for identifying and managing cyber risks in annual reports.
- These new cybersecurity incident reporting rules are set to take effect on December 18, 2023, or 30 days after being published in the Federal Register (whichever comes later). However, smaller companies will be granted an additional 180 days before they are required to provide Form 8-K disclosures.
- In some instances, the disclosure timeline may also be postponed if the U.S. Attorney General determines that an immediate disclosure would pose a significant risk to national security or public safety.
Questions abound about the threshold for “materiality,” since it can take weeks or months to determine whether a breach has occurred. Also, there’s not much specified by way of fines and penalties, and certain exceptions have been noted in the text of the lengthy rule document.
The SEC also adopted new regulations mandating foreign private issuers to provide equivalent disclosures following cybersecurity breaches.
Potential Implications of the New Rules
The SEC argues that these new rules will provide more consistent, comparable and transparent disclosure around cyber incidents. “Through helping to ensure that companies disclose material cybersecurity information, today’s rules will benefit investors, companies and the markets connecting them,” Gensler said in the press release.
There is a lack of consensus of where precisely these new rules will create market pressure, though, at a minimum, there is an expectation that an enterprise can describe how it is deploying a risk-based cybersecurity program.
- Proponents argue that the new rules hold the potential to provide investors and market participants across the board with critical information relating to a company’s risk management and strategy as well as governance in its periodic reporting.
- Challengers believe that the rules mandate public disclosure of too much, too sensitive and highly subjective information, without deference to regulators of public companies or government agencies specializing in cybersecurity management and incident response, such as CISA and the FBI.
- Still others assess that the rule could harm the very investors it purports to protect by prematurely publicizing a company’s vulnerabilities, which could exacerbate the response to and impact from cybersecurity risks.
How Exiger Can Help with Compliance
Exiger will continue to assess the new rules and understand how this regulation will be applied. Ostensibly, the rule will lead to greater transparency, which advances Exiger’s mission to uncover hidden cybersecurity risk with data.
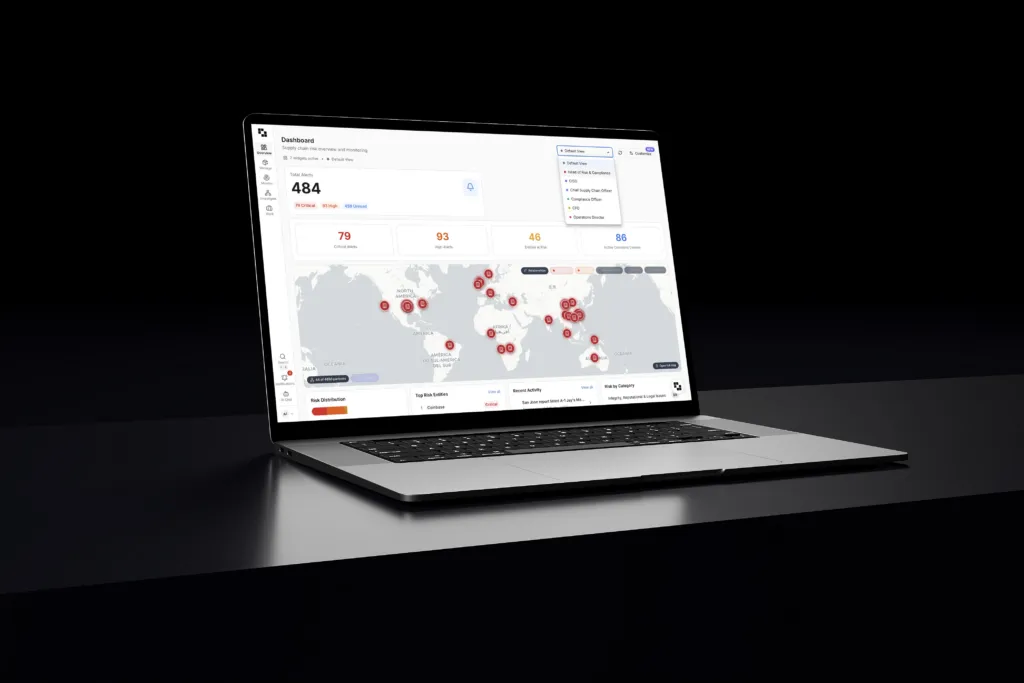
Exiger helps clients prioritize vulnerable vendors and third parties, by identifying hidden risks and dependencies in the cyber supply chain and understanding ecosystem exposure. Instead of waiting for an SEC disclosure, Exiger’s platform provides warning of cyber incidents – to include data breaches and ransomware – so that clients can understand the potential scale and scope of a supply chain attack. Exiger’s risk management platform is specifically designed to assess supply chain risk management of third parties by systematically investigating cyber risks to and through the supply chain, prioritizing by potential impact, and continuously monitoring of risk exposure.
With the ongoing monitoring and risk scoring, clients can determine where to focus attention on potential non-compliance, as well as correlate with other regulatory requirements. Exiger uses automation and data-driven prioritization to focus limited resources and proactively identify connected risk through the supply chain.