The penalties are not theoretical. Importers caught in an illegal transshipment scheme by U.S. Customs and Border Protection (CBP) — even unknowingly — can face retroactive duty assessments of hundreds of percent above declared rates, inventory seizure, loss of import privileges, suspension from trusted-trader programs, and criminal prosecution under 19 U.S.C. § 1586. CBP has the authority to look back five years.
Sector Exposure
Industries under Active CBP Targeting
CBP and Customs Trade Partnership Against Terrorism (CTPAT) guidance now identify entire industries that are being actively targeted, and enforcement actions are arriving in the form of quiet, easily-overlooked requests for information that can quickly snowball into multi-million dollar penalties.
Critical enforcement signal
What is a CBP Form CF-28 and Why Does It Matter?
Most importers don't realize that before CBP escalates a transshipment concern to a formal investigation, it typically sends a quiet but powerful signal: Customs Form 28 (CF-28), "Request for Information." This is not a courtesy. It is an official demand under Section 509(a) of the Tariff Act of 1930, and how you respond — or fail to respond — determines what happens next.
A CF-28 is typically triggered when CBP finds incomplete, inaccurate, or suspicious information in your entry documentation. In the context of transshipment, it means CBP has already flagged your shipment as potentially misrepresenting country of origin, valuation, or classification.
Proactive Requirements
Red Flag Indicators CBP Expects You to Monitor
CBP's CTPAT guidance makes clear that importers are expected to conduct ongoing supply chain risk assessments and identify red flags proactively. Failure to do so — and failure to detect the following indicators — undermines your "reasonable care" defense.
Customer Expectations
What CBP Requires and Where Companies Fall Short
The CTPAT alert is explicit about what's expected of members. Each requirement creates a workflow problem most companies cannot solve manually.
CBP REQUIREMENTS
- Conduct strong risk assessments to identify shipments of potential concern
- Vet all foreign suppliers against program minimum-security criteria
- Build relationships with suppliers and business partners
- Maintain notification procedures when anomalies are detected
- Verify country-of-origin (COO) markings before importing
CHALLENGES WITHOUT EXIGER SUPPLY CHAIN AI
- Manual review can’t scale across global supplier networks
- Supplier vetting is time-consuming and data is fragmented across jurisdictions
- No visibility into nth-tier suppliers — you only know who you buy from directly
- Anomaly detection requires structured data and change monitoring at scale
- COO verification requires cross-referencing trade data, not just reviewing documents
The Importer's Action Plan
What Importers Should Do Now to Meet Requirements
CBP’s enforcement posture is clear: importers cannot rely solely on supplier representations. The following workflow reflects what CTPAT guidance — and courts — define as reasonable care in preventing transshiptment exposure.
Map and Vet Your Full Supply Chain
Know every tier of your supply chain — not just your direct supplier. Verify that the declared manufacturing country has the capacity and infrastructure to produce the goods at the volumes you are importing. Conduct factory verification where feasible.
Conduct Ongoing Risk Assessments
Implement a format, documented supply chain risk assessment process aligned with CTPAT minimum-security criteria. Review for AD/CVD exposure, tariff applicability, and country-of-origin verification on every product category you import.
Verify Country of Origin Documentation
Per Section 304 of the Tariff Act of 1930, all foreign-origin goods must be properly marked. Verify certificates of origin and HTS classifications are accurate before filing entry documents. Fraudulent COOs from suppliers do not transfer liability away from you.
Monitor for Red Flag Indicators in Real Time
Establish internal controls to flag anomalous routing, pricing deviations, unusual transaction structures, or suppliers with inconsistent trade volumes. These are the same data signals CBP uses to identify evasion schemes.
Know Your Freight Forwarders
Use only trade facilitators with sound export management and compliance programs. BIS guidance warns against routed export transactions unless a long-standing, trusted relationship exists with all parties in the transaction.
Have an Anomaly Notification Procedure
CTPAT requires members to have documented procedures for detecting and reporting anomalies. If something looks wrong, your team must know who to call — both internally and at CBP. Suspected violations can be reported through CBP’s e-Allegations system.
Respond to CF-28s Immediately and Strategically
If you receive a CF-28, do not treat it as administrative routine. Engage legal counsel and trade compliance experts immediately. Respond within 30 days. Assess whether a Prior Disclosure submission is warranted to mitigate penalties. Audit your broader import history for related exposure across the past five years.
Take Control of Your Compliance Posture
How Exiger Helps
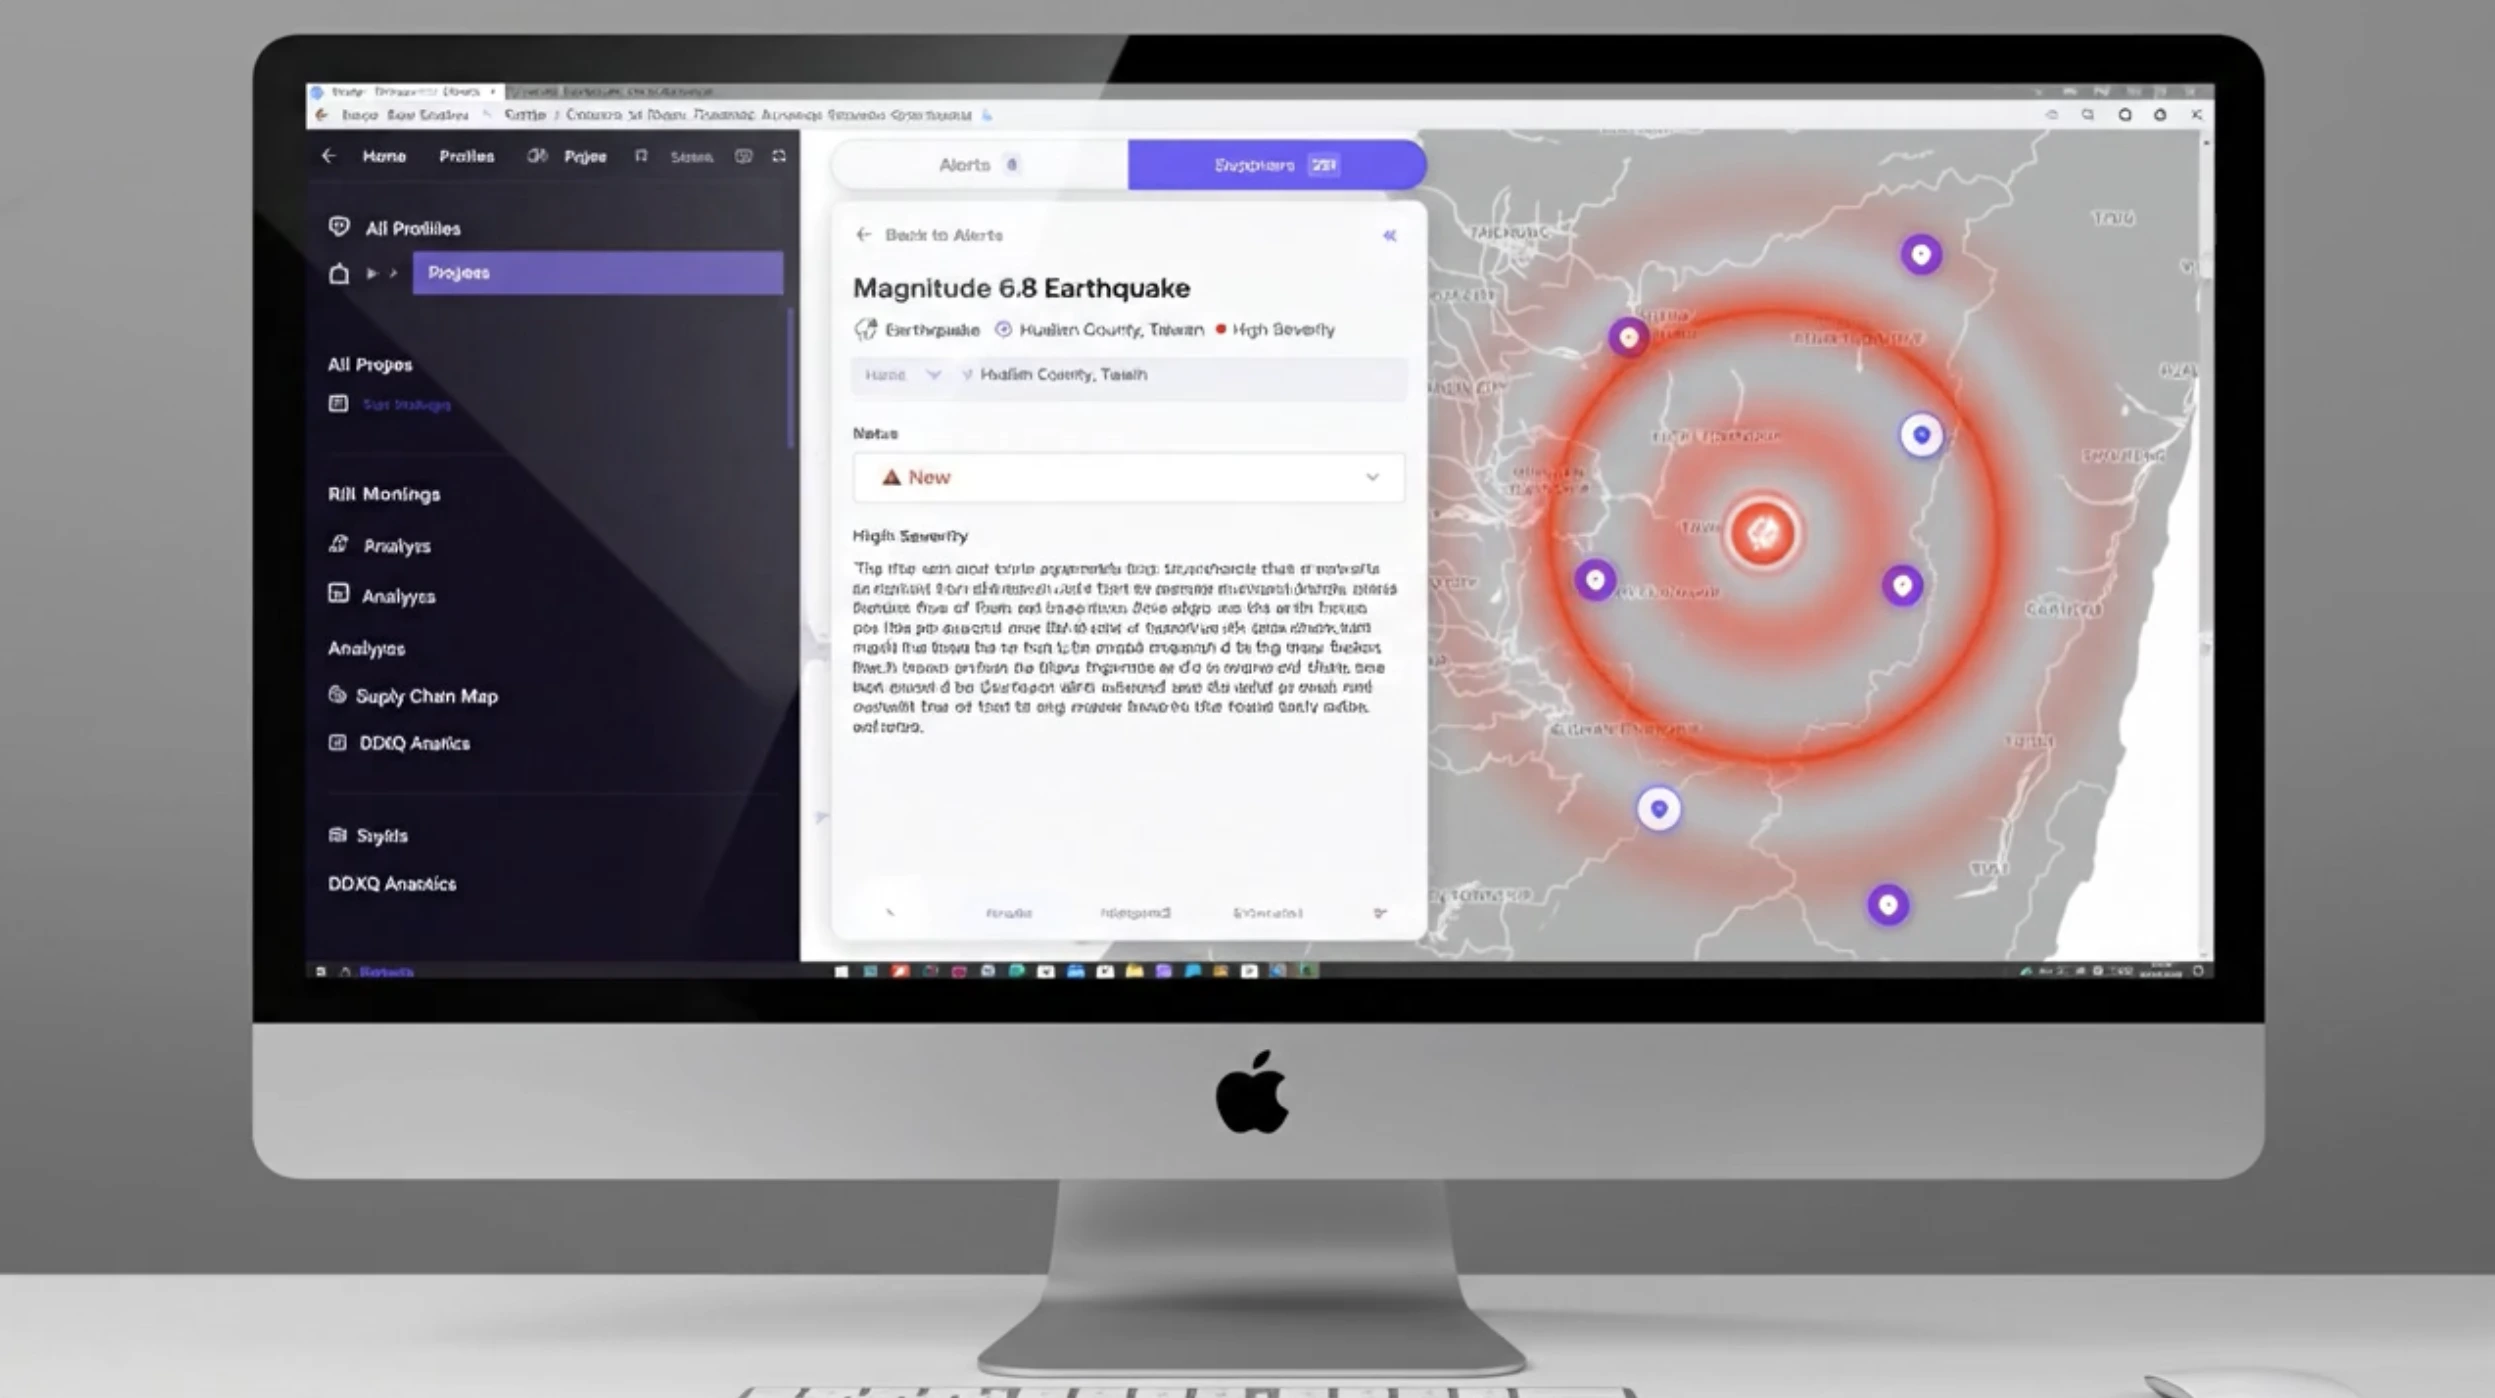
The 1EXIGER.AI platform helps organizations find blind spots in their supply chains before disruption hits — turning reactive compliance into proactive defense.

Supplier Network Mapping
Connect relationships across suppliers, sites, and upstream dependencies down to the nth tier.

Real-Time Risk Monitoring
Connect relationships across suppliers, sites, and upstream dependencies down to the nth tier.

Regulator-Ready Documentation
Traceability artifacts and audit trails that let you respond to a CF-28 with confidence.
Your Suppliers Have Blind Spots. Exiger Finds Them First.
Exiger provides the only purpose-built illegal transshipment detection capability used by CBP — which is now available to importers who need to find the same risks before enforcement agencies do. Don’t wait for a CF-28 to indicate your exposure.