Third-Party Risk Management Orchestration
Act first on third-party risk with a coordinated response across your business. Exiger connects proprietary risk intelligence, your teams, and an AI workforce to execute decisions across enterprise systems—uniting compliance, cybersecurity, procurement, supply chain and operations under your controls.
Exiger Serves 150+ Fortune 500 Companies and More Than 60 U.S. Federal Agencies


Coordinate the Response Across the Business
A change in one relationship can require decisions from compliance, cybersecurity, procurement and the business owner. Each team needs relevant evidence, clear responsibilities and a record of what was decided.
1EXIGER.AI links Exiger intelligence to your assessments and enterprise systems, so risk events can initiate the work your program requires. AI agents assist with triage, evidence review and workflow execution under your policies and permissions.
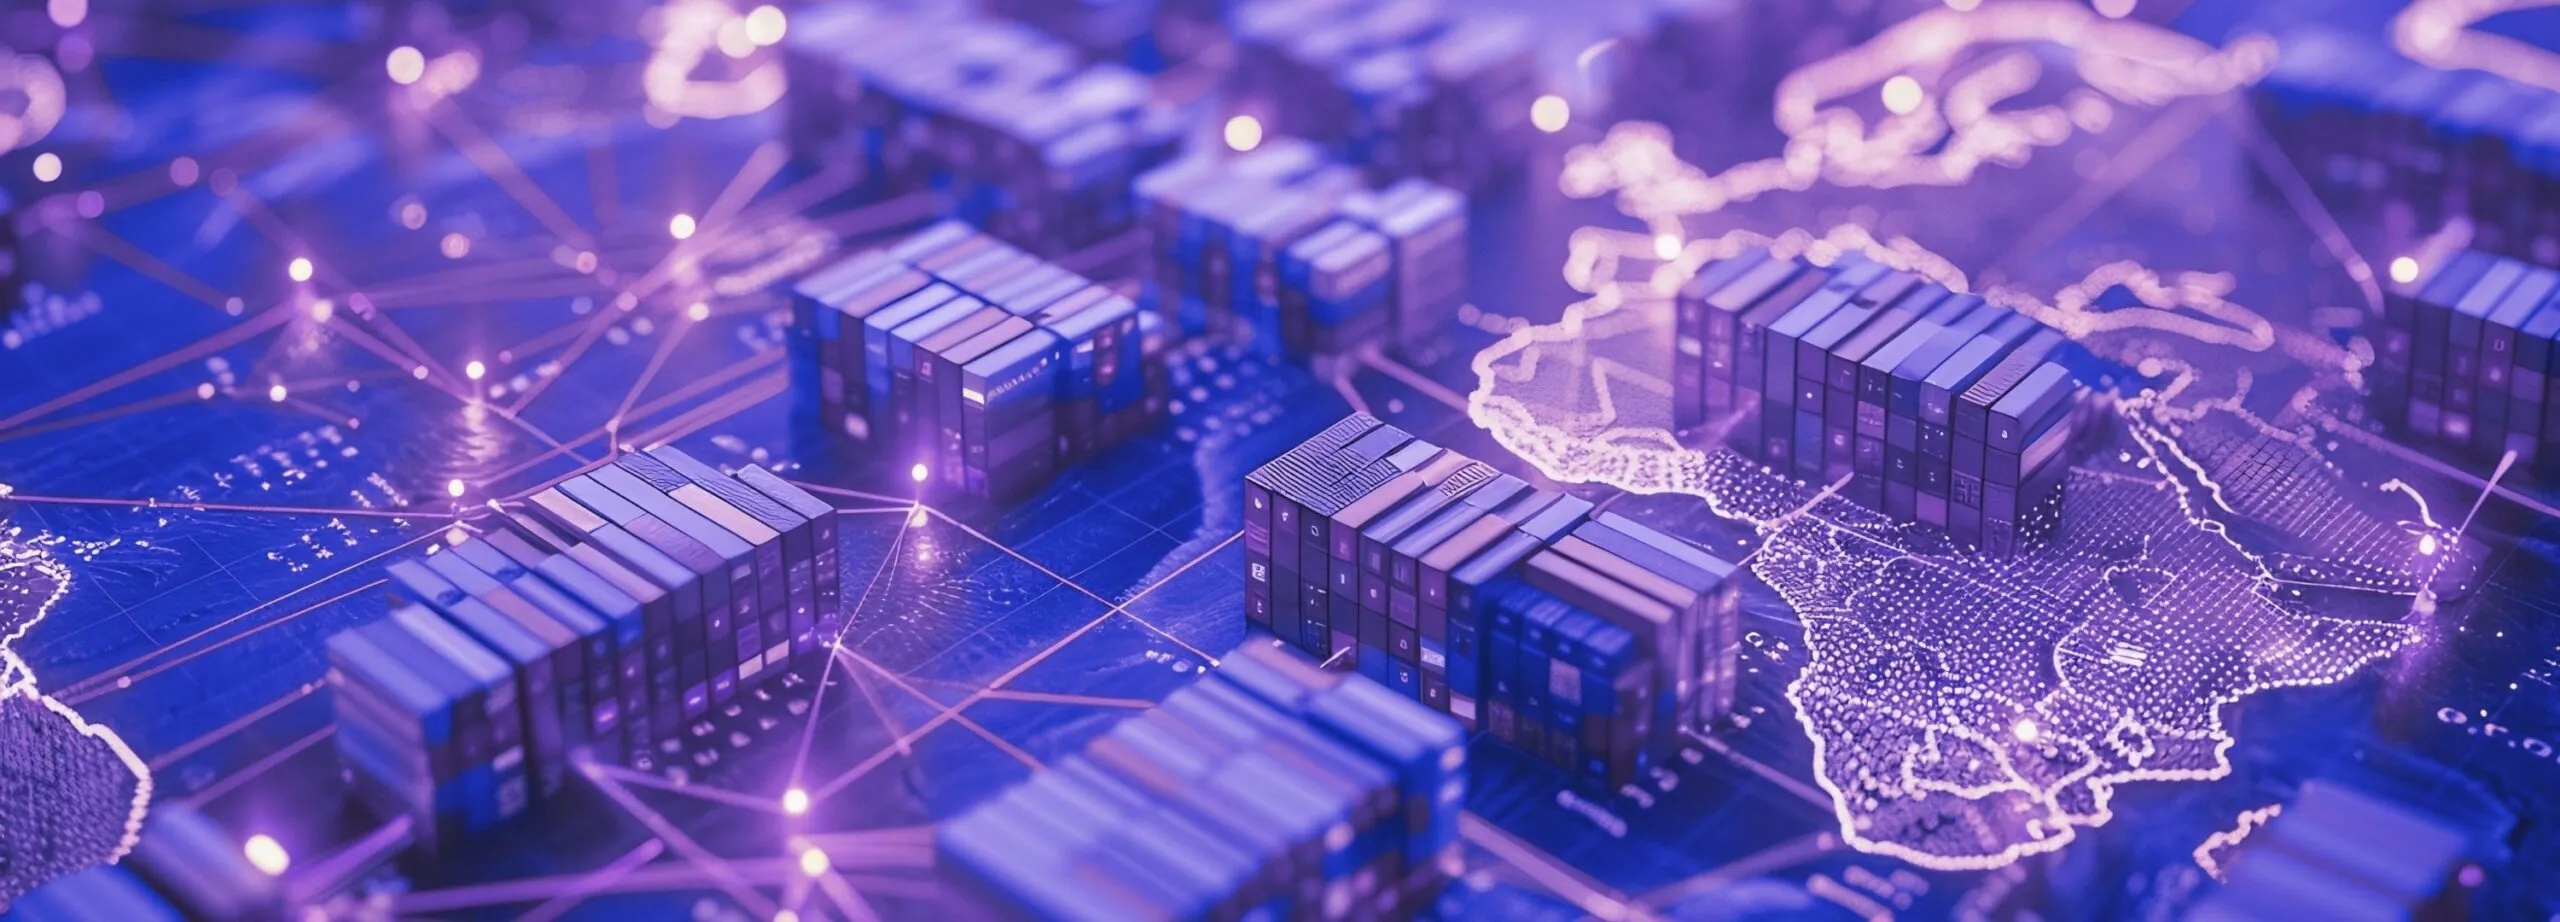
Identify which relationships are affected
Connect a risk event to the third parties, subsidiaries and locations involved. Exiger’s entity resolution and relationship mapping help teams identify indirect exposure and assess its significance before choosing a response.
- Trace ownership and deeper third-party dependencies, including geographic and concentration exposure.
- Prioritize review using third-party criticality, risk severity and potential business impact.
- Inspect source evidence and AI rationale behind alerts and recommendations.
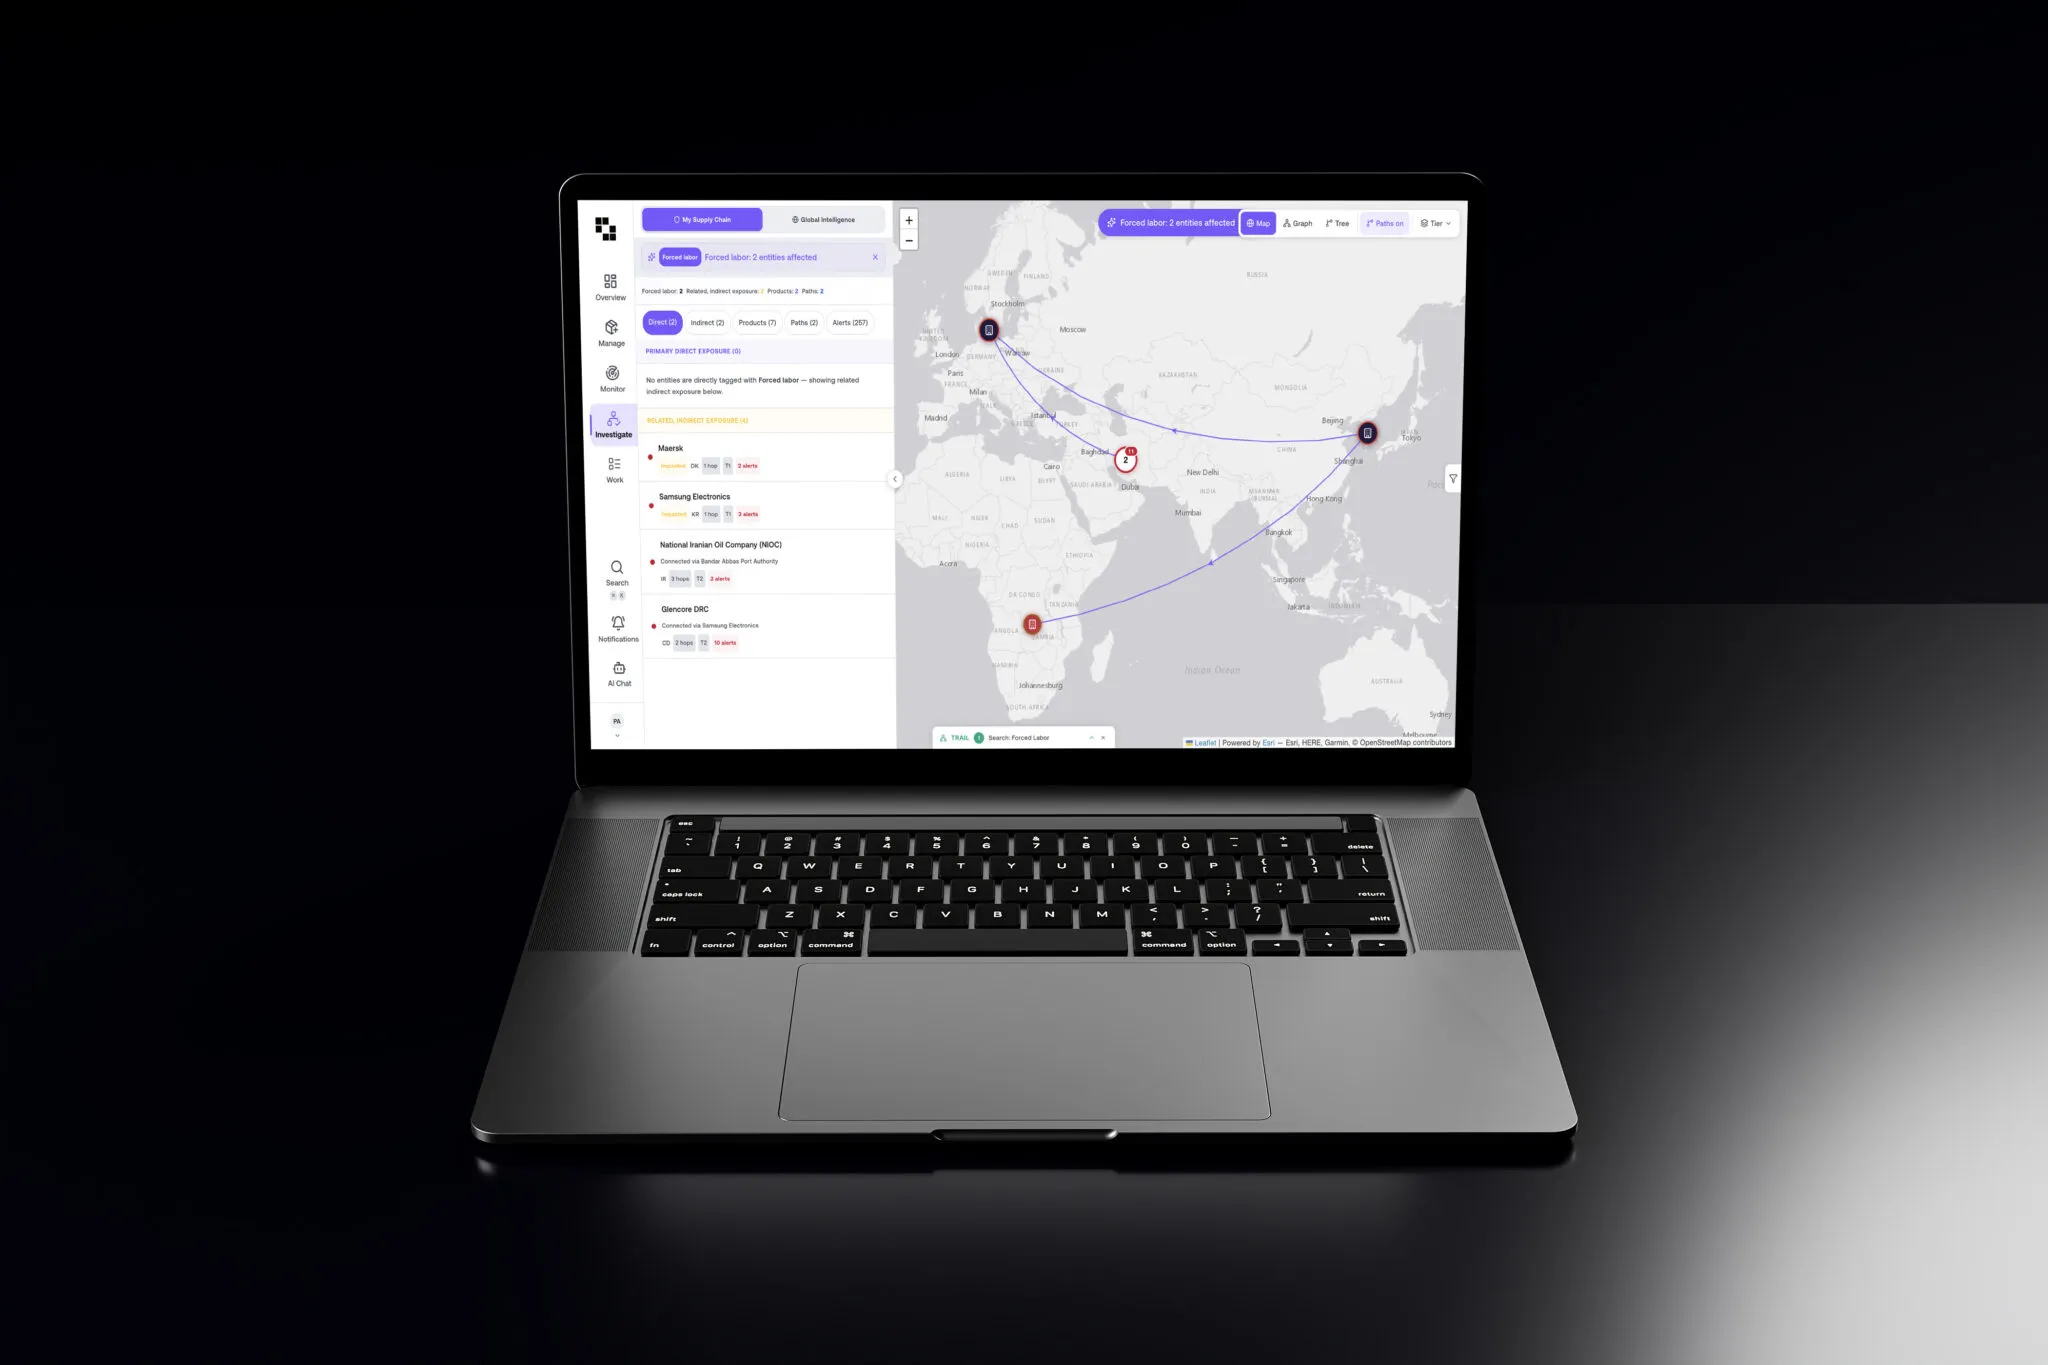
Carry the assessment into the systems teams use
Build assessment and response workflows around your existing processes. 1EXIGER.AI can exchange data with customer systems through APIs, bring questionnaires and supporting documents into the assessment, and route work to the people or agents responsible for the next step.
- Create and edit workflows with no-code tools, including review steps for multiple risk domains.
- Request information and documents from third parties, then use the responses in the risk review.
- Share risk information and workflow outputs with procurement, enterprise risk and service management systems through configured integrations.
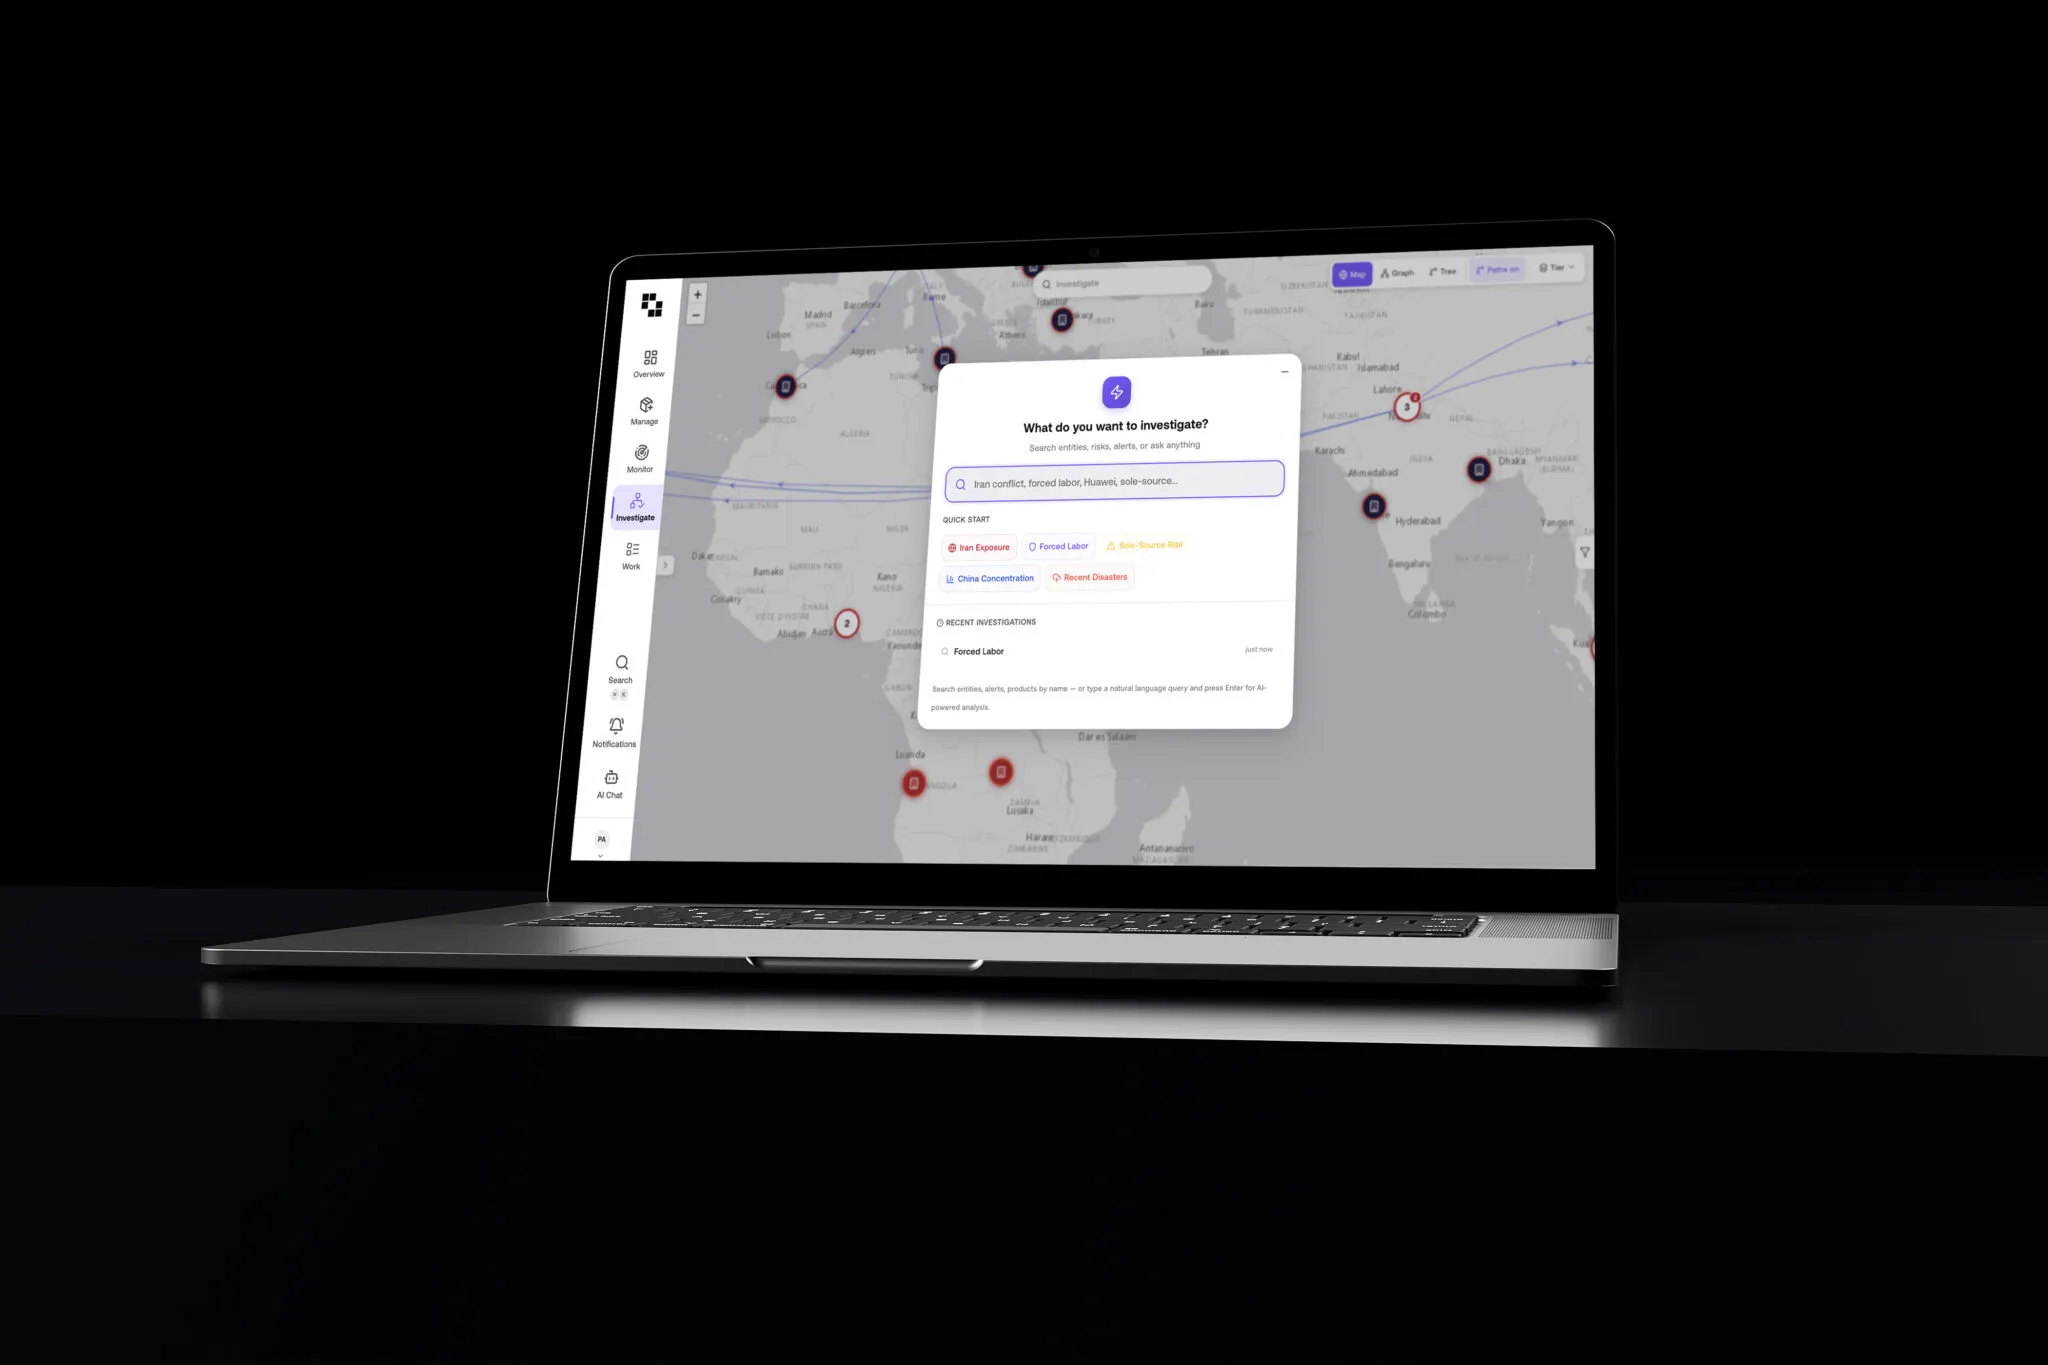
Set the rules for decisions and follow-through
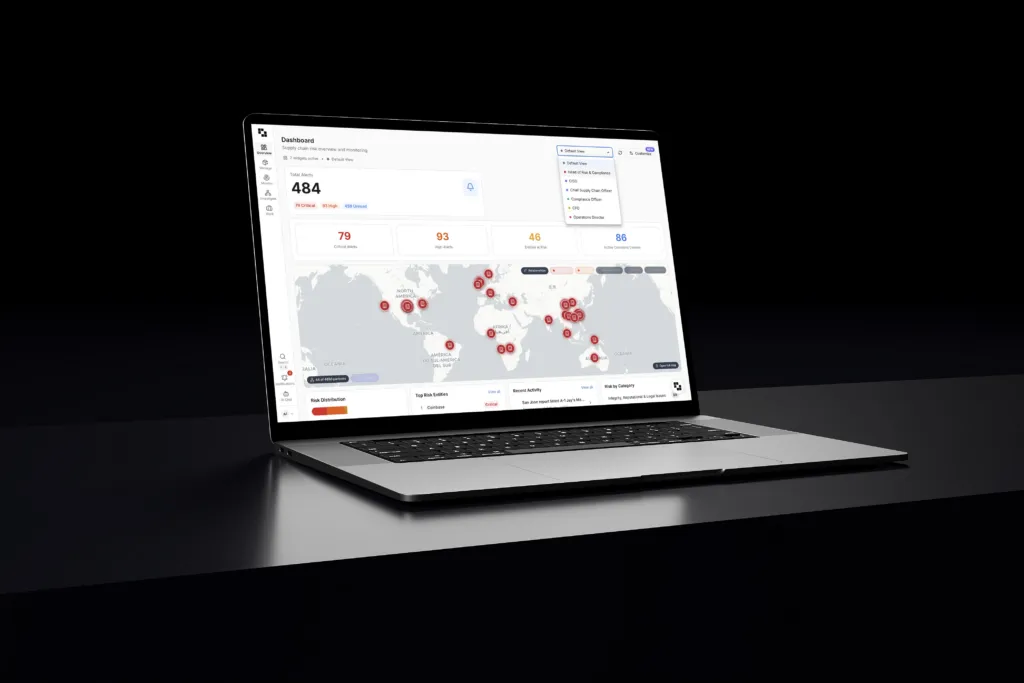
Apply the risk appetites, review requirements and access controls your organization chooses. Track mitigation owners, due dates and overdue work. Configurable dashboards give program leaders and oversight teams a view of exposure and unresolved actions.
- Configure risk models, thresholds and notifications around your program requirements.
- Assign tasks, record evidence and escalate issues to risk registers.
- Apply different permissions and risk configurations across business units or regions.
- Report on high-risk relationships, open alerts and outstanding actions for management and risk committees.
Proven Results
A Vertically Integrated Approach to Third-Party and Supply Chain Risk Management in Healthcare
A case study about Northwell Health, New York’s largest healthcare provider, partnering with Exiger on a vendor risk management ecosystem.
Action the Evidence Behind the Decision
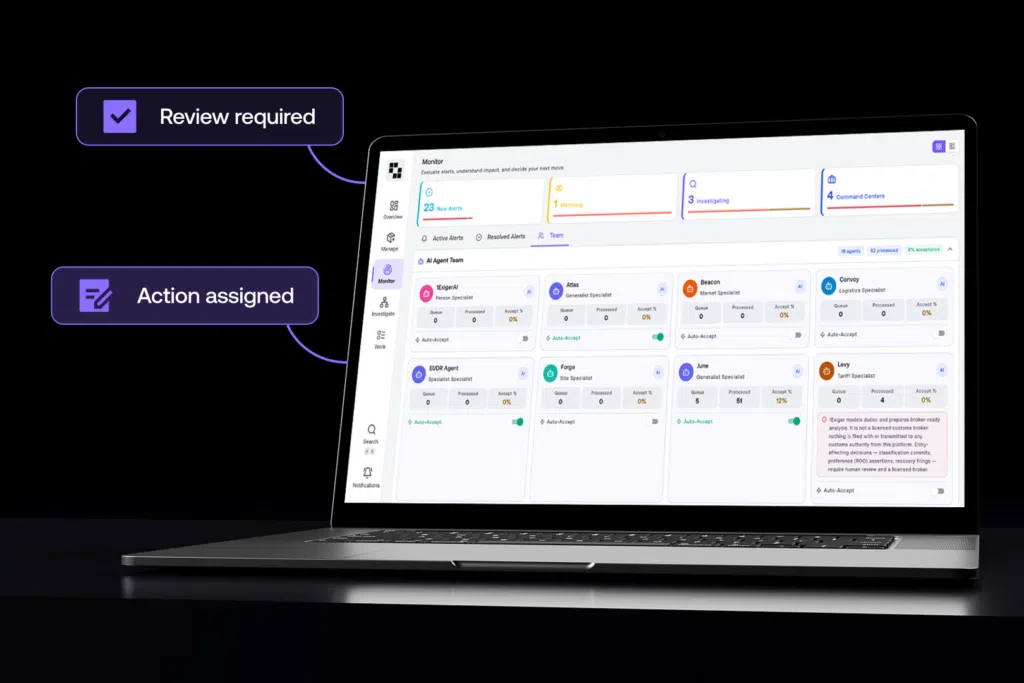
Review source evidence alongside an alert’s severity and confidence. Inspect AI assessments and recommendations, then retain the record of decisions and assigned actions. Know that your data is secure: Exiger provides a FedRAMP-authorized platform with SOC 2 Type 2 assurance and ISO 27001 certification.
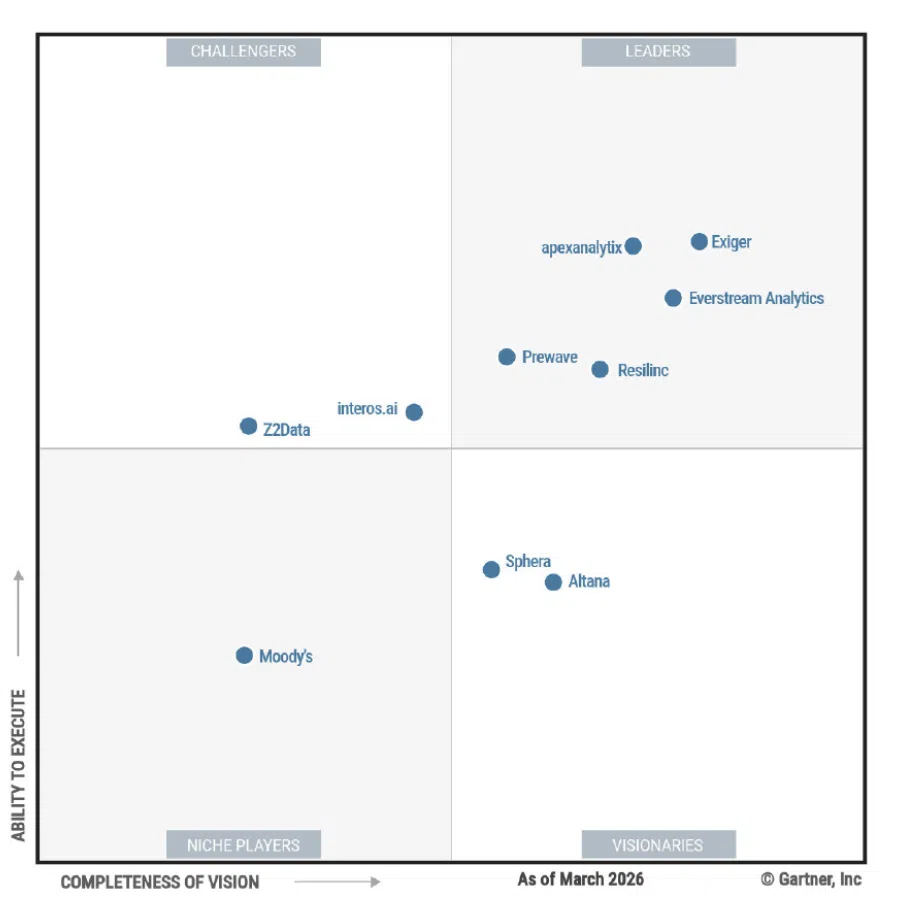
Exiger Named a Leader in the 2026 Gartner® Magic Quadrant™ for Supplier Risk Management Solutions Two Years in a Row
Highest in Execution and Furthest in Vision

Exiger named a Winter 2026 leader in Governance, Risk, and Compliance
Exiger is a mission-driven, market-moving force redefining AI-powered supply chain resilience.
Exiger Named Value Leader in The Hackett Group’s Spring 2026 SolutionMap for Procurement Technology.

We were able to achieve our own security objectives and satisfy customer demands.
Exiger Named Winner of TPRA 2024 Third Party Risk Management Service Provider Innovator Award
Exiger Named in Fast Company’s List of Brands That Matter for Second Consecutive Year
Three Exiger Executives Awarded 2024 Pros to Know by Supply & Demand Chain Executive
Exiger and Oshkosh Recognized by Supply & Demand Chain Executive with 2023 Top Supply Chain Projects Award

Exiger tops ProcureTech100 for the 3rd consecutive year
Have TPRM Orchestration Questions? We Have Answers.
What is TPRM orchestration?
TPRM orchestration connects the tasks involved in managing a third-party relationship, including assessments, reviews, monitoring and remediation. It brings the necessary intelligence into those tasks and coordinates responsibilities across participating teams and connected enterprise systems.
How does orchestration relate to third-party risk management?
TPRM covers the overall discipline of assessing and managing risk in third-party relationships. Orchestration describes how that work is coordinated across functions and systems, including what starts an assessment, who reviews the evidence and how resulting actions are tracked.
How does orchestration differ from workflow automation?
Automation performs a defined task, such as sending a questionnaire or issuing a reminder. Orchestration coordinates the wider assessment and response, using risk intelligence and business rules to determine the relevant steps, participants and connected systems.
Can Exiger work with our existing procurement and risk systems?
Exiger’s API supports sharing data and workflow outputs with customer systems. Bidirectional integrations with systems such as SAP, Coupa, Salesforce and ServiceNow embed risk intelligence and automated actions into the enterprise workflows your teams already use.
How do we control AI agents?
Your team sets the workflow, permissions and review points. Agents can assist with alert triage, evidence review and task execution within those controls. Users can inspect the supporting evidence, review recommendations and choose the appropriate response–or delegate it to agents operating within your pre-determined guardrails.
Can different business units or regions use different risk rules?
Yes. Groups, roles and configurable risk models allow teams to apply different risk settings and access permissions. This supports regional or business unit requirements while allowing authorized users to see relevant exposure across the organization.
Can we extend workflows around our own program?
Yes. You can configure workflows, questionnaires, risk models and agents around your processes. Exiger’s implementation teams can also help connect your data and enterprise systems. Build with Exiger on the intelligence and controls already in the platform.
Discuss Your Orchestration Requirements →
Solutions for Your Wider Risk Program
1EXIGER.AI
Explore the platform connecting proprietary intelligence, organizational data and AI agents across risk, compliance and operating teams.
Third-Party Risk Management
Connect risk intelligence to assessments, approvals and remediation across functions and enterprise systems.
Supply Chain
Map supplier dependencies and assess the risks affecting parts, products and operational continuity.
Software Supply Chain Security
Assess software suppliers and components, trace provenance and monitor exposure across your software portfolio.
Third-Party Risk Perspectives