Introduction
As previously explored, the Digital Operation Resilience Act (DORA) has an exhaustive set of complex requirements that cover information and communication technology (ICT) risks within the financial sector and their critical third-party technology service providers.
Failure to comply leads to significant fines that can go up to 1,000,000 Euros for financial entities and up to 5,000,000 Euros for critical third-party technology providers.
It is crucial for financial services and third-party providers to comprehensively manage their ICT risks to ensure DORA compliance. In this article, we delve deeper into the Exiger capabilities and solutions that can meet DORA requirements.
Detecting Anomalous Activities
DORA requires that financial entities develop a comprehensive ICT risk management framework that identifies, assesses, and mitigates ICT risks. Under Article 10, this includes having mechanisms to promptly detect anomalous activities, including ICT network performance issues and ICT-related incidents.
Financial entities are required to have mechanisms to promptly detect anomalous activities in accordance with DORA Article 17 . To address this issue, it’s critical for organizations to have three capabilities:
-
SBOM Generation and Analysis:
- Generate and analyze SBOMs (Software Bills of Materials) to detect anomalies in software supply chains, even without source code.
- Verify the completeness and accuracy of SBOMs and validate internal or third-party SBOMs.
- Identify single points of failure, such as components maintained by single committers or projects at the end of life.
-
Continuous Monitoring:
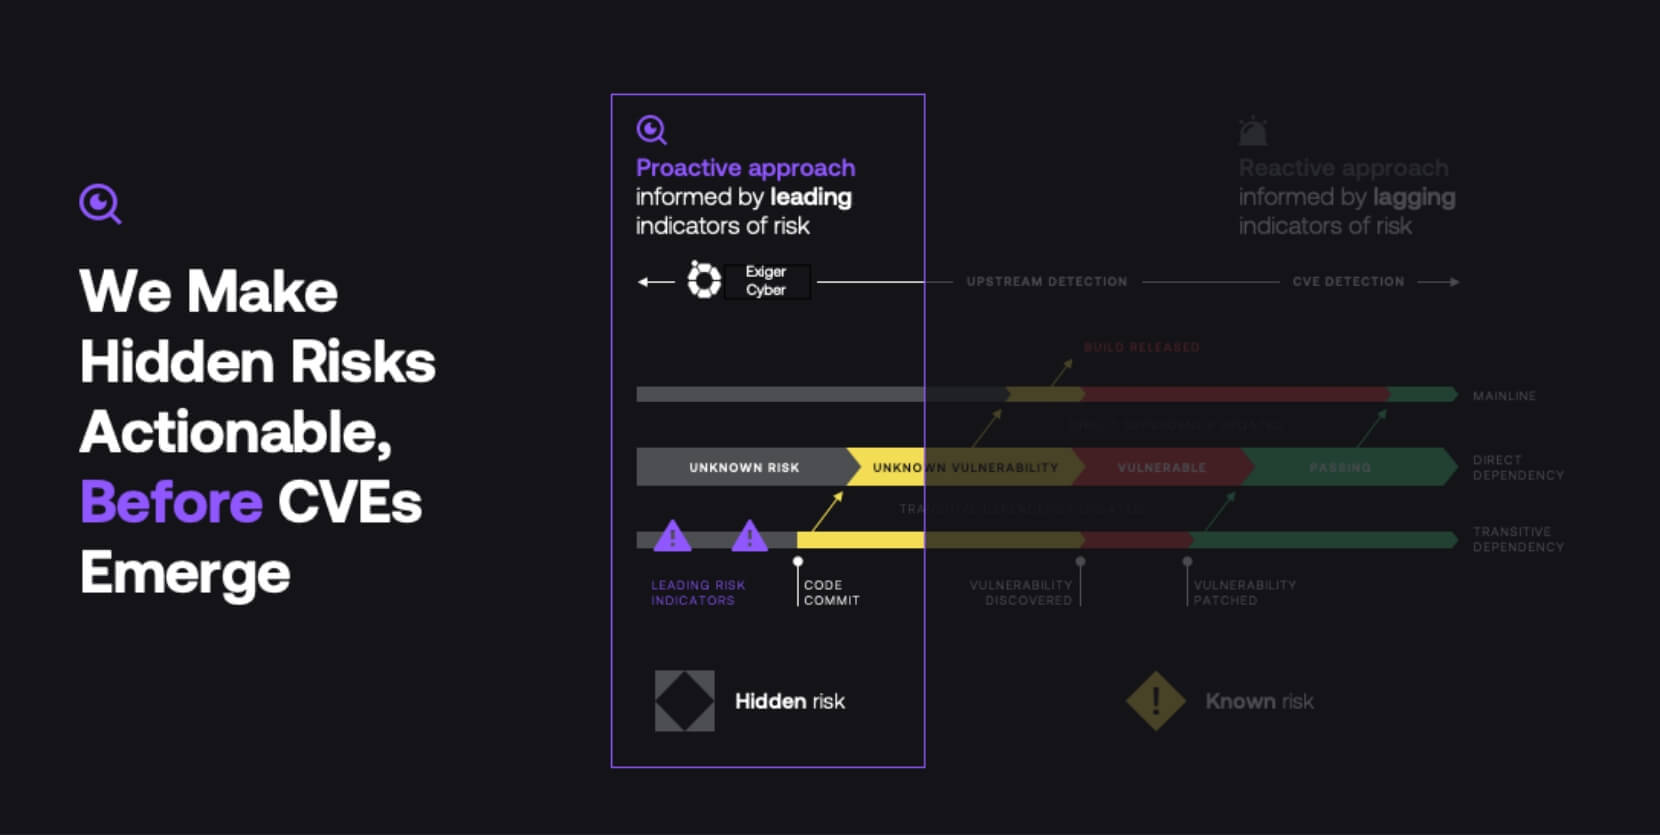
- Monitor software components and associated risks continuously, including known vulnerabilities (CVE) and proactive identification of risks ahead of public disclosures.
- Identify high-risk contributors, such as contributions from developers associated with adversarial organizations.
-
Proactive Incident Detection:
- Detect anomalies in the chain of custody of software components, identifying indicators of sabotage or hidden risks (e.g., malware, grenade-ware) before vulnerabilities become known.
- Integrate alert thresholds to monitor and classify vulnerabilities for immediate escalation.
How to Meet Them with Exiger:
Exiger’s capabilities focus on comprehensively detecting vulnerabilities and risks within software supply chains. By leveraging tools such as SBOM generation, binary analysis, and continuous monitoring, financial entities can identify anomalous activities proactively, such as:
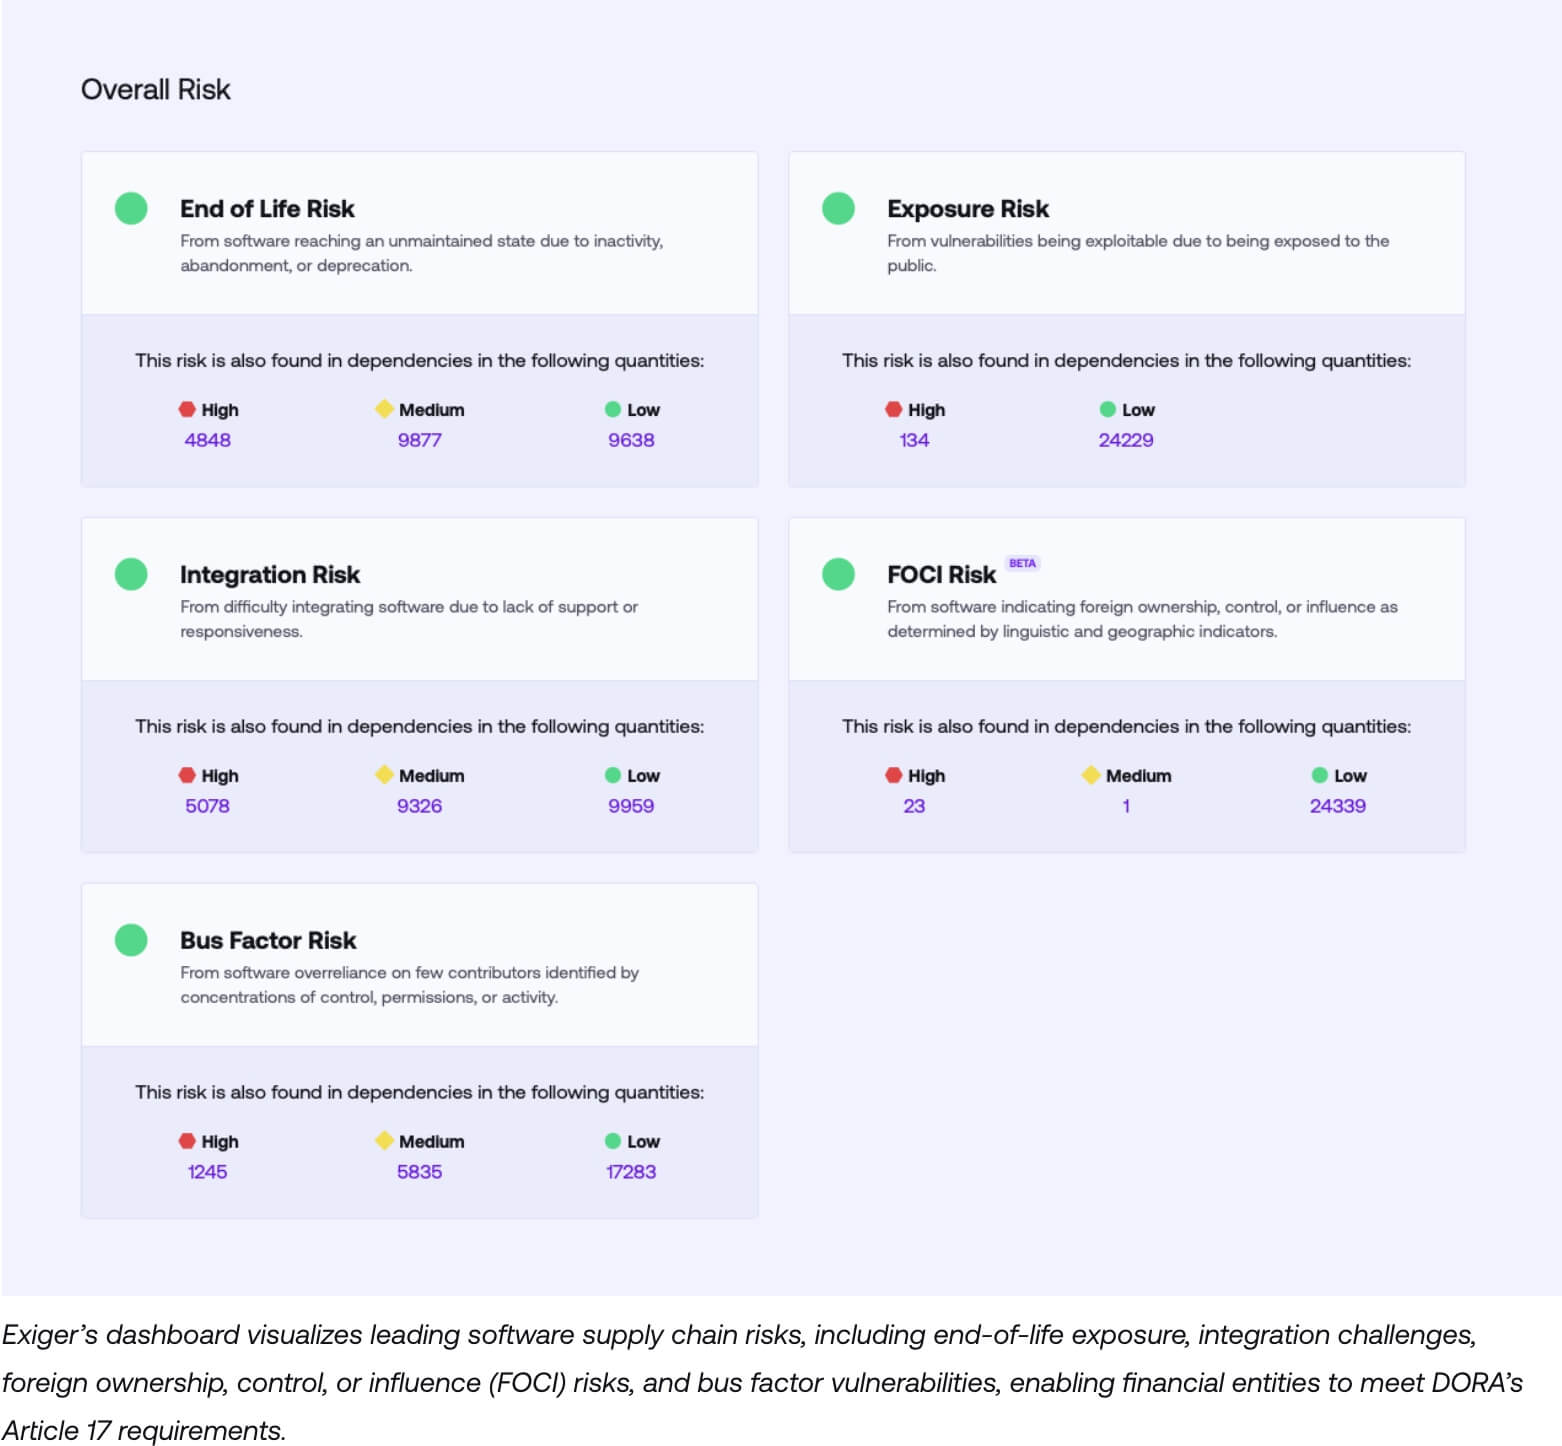
- Single Points of Failure: Identifying end-of-life components, single-committer projects, or abandoned software helps entities address critical weaknesses before they lead to disruptions.
- Proactive Risk Indicators: These tools detect leading risk indicators, such as anomalies in software lineage or contributions from high-risk sources (for example, developers affiliated with sanctioned entities), months before they are reflected in public vulnerability disclosures.
Regular updates and automated alerts help ensure mechanisms remain functional and effective over time. This aligns with DORA’s requirement to test detection mechanisms regularly, as stipulated in DORA Article 25 .
Impact:
Financial institutions can reduce operational and cybersecurity risks by pinpointing weaknesses in their ICT networks early. By addressing these risks before they escalate, entities build resilience and fulfill DORA’s requirement to identify critical risks and single points of failure.
The detection mechanism referred to above must have multiple layers of control and define alert thresholds and criteria to trigger and initiate ICT-related incident response processes. This includes automatic alert mechanisms for the staff in charge of ICT incident responses.
For this, it’s important for financial entities to have:
- Automated alert mechanisms to ensure timely notifications to relevant staff, with thresholds and criteria embedded in workflows for ICT-related incident response.
- Integration of proactive detection techniques to identify incidents such as grenade-ware or supply chain risks faster than traditional methods.
How to Meet Them with Exiger:
Exiger enables financial entities to implement layered detection and response controls by offering advanced monitoring capabilities. This includes:
- Defined Alert Thresholds
With real-time alerts and customizable thresholds, Exiger can ensure risks are escalated as needed.
- Proactive Alerts and Actionable Context of Threats
This helps ensure that the response processes are timely and effective, while automated alerts minimize reliance on manual oversight.
Additionally, Exiger can deliver ongoing, in-depth monitoring of software risks, addressing DORA’s mandate for sufficient resource allocation in this area. Key functions include:
- Continuous Monitoring: Real-time tracking of software components, including both known vulnerabilities and predictive risks, ensures that anomalies are detected even before they’re known.
- Holistic Coverage: The platforms cover software risks across IT, OT, and IoT environments, enabling comprehensive visibility into software risk for any part of a network.
- Focus on Cyber-Attacks: By analyzing patterns such as malware propagation, supply chain sabotage (e.g., grenade-ware), and poor software hygiene, the tools help entities anticipate and counter cyber threats effectively.
Impact:
By embedding these capabilities into their operational workflows, financial entities can ensure a robust and swift response to incidents, preventing minor issues from escalating into major disruptions. This ensures compliance with DORA’s need for layered controls and integrated incident response mechanisms.
Continuous, in-depth monitoring with Exiger also ensures that financial entities maintain an up-to-date and detailed view of the software that makes up their ICT environments. By dedicating resources to proactive monitoring, they can better identify, classify, and mitigate ICT anomalies and cyber threats, thereby strengthening their resilience to evolving risks.
Protection and Prevention
Under DORA Article 9 of DORA, ICT systems are required to continuously monitor and control the security and functioning of ICT systems and tools. They also need to minimize the impact of ICT risk on ICT systems through the deployment of ICT security tools, policies, and procedures.
Additionally, financial entities need to design, procure, and implement ICT security policies and tools to ensure the resilience and continuity of these systems.
To ensure this, it’s crucial for financial entities to have:
- Real-Time Risk Awareness: Continuous monitoring and proactive detection ensure financial entities stay ahead of vulnerabilities, reducing the likelihood of ICT disruptions.
- Integrity and Security: SBOMs and binary analysis that provide high confidence in the authenticity and integrity of the components in ICT systems.
To address the challenge of continuously monitoring and controlling the security of ICT systems and tools, financial entities will need the following capabilities:
-
Continuous Monitoring of ICT Systems and Supply Chains
- Through this, Exiger can detect risks such as vulnerabilities, end-of-life components, and supply chain fragility.
-
Proactive Detection
- Lets organizations identify and prioritize risks before they become public vulnerabilities, enabling critical early intervention.
-
Binary Analysis
- Generate an SBOM that can then be analyzed and validated to verify the integrity of software components, thus reducing risks associated with poor coding practices or hidden sabotage.
Impact:
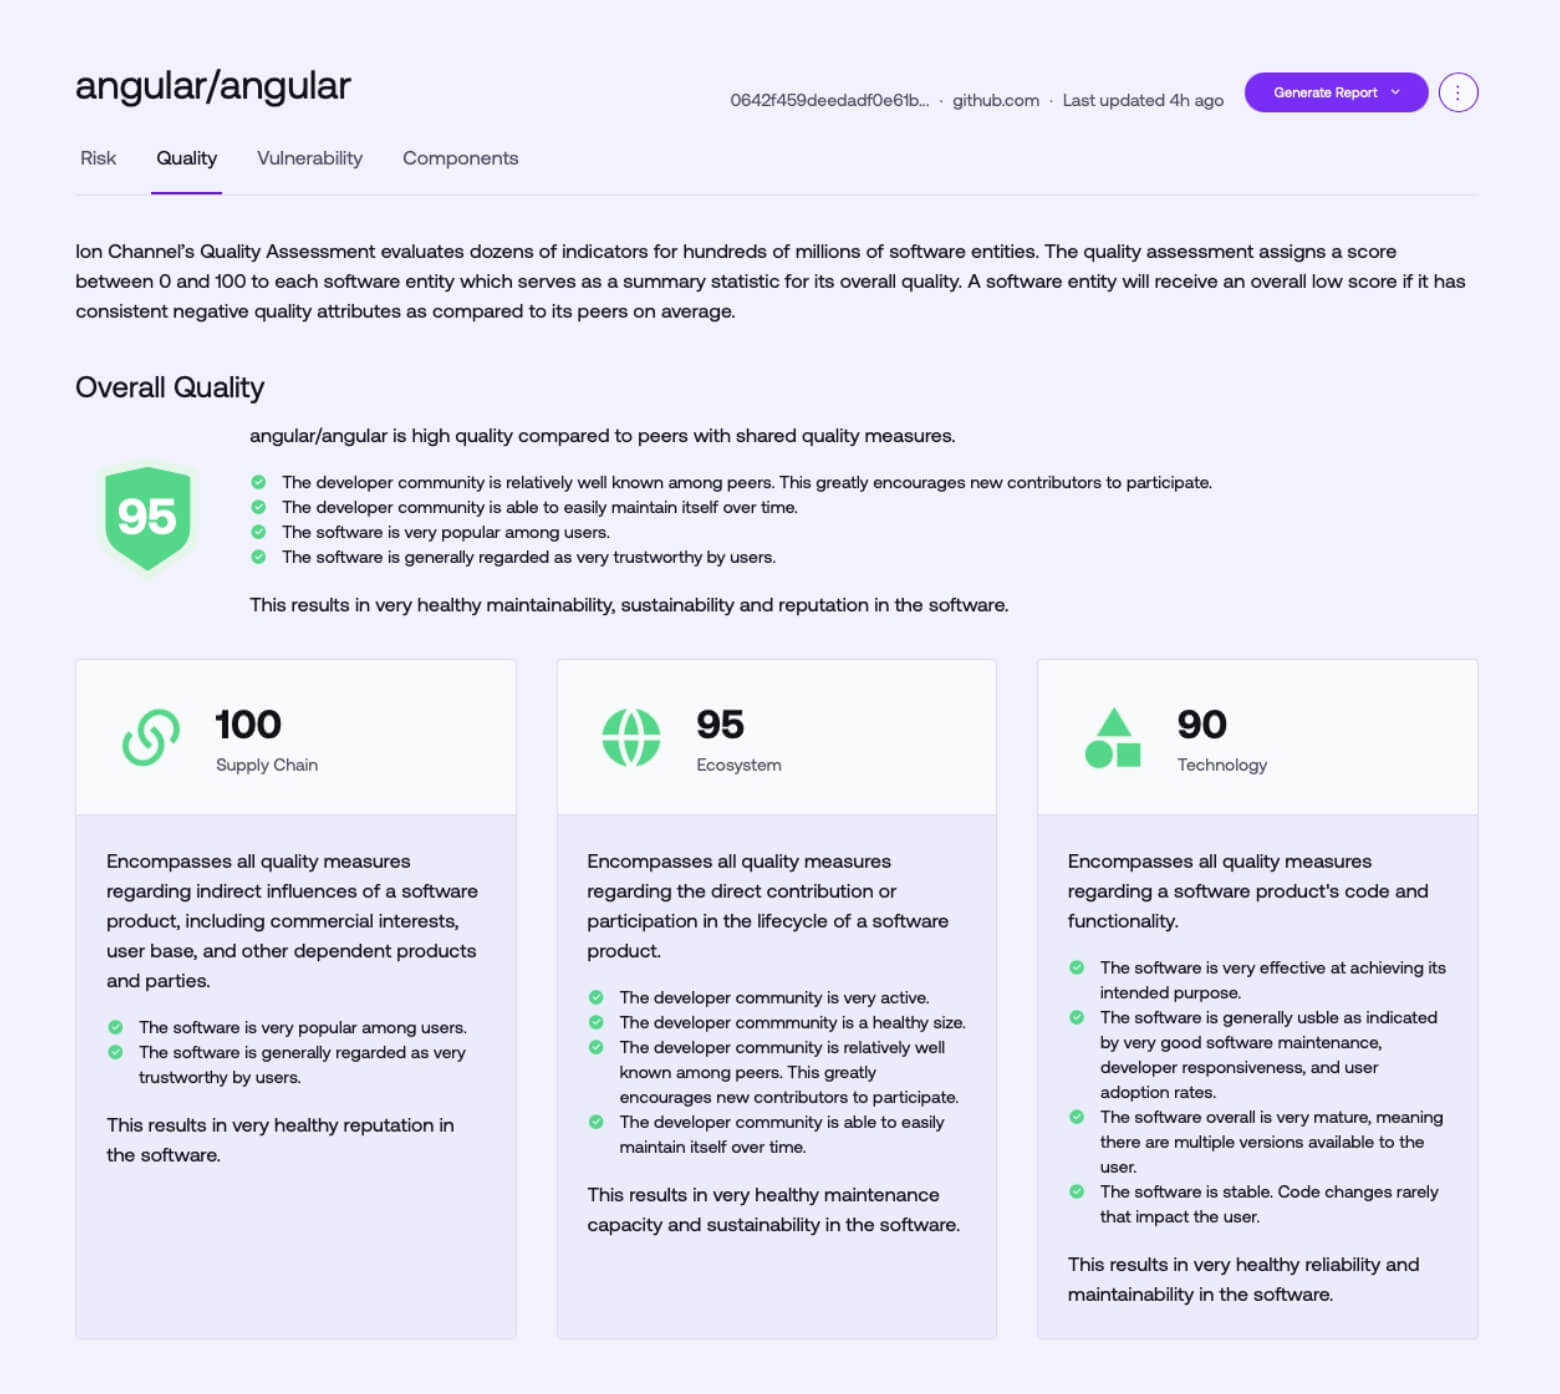
Continuous monitoring allows financial entities to maintain a real-time understanding of their ICT systems’ security posture. This proactive approach minimizes the impact of ICT risks by detecting potential vulnerabilities early and ensuring they are addressed promptly, directly fulfilling Article 9, Paragraph 1 for DORA.
To help ensure that financial entities meet the DORA requirements for their ICT security policies and tools, Exiger provides the following capabilities:
- SBOM Generation and Verification: Ensures software’s integrity, authenticity, and confidentiality by providing detailed component pedigree and provenance.
- Risk-Scored Processes: Incorporates risk scoring into ICT solutions, ensuring critical systems are prioritized for protection.
- Supply Chain Transparency: Analysis shows all software components within a system and identifies risky components in the software supply chain, such as unmaintained projects or contributors from adversarial nations.
- Validation of SBOM Integrity: Exiger analyzes all components of an SBOM via binary analysis that provides the ability to detect malware, grenade-ware, and wiper-ware.
Impact:
Through these capabilities, financial entities can implement ICT tools and protocols that maintain high standards for data security, resilience, and continuity. By integrating validated SBOMs, Exiger addresses the DORA requirements for ICT system reliability.
Identification of ICT-Supported Functions
As part of the ICT risk management framework referred to in DORA Article 6 of the DORA, financial entities are required to identify, classify, and adequately document all ICT-supported business functions, roles, and responsibilities.
DORA Article 8 goes into detail on what this identification process entails, which includes identifying sources of ICT risks and conducting risk assessments. On top of that, entities are also expected to identify and document processes that are dependent on third-party service providers.
To meet the requirements under Article 8, financial entities would require capabilities that include:
- Proactive Risk Monitoring: Continuous identification of threats and vulnerabilities reduces the likelihood of ICT disruptions and improves risk visibility.
- Third-Party Assurance: Tools for mapping dependencies and risks tied to third-party providers ensure compliance with critical function documentation requirements.
- Legacy System Security: The capability to generate SBOMs from software binaries and then analyze them to find vulnerabilities, including if they’re deprecated, have been acquired by other companies, or are no longer supported. Financial institutions don’t need to depend on third parties in order to understand the composition or risk of their software.
DORA requires the identification, classification, and documentation of key ICT assets. Financial entities also need to review (as needed and at least yearly) the adequacy of this classification and any relevant documentation.
How to Meet Them with Exiger:
Ensuring an accurate, updated catalog of ICT functions will be critical here. Exiger helps with these three crucial capabilities:
Exiger enables financial entities to implement layered detection and response controls by offering advanced monitoring capabilities . This includes:
- Discovery : Exiger’s platforms enable automated discovery and classification of software components within ICT assets, including proprietary and open-source libraries and dependencies.
- Mapping Roles and Dependencies : Exiger provides insights into the relationships between different software components, helping to uncover unknown risks like anomalies in the chain of custody, contributions from known bad actors, and FOCI risk from adversarial nations or sanctioned entities and documenting these dependencies for business-critical operations.
- Periodic Review Mechanisms : Continuous monitoring of all the components to ensure inventories are updated in real-time so that they can be reviewed at least yearly, meeting regulatory standards.
Impact:
These capabilities ensure financial entities maintain an accurate and up-to-date catalog of all ICT-supported functions, roles, and responsibilities. By documenting interdependencies and risks, entities can easily comply with DORA’s requirement to classify and review ICT assets and their documentation annually.
Paragraph 2 of Article 8 stipulates that financial entities shall, on a continuous basis, identify all sources of ICT risk, in particular, the risk exposure to and from other financial entities. They are also required to assess cyber threats and ICT vulnerabilities deemed relevant to their ICT-supported business functions, information assets, and ICT assets.
How to Meet Them with Exiger:
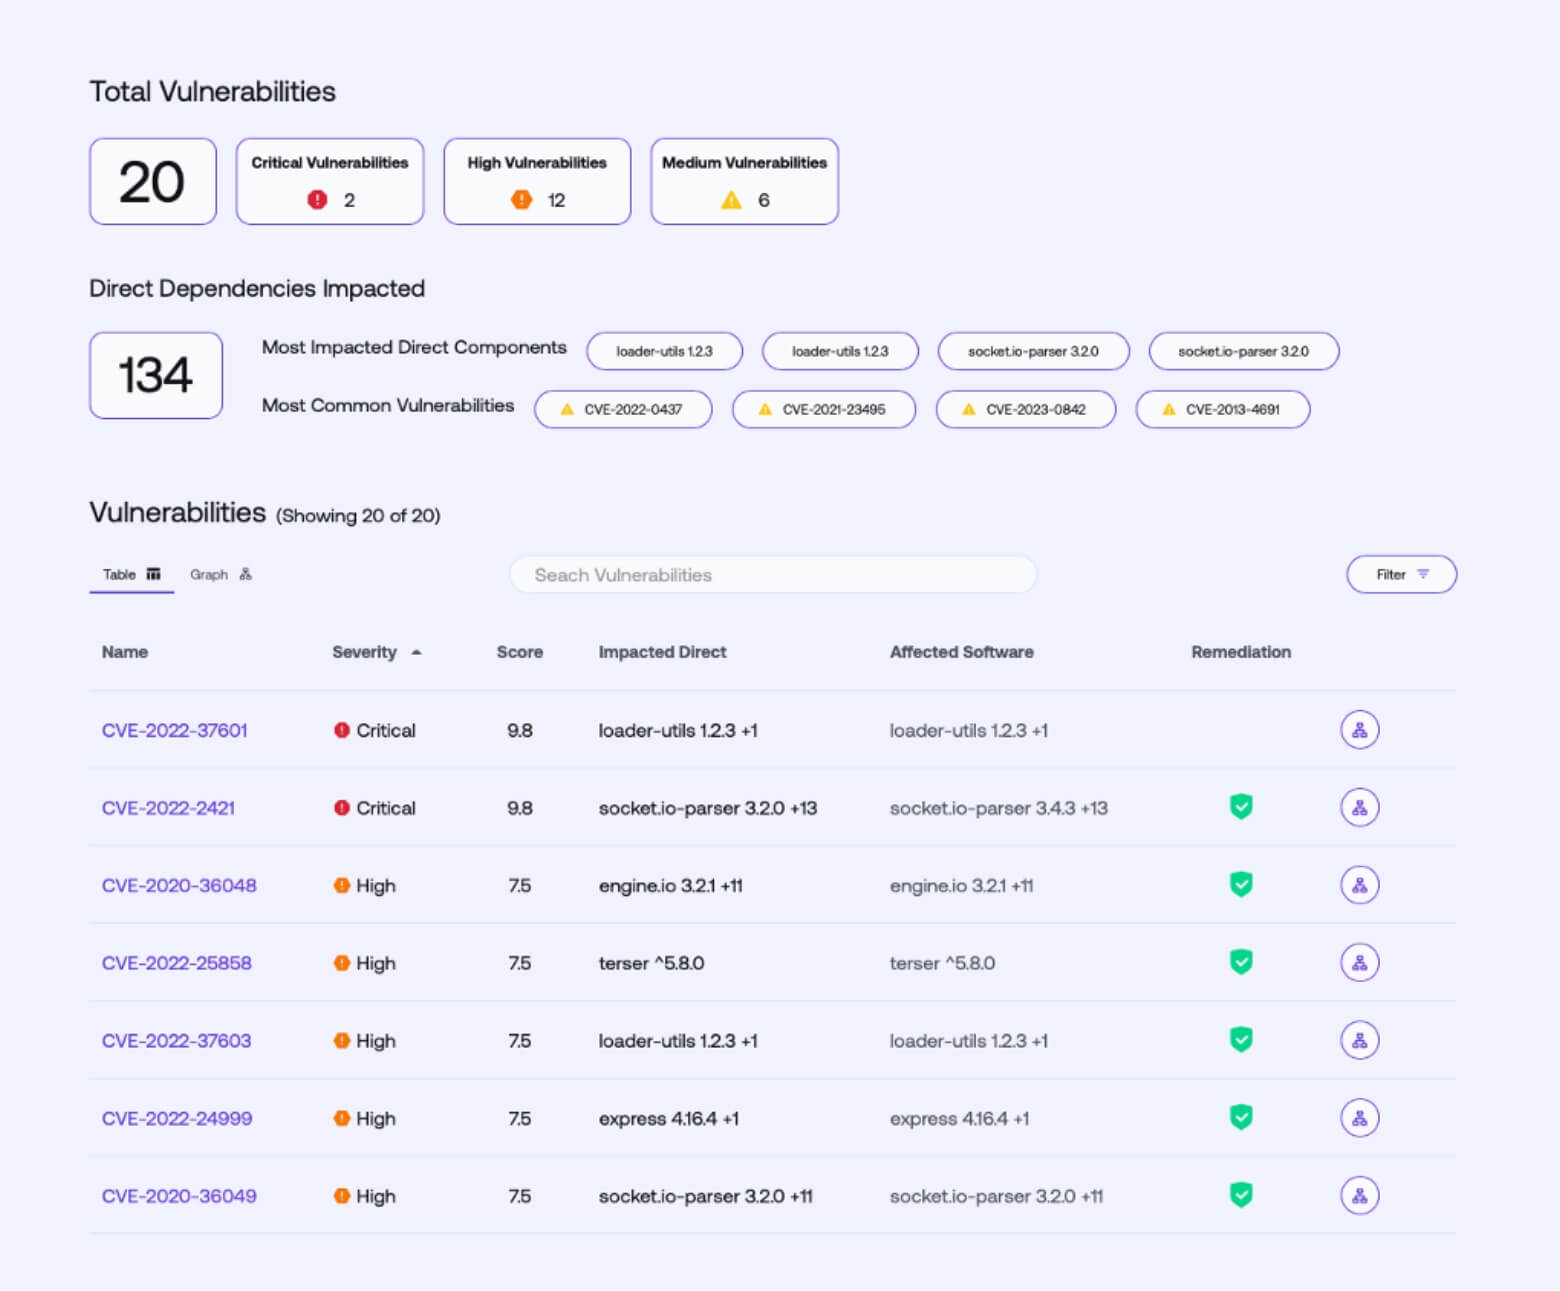
Exiger’s Continuous Monitoring capabilities will continuously identify ICT risks by analyzing vulnerabilities, cyber threats, and potential exposure to other financial entities.
Impact :
With real-time monitoring, financial entities can identify and mitigate ICT risks promptly. This fulfills DORA’s requirement for continuous risk identification, enhancing resilience against evolving threats.
Another DORA requirement is for financial entities to identify all information and ICT assets (including those on remote sites, network resources, and hardware equipment) and then map those considered critical.
How to Meet Them with Exiger:
Two of Exiger’s capabilities will be tremendously useful in this situation:
- Configuration Mapping : Exiger’s platforms map the configurations of ICT assets, identifying critical components and their interdependencies.
- Legacy System Analysis : Specific tools address risks in legacy systems by mapping their connections and dependencies.
Impact:
Detailed mapping of ICT asset configurations allows financial entities to pinpoint critical systems and understand how failures might propagate through dependencies. This ensures compliance with DORA’s requirement for mapping and documenting critical ICT assets.
Financial entities must conduct, at least annually, a specific ICT risk assessment on all legacy ICT systems, as well as applications or systems before and after connecting technologies.
How to Meet Them with Exiger:
This is where third-party risk management comes in. Exiger provides scalable solutions designed to arm compliance teams with the tools they need. Crucial capabilities for these requirements include:
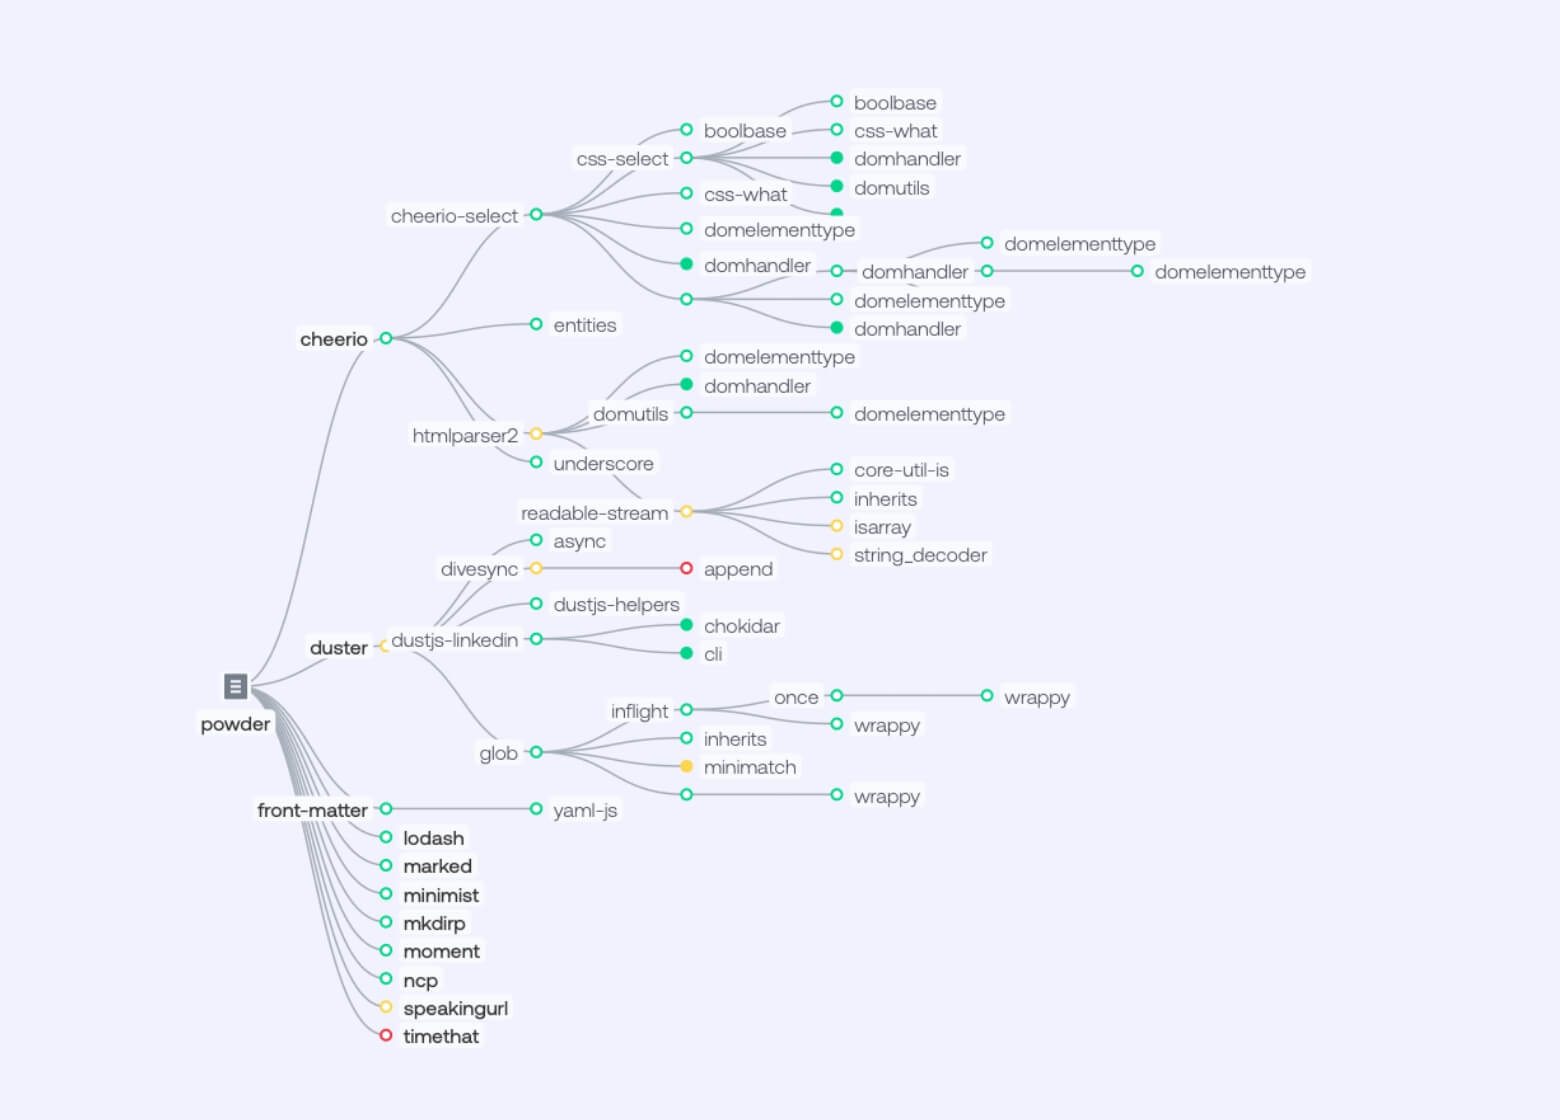
- Third-Party Risk Management : Automated workflows and SBOM analysis are used to identify all dependencies on ICT third-party service providers, including critical functions supported by these providers.
- Interconnection Insights : Exiger provides visibility into dependencies and interconnections with third-party software components and libraries and assesses risks posed by these dependencies.
Impact:
With comprehensive third-party risk assessments, financial entities can easily ensure documentation of all processes reliant on ICT service providers. This meets DORA’s requirement to identify and document interdependencies with third-party providers.
Financial entities must, and at least once a year, conduct a specific ICT risk assessment on all legacy ICT systems and applications or systems.
How to Meet Them with Exiger:
- Legacy System Risk Analysis : Exiger offers specialized tools to assess vulnerabilities in legacy ICT systems, including those that don’t have SBOMs available. When there is no SBOM, Exiger can generate one from software binaries.
- Continuous Monitoring of Legacy Systems : Regular updates ensure legacy systems are monitored for new risks, such as emerging vulnerabilities.
Impact:
By targeting legacy systems specifically, these capabilities enable financial entities to conduct regular risk assessments and ensure that connecting technologies do not compromise overall system security.
Conclusion
Even for financial entities and organizations adhering to best industry practices and standards, the DORA Act is not something to be underestimated. As we’ve observed in Exploring DORA, the act is robust and complex and requires the right technology to ensure due diligence and compliance.
Overall, Exiger offers robust solutions that align closely with DORA requirements, particularly for legacy systems, risk assessment, and third-party dependency mapping. These capabilities provide financial entities with the transparency of their software supply chain needed to build resilience and maintain compliance. To learn more about how the 1Exiger platform can help address your DORA requirement gaps, please request a demo.