By Bob Kolasky, Exiger Senior Vice President of Critical Infrastructure
Bob Kolasky previously served as Assistant Director for Cybersecurity and Infrastructure Security Agency (CISA) within the Department of Homeland Security (DHS), where he led the National Risk Management Center (NMRC).
The National Institute of Standards and Technology (NIST) issued updated cybersecurity supply chain risk management guidance via NIST Standard Publication 800-161 in May 2022. Exiger applauds NIST’s continued leadership in cybersecurity supply chain risk management (C-SCRM) and urges all critical infrastructure organizations to adopt the guidance and build it into their enterprise risk management processes as “fundamental to any effort to manage risk exposure arising from enterprise operations.”
In its guidance, in part a response to Executive Order 14028, NIST outlines C-SCRM as “a systematic process that aims to help enterprises manage cybersecurity risks throughout the supply chain. Enterprises should identify, adopt, and tailor the practices described in this document to best suit their unique strategic, operational, and risk context.”
What is worth emphasizing in that description is that supply chain risks and vulnerabilities are not managed for their own sake but instead need to be accounted for as key practices in achieving business objectives. This means that business processes moving forward have to involve not just security and risk professionals but also business owners as well as those responsible for acquisitions and human capital teams.
Ultimately, the implementation of an effective NIST cybersecurity framework is accomplished when organizational elements come together to bring criticality analysis to bear, to ensure that supply chains aren’t presenting a cyber risk on top of other business objectives. Because of that, the governing of risk and the development of a culture of risk management are important elements of a C-SCRM program.
As NIST author Jon Boyens rightly notes:
To successfully address evolving cybersecurity risks throughout the supply chain, enterprises need to engage multiple internal processes and capabilities, communicate and collaborate across enterprise levels and mission areas, and ensure that all individuals within the enterprise understand their role in managing cybersecurity risks throughout the supply chain.
The technical process of supply chain risk mitigation is a key element of achieving that success, and it includes the key step of having proper risk assessment, which is core to the support that Exiger provides to federal agencies and business entities in supply chain risk.
How to Comply with NIST Guidance
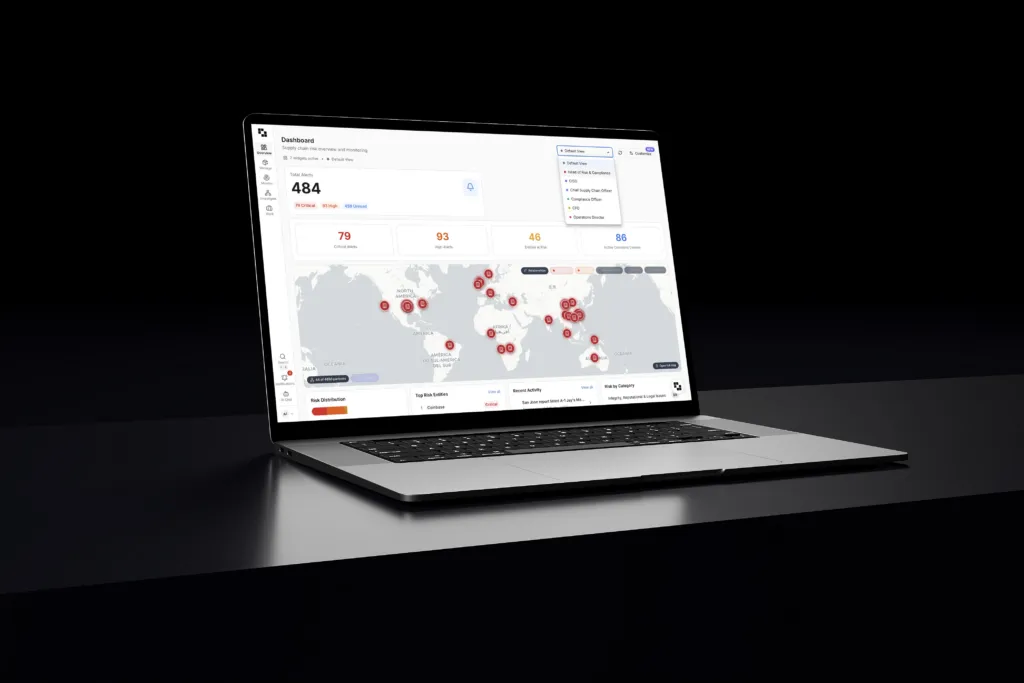
Automating your risk management workflow is critical to reaching all levels of NIST guidance. Our Supply Chain Explorer tool allows entities to have visibility to the cybersecurity SCRM risks which NIST calls out, to include insider, foreign ownership and control, software flaws, counterfeit goods, and supplier third party risk. By integrating thousands of data sources into one ecosystem, and surfacing unseen relationships, Supply Chain Explorer assesses and prioritizes risks of concern. By doing this effectively, companies can execute the subsequent parts of the guidance of responding to and monitoring risks.
While Exiger’s core service offerings help companies achieve the NIST identified “foundational practices” for a C-SCRM program, our offerings go further than supply chain security and can help companies get to sustaining and enhancing practices in the spirit of continuous improvement against cyber attacks.
For example, our analytic capability as both information security and an information system supports near continuous monitoring and reassessment of suppliers and supplied products so as to enable a dynamic SCRM program. So, too, can we help apply insights from C-SCRM metrics to enable more predictive monitoring of risk management activities. It is through cutting edge analytics and utility of big data that companies and their stakeholders can achieve the visibility needed to proactively manage supply chain risks.
Get Cyber Supply Chain Risk Management with Exiger
NIST’s work to update 800-161 and to outline how entities can establish C-SCRM programs is timely. As businesses and government continue the movement to increased digitalization and reliance on complex supply chains in their life cycles, it is absolutely essential that critical entities do so in a measured way that does not introduce unnecessary operational and integrity risks into their critical systems.
At Exiger, we are committed to helping companies along that journey and fully support the achievement of the critical guidance offered by NIST. To learn more about our cyber supply chain risk management solutions, please contact us.