When a cyber incident hits an automaker, like many manufacturers, the impact doesn’t always stop at the security operations center.
It can ripple through production lines, tier-1 and tier-N suppliers, dealer networks, logistics, and even local economies. Recent events impacting Jaguar Land Rover (JLR) brought this possible reality into sharp focus: production pauses, controlled restarts, and supplier payment backlogs translated into material disruptions across a vast ecosystem. Public reporting estimates the economic impact for the U.K.-based company in the range of £1.9 billion, with around 5,000 businesses affected across the extended value chain
What happened—and why it matters to supply chains
According to media reports, JLR took prompt action when they discovered the incident, proactively shutting down systems to ensure containment. But implementing a controlled restart plan proved time consuming given the deep integrations between IT and operational technology (OT) systems. The incident caused JLR to make security decisions that impacted operations, and the resulting production pause lasted into late September, affecting their supply chain partners.
For supply chain leaders, the takeaway isn’t about a single company’s response; it’s that digital risk can interrupt physical processes at scale. A single event can cascade into thousands of downstream firms and have significant macroeconomic impact.
The ripple effects are real — and compounding
For JLR, the production pauses cascaded into delayed orders and cash-flow stress for its small and mid-sized suppliers, affecting thousands of businesses. These are not abstract risks; they show up in missed ship dates, expedited freight, idle labor, and strained working capital across the JLR’s supply chain.
The Cyber Monitoring Centre estimates the event caused a UK financial impact of £1.9 billion and affected over 5,000 UK organizations.
Manufacturing is facing growing cyber threats
Verizon’s 2025 Data Breach Investigations Report (DBIR) shows manufacturing’s cyber threat landscape growing more acute. Confirmed manufacturing breaches nearly doubled year-over-year—1,607 this cycle vs. 849 the prior year. System Intrusion remains the top breach pattern (60%), while malware appears in 66% of manufacturing breaches, with ransomware present in 47%. Most actors are financially motivated and external, and espionage-motivated breaches climbed to roughly one in five.
The DBIR also documents the growing role of third parties and software in breaches; third-party involvement was observed in about 30% of all breaches this year—up from roughly 15% last year. In short: the software and service providers your operations run on are now central to resilience.
The Organizational Gap: Cybersecurity and Procurement Still Operate in Silos
Procurement teams excel at cost, quality, and continuity, but may not have the technical backgrounds—or the data—to weigh software and firmware security posture in sourcing decisions. Meanwhile, security teams don’t always map controls to supplier tiering, single-source exposure, or just-in-time realities. And too often, CISOs and supply chain leaders engage only at escalation points. The result: latent software and third-party risks aren’t accounted for in vendor or product selection or in total cost of ownership (TCO), despite clear evidence that vendor and software cybersecurity postures belong in the selection and renewal criteria.
Why software supply chain transparency belongs in procurement
Procurement should be equipped to evaluate:
- Vendor cyber resilience and incident history.
- Product security posture—including SBOMs, update cadence, vulnerability management performance, and key control defaults (e.g., MFA by default).
- Component and firmware provenance, especially for safety-critical systems and connected vehicle components.
The DBIR’s analysis of recent mass-impact campaigns shows how control defaults and poor credential hygiene at third-party platforms can become single points of failure at scale. Folding these factors into sourcing decisions ensures cyber risks are properly weighed: a cheaper but insecure product can prove a costly choice if it creates a disruption.
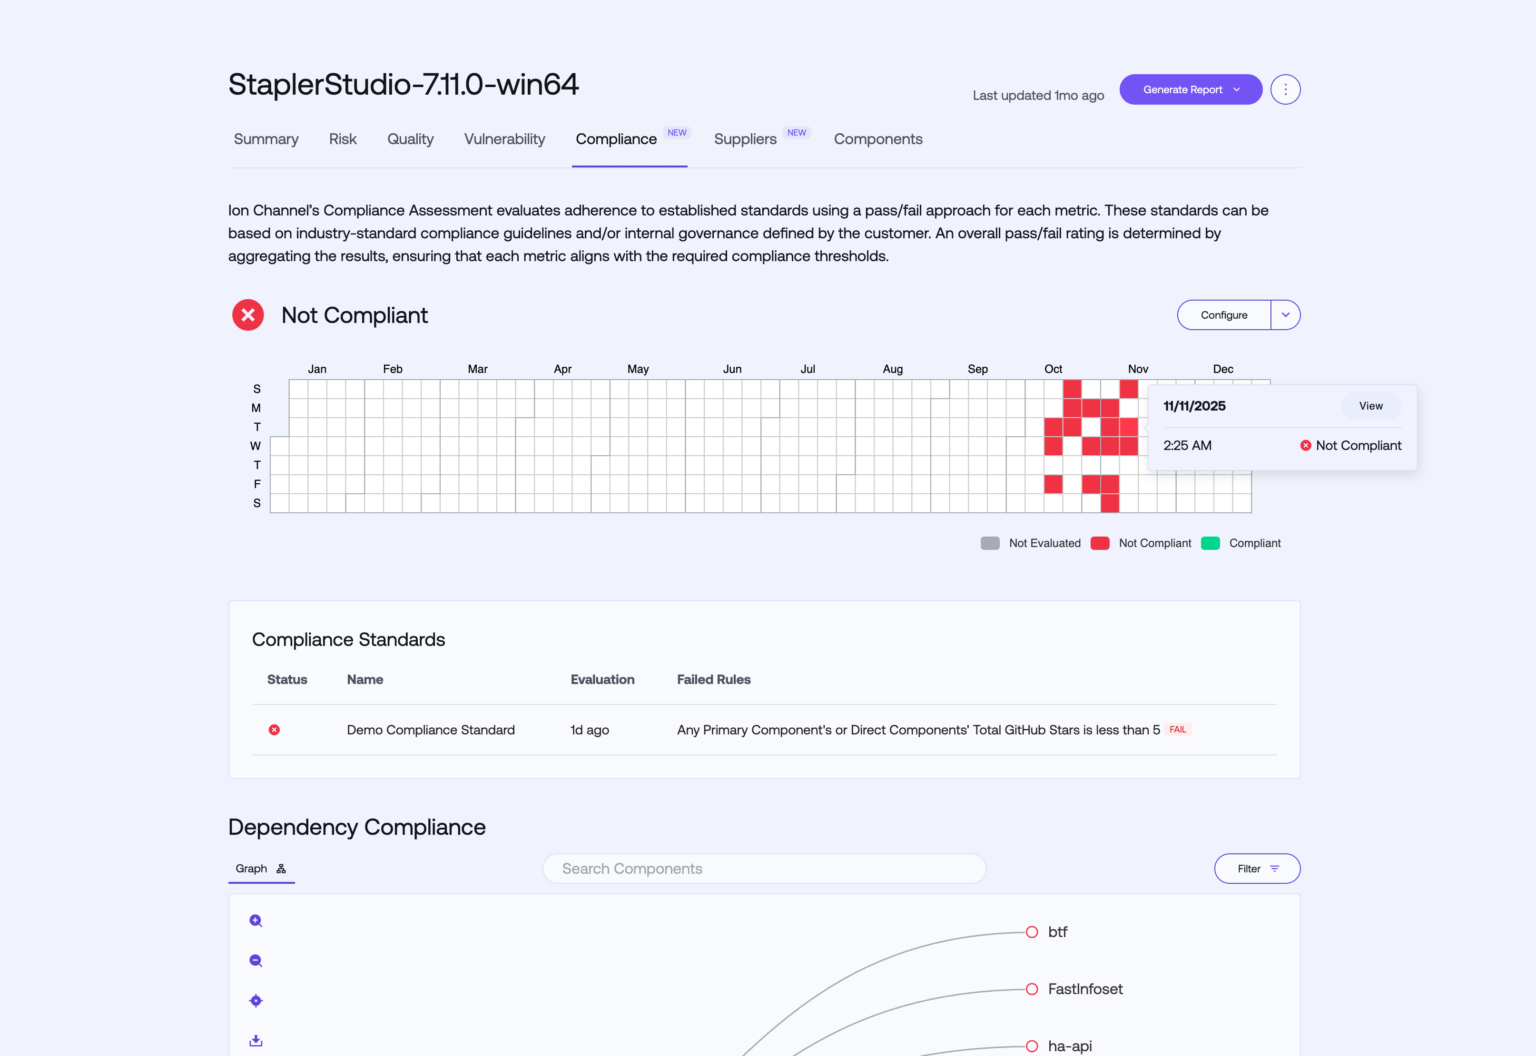

How Exiger Can Be Your Partner in Mitigating Risks
- Before an incident
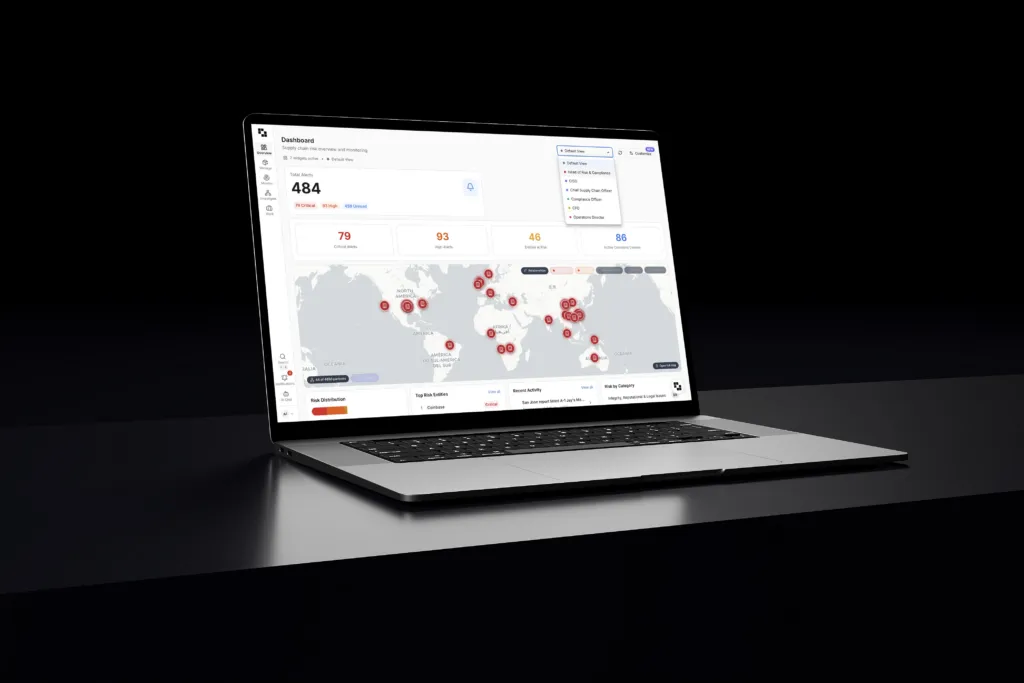
- Unified risk visibility across suppliers, software, and parts. We map supplier criticality to your business and align it with cyber posture and software dependencies—so a high-risk vendor or component is fully visible.
- Security-outcomes-aware procurement. We can help operationalize risk criteria (e.g., secure-by-default, vulnerability management performance, credential policies) into RFPs, renewals, and scorecards, so cyber resilience can be used as a weighted factor in contracts and awards.
- Continuous monitoring and early warning. We track threat activity, exposed secrets, and exploitable edge device issues tied to your supplier landscape to surface action items before they become vulnerabilities that cause outages.
During an incident
- Supplier continuity playbooks. We help prioritize parts and vendors by operational criticality and work with your teams to pre-clear contingency options (approved alternates, safety-stock release, logistics plan changes).
After an incident
- Root-cause to procurement loop. Lessons learned feed directly into sourcing criteria, supplier development, and product security requirements—so fixes persist beyond IT remediation.
- Board-level reporting. Clear metrics tie cyber risk reduction to continuity and revenue protection.
Take a Tour: See the Exiger Software Supply Chain Security Solution in Action
Why Bringing Supply Chain and Software Transparency Under One Roof Helps
Consolidating supply chain, vendor, and software-component visibility with one partner shortens contracting cycles, reduces the cost and complexity of managing multiple tools, and eliminates blind spots created by siloed systems. A true single pane of glass lets leaders see operational, cyber, financial, and compliance risk together—so decisions happen faster and with more context. As programs scale, Exiger Software Supply Chain Security grows with you, maintaining continuity of insight from raw materials and parts to software components, finished products, people, and entities.
What every OEM should be asking themselves right now:
- Does a supplier’s cyber posture— including their product’s software supply chains— face the same scrutiny as quality or cost during evaluation?
- Which of our suppliers and which of their products poses the highest cyber risk, and what mitigations or alternatives are available?
- If a critical supplier suffers a cyberattack, what is our plan? And how quickly can we execute it across parts, plants, and programs to minimize disruption?
An Approach for the Future
- Stand up a joint cyber–procurement governance model with clear ownership, shared tools and metrics, and escalation paths.
- Require software supply chain transparency (SBOMs, secure-by-default controls, patching KPIs) in RFPs and contracts.
- Tier suppliers by operational criticality and cyber exposure, not spend alone; keep alternates warm for single-points-of-failure.
- Run tabletop exercises that simulate both IT and operational impacts—payment pauses, supplier cash-flow stress, alternate-sourcing triggers, and logistics changes.
- Establish pre-approved contingency playbooks to stabilize key suppliers during outages.
The JLR disruption is a reminder that cyber incidents are operational events with financial footprints measured in billions, not just security tickets. JLR reported that their revenue for Q2 2025, impacted by the production stoppages, was down 24% year‑on‑year.
The manufacturers that win the next decade will integrate cyber, software, and supply chain decisions into one operating picture—and practice responding together before it counts.
Get in touch to request a demo of Exiger’s software supply chain security solution