Major Update to Exiger Software Supply Chain Security Solution background

Major Update to Exiger Software Supply Chain Security Solution

Article
November 17, 2025

Exiger is announcing a major update to its Software Supply Chain Security solution, making it easier for users to manage compliance, understand their suppliers, and keep Software Bill of Materials (SBOM) data current.

Compliance Automation

Users can now set custom rules for evaluating their SBOMs and these are automatically re-evaluated each day. If something changes, for example a change in the compliance standard or in the SBOM itself, the change will be reflected in the daily evaluation.
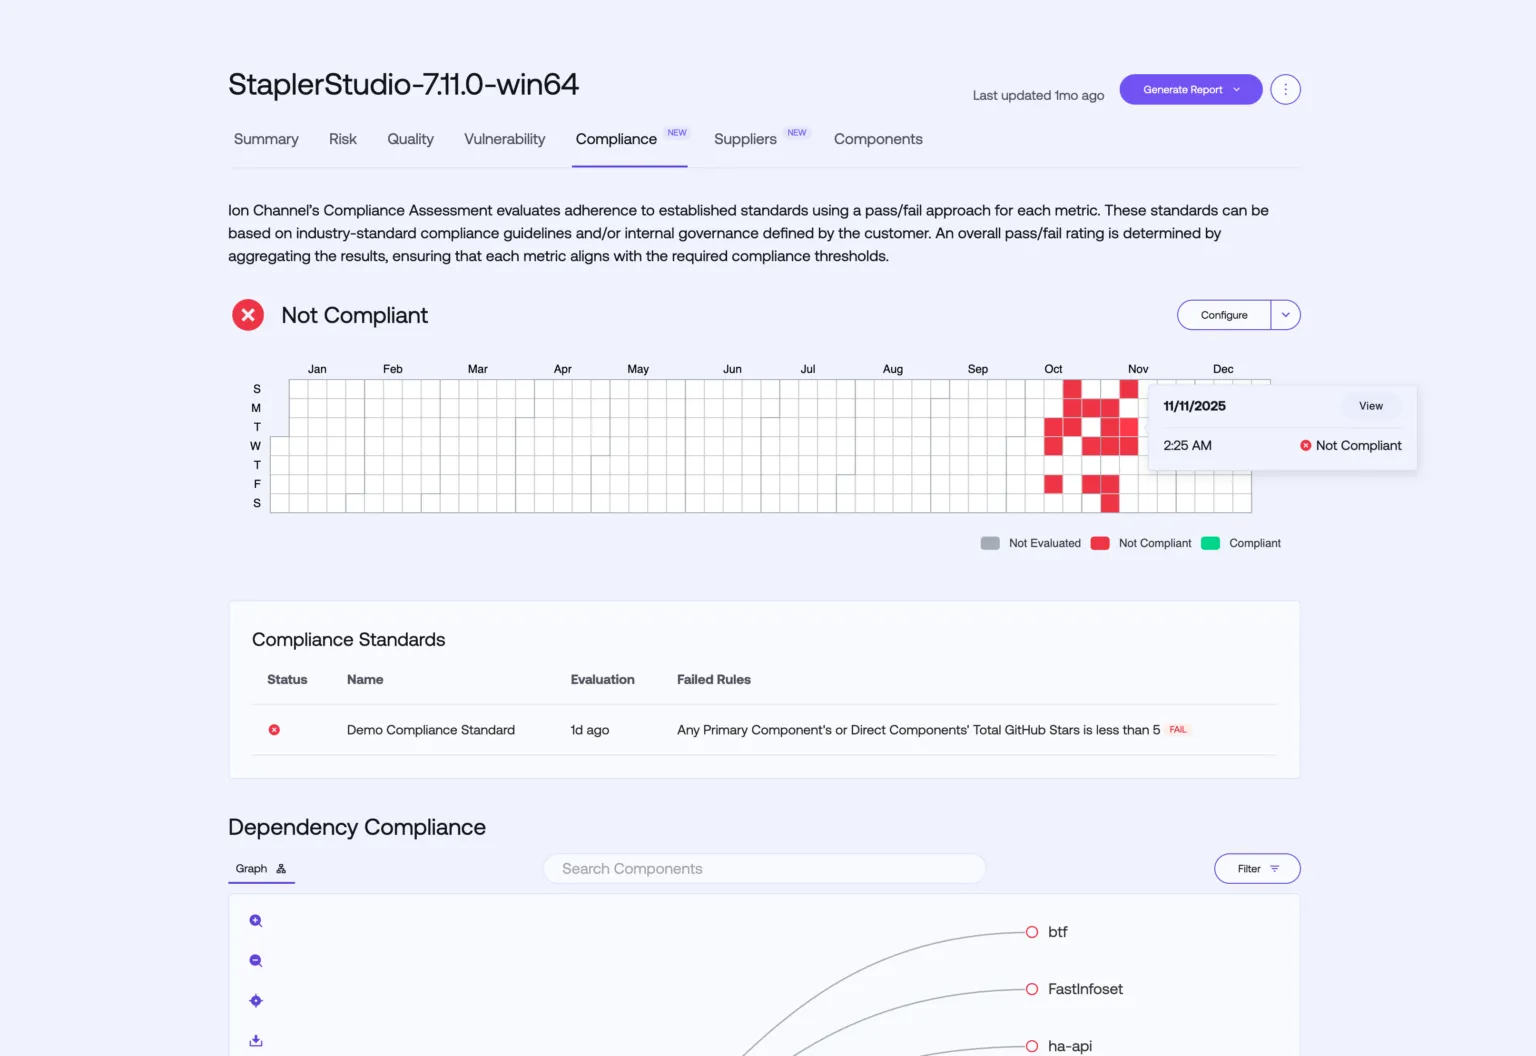
Software compliance assessment dashboard displaying non-compliant components, security rule failures, and dependency risk insights used to evaluate software supply chain security.

Compliance with industry or customer-defined standards is monitored daily basis with clear visualization of compliance status as well as the reason for failure.

We’re also introducing shared compliance standards to automate compliance validation against key cybersecurity frameworks, so clients can stay audit-ready without costly manual reviews. Beginning with our “Exiger Recommended” baseline, we will expand to support existing and emerging standards, including:  

  • EO 14028
  • NIST Minimum SBOM Requirements
  • CISA Minimum SBOM Requirements
  • Cyber Resilience Act (CRA)
  • Trade Agreements Act (TAA)
  • NDAA 889

Expanded Supplier Visibility

Exiger now identifies suppliers at both the SBOM and component levels, providing users a clear picture of who’s behind their software.  This expanded visibility exposes FOCI (Foreign Ownership, Control, or Influence) risks — no matter how deeply embedded the supplier’s software component are.
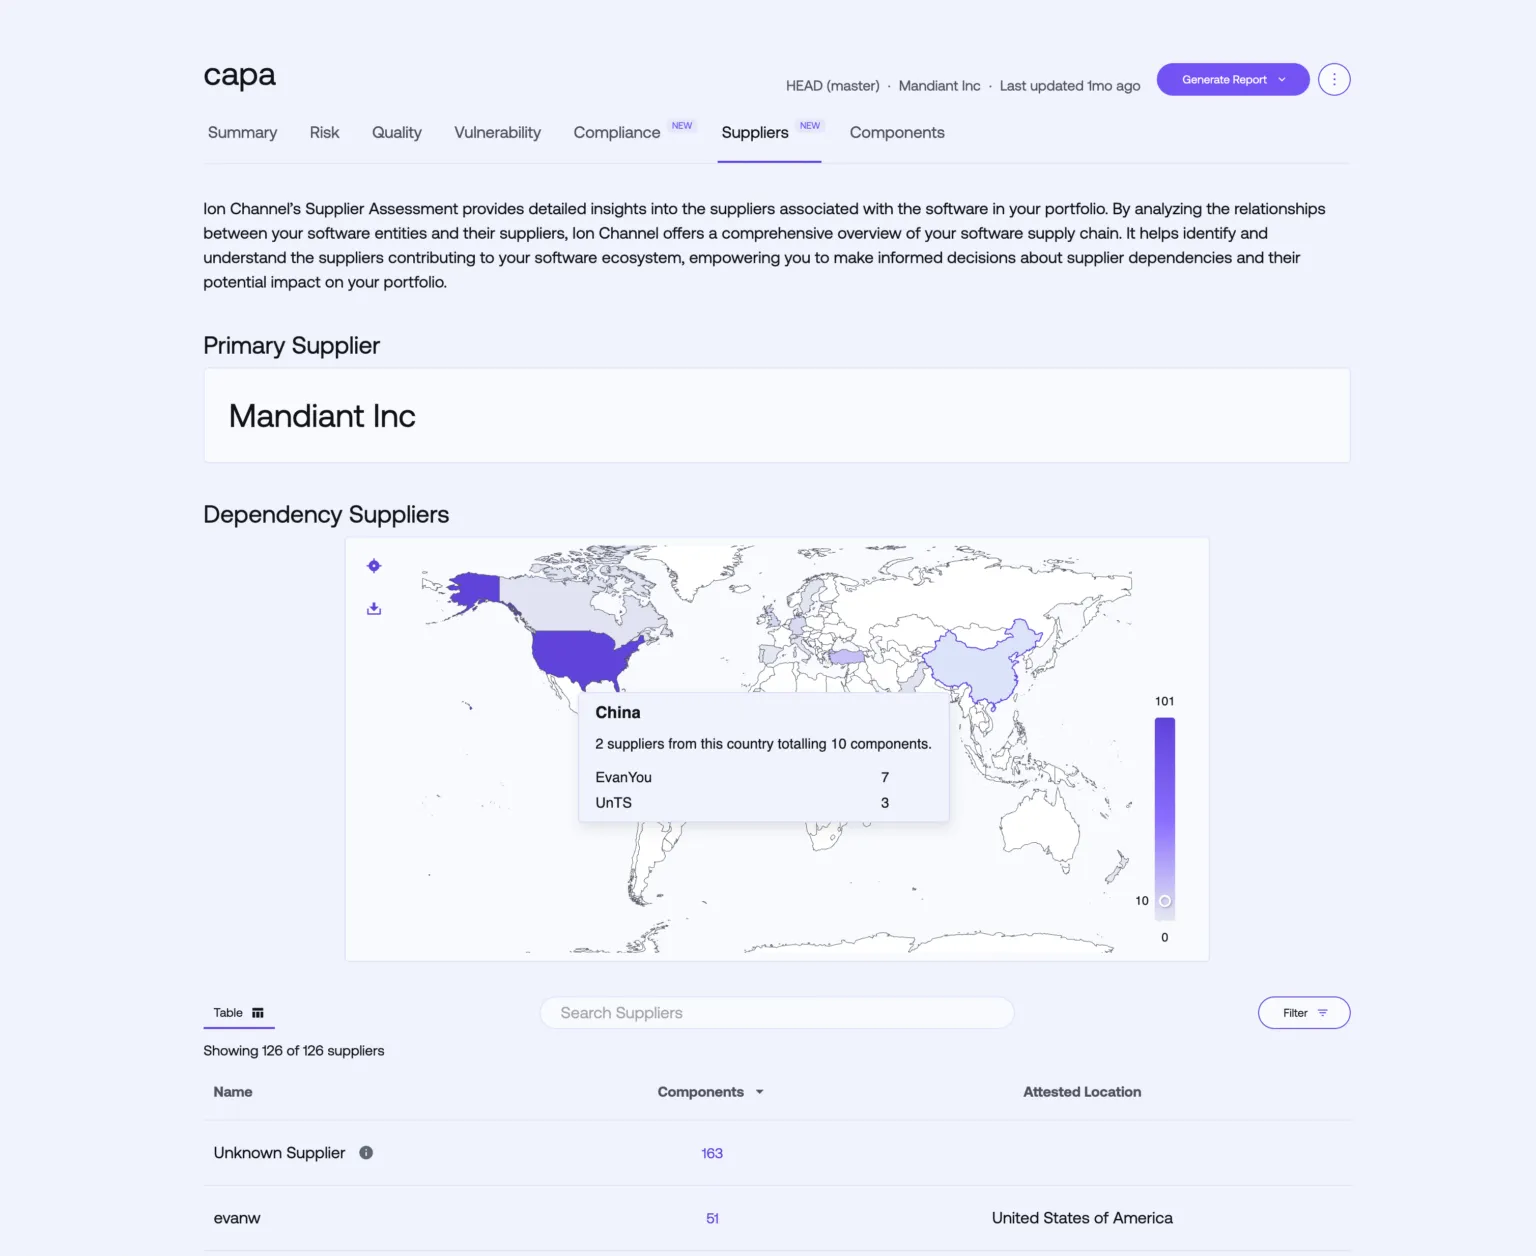
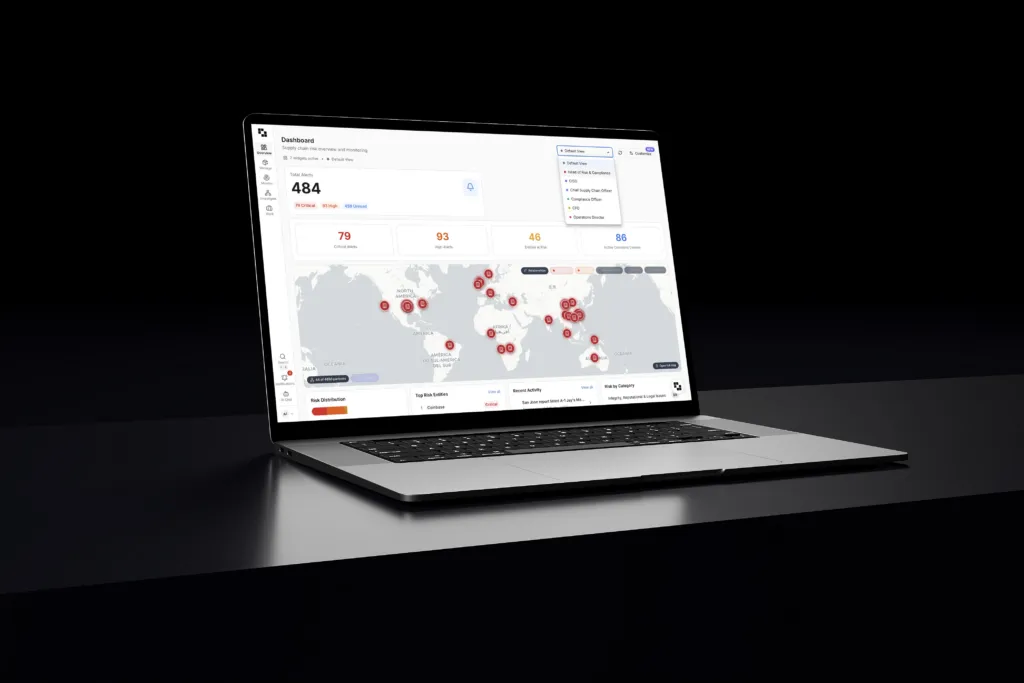
A new geographic visualization shows where suppliers are located globally and helps teams understand where risk is concentrated across their supplier base.

SBOM Version Management and CI/CD

Product teams updating software frequently can produce a large volume of SBOMs as new versions are released. Exiger now enables product development teams to version-manage SBOMs, tracking all iterations in a single interface to improve visibility and traceability across changing versions.

  • For automated builds, the platform will create new SBOM versions with each build and provide a pinning feature so teams can select which versions are tracked in inventory.
  • We’ve also made it faster and easier to create SBOMs via multiple input options, including drag-and-drop file uploads directly into inventory, accelerating time to analysis.
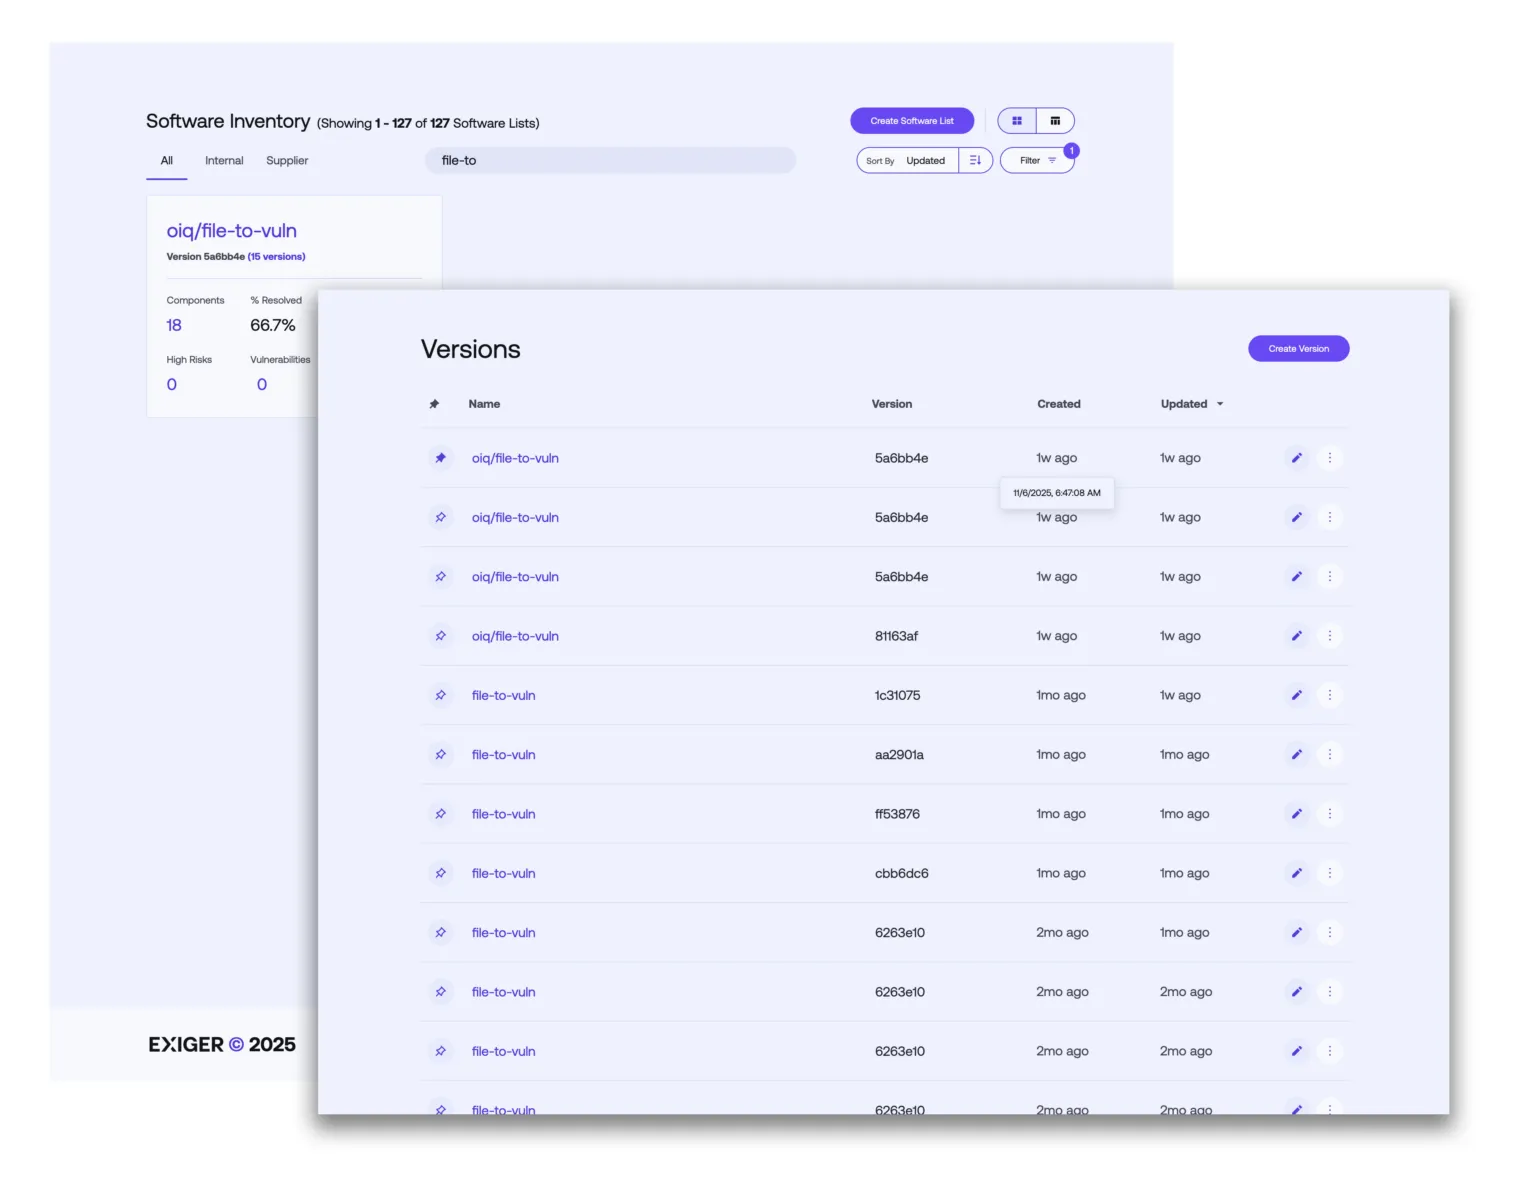
SBOM version management

For each software package in your inventory, every SBOM version is listed along with its history to add clarity and make versions easier to track.

Get in touch to request a demo of these powerful new software supply chain visibility tools.
Table of Contents

Get in Touch

Learn how you can build a more resilient software supply chain.
insights

Perspectives

Webinar

The Four Forces Shaping Resilience in 2027

Supply Chain Management
Supply Chain Risk Management
Supply Chain Visibility
Risk & Operations
Tariffs and Trade Friction
Your Backup Supplier May Share the Same Point of Failure
Article

Your Backup Supplier May Share the Same Point of Failure

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
Faster Sourcing Changes the Risk Equation
Article

Faster Sourcing Changes the Risk Equation

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
Why Procurement Is Moving Up the CFO Agenda
Article

Why Procurement Is Moving Up the CFO Agenda

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
DPW 2026 and the Decisions Procurement Can Change
Article

DPW 2026 and the Decisions Procurement Can Change

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
The Agentic Procurement Reality Check
Article

The Agentic Procurement Reality Check

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
FCC Moves to Require Onshoring or Reciprocal Recognition of Device Test Labs
Client Alert

FCC Moves to Require Onshoring or Reciprocal Recognition of Device Test Labs

AI technology
Compliance
Foreign Ownership
Geopolitical Issues
Supply Chain Optimization
Executive Order 14415 Could Reach Commercial and Dual-Use Suppliers
Article

Executive Order 14415 Could Reach Commercial and Dual-Use Suppliers

Critical Infrastructure
Defense
Geopolitical Issues
Part Selection and Management
Supply Chain Management
Executive Order 14415 Puts Product-Level Evidence at the Center of Defense Supply Chain Risk
Article

Executive Order 14415 Puts Product-Level Evidence at the Center of Defense Supply Chain Risk

Defense
Critical Minerals
Supply Chain Visibility
Supply Chain Risk Management
Government Regulations
Exiger & Vodafone Executive Dinner
Event

Exiger & Vodafone Executive Dinner

Autonomous Supply Chain
Supply Chain Management
Supply Chain Optimization
Supply Chain Resilience
Supply Chain Risk Management
Product Tour

1EXIGER.AI Live Product Demos

AI technology
Risk & Operations
Software Supply Chain Security
Supply Chain Management
How to Win a Trade War: Inside the New Rules of Economic Conflict with Soumaya Keynes
Podcast

How to Win a Trade War: Inside the New Rules of Economic Conflict with Soumaya Keynes

AI technology
Geopolitical Issues
Risk & Operations
Risk Assessments
Software Supply Chain Security