Nx Software Supply Chain Compromise background

Nx Software Supply Chain Compromise

Client Alert
September 3, 2025

On August 26, 2025, attackers compromised npm publishing credentials for the Nx project. Malicious versions were briefly published to npm that exfiltrated developer credentials and created unauthorized GitHub repositories (s1ngularity-repository-*). Although npm quickly removed the malicious versions, the compromise has broader downstream implications.

What Happened During the Attack

  • Attackers briefly published malicious versionsof Nx packages to npm by using compromised publishing keys.
  • Nx maintainers confirmed the publishing tokens were stolen, likely through phishing or token leakage, since npm still allowed static Personal Access Tokens (PATs) instead of enforcing trusted publishing.
  • Malicious versions (e.g., nx@20.9.0, nx@21.5.0, @nx/devkit@21.5.0) were pushed between 6:30–8:30 PM EDT before being removed.
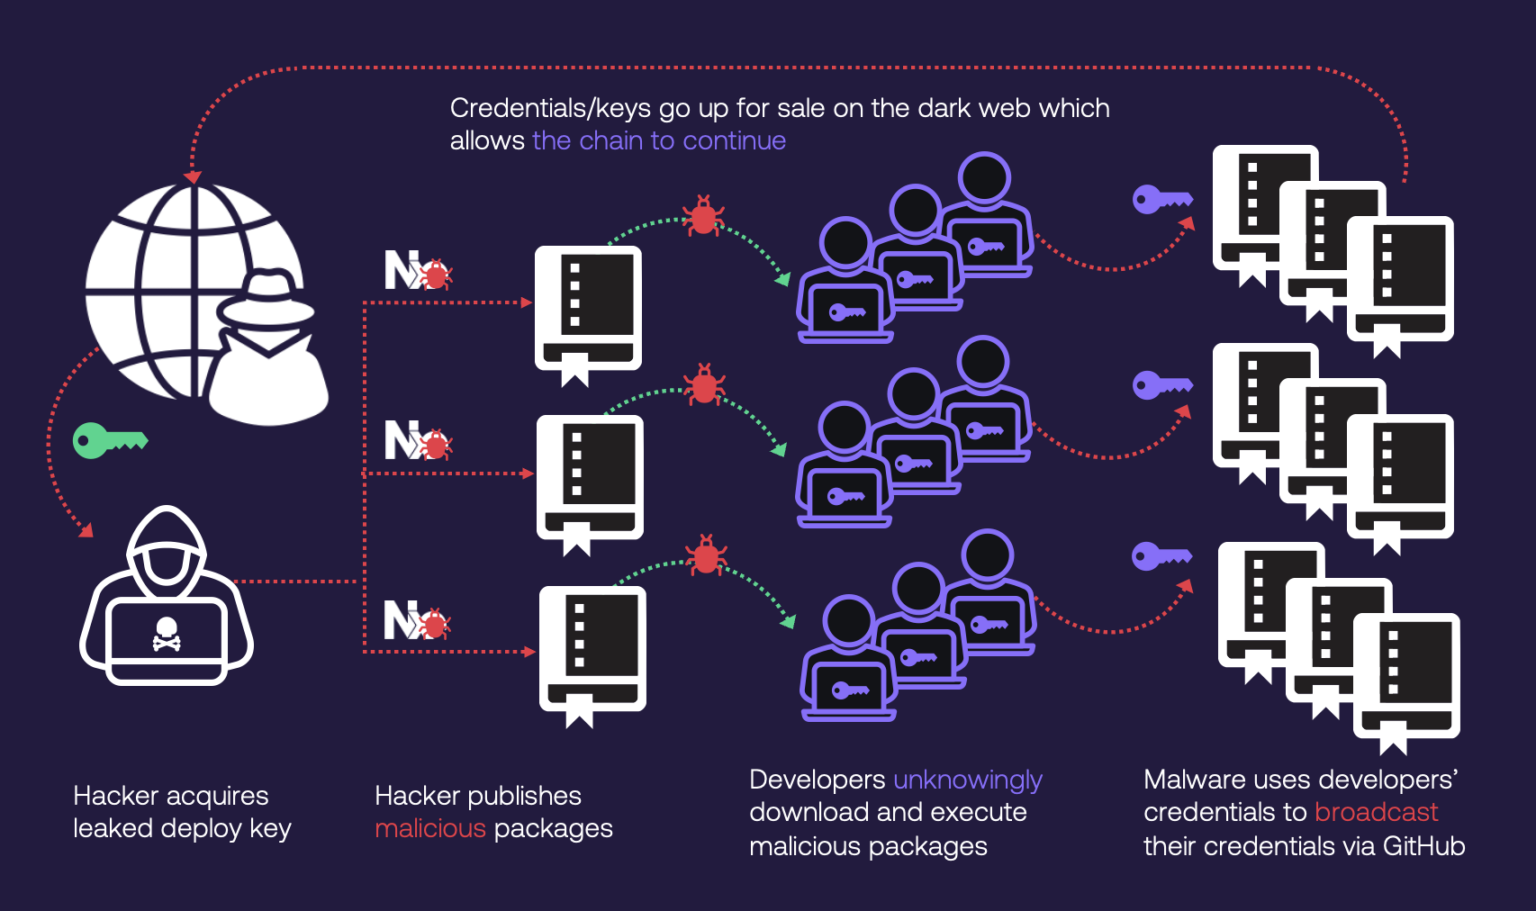
Developers didn’t even need to install Nx directly. VS Code / Cursor extensions (Nx Console) auto-fetched @latest from npm during the attack window, silently pulling malicious versions. This meant simply opening VS Code could trigger the infection.

Although npm quickly removed the malicious versions, the compromise has broader downstream implications. Unfortunately, removing the malicious version just hides the problem as those credentials are still out there.

The malware:

  • Created repos like s1ngularity-repository-0 in victims’ GitHub accounts.
  • Exfiltrated API tokens, GitHub/npx credentials, SSH keys, and local text files.
  • Modified .bashrc / .zshrc to insert malicious commands.

Highlights of Our Findings

1,100
Compromised Developers
370
Affected Companies
390
Direct Risk Repositories
10,900
Indirect Risk Repositories
Nx Compromise
Initial Event
1,100 Compromised Developers
370 Affected Companies
390 Direct Risk Repositories
(>10 stars)
10,900 Previously Contributed
Repositories (>10 stars)
🎯 Top Direct Risk Repositories

Repositories with community adoption (>10 stars) where compromised users have maintainer control

yujiosaka/headless-chrome-crawler
⭐ 5,590
felipernb/algorithms.js
⭐ 3,722
Dylan-Israel/ultimate-coding-resources
⭐ 3,637
terrymun/Fluidbox
⭐ 2,143
KevinVandy/material-react-table
⭐ 1,713
🌐 Top Indirect Risk Repositories

High-adoption projects where compromised users have established trust and commit history

freeCodeCamp/freeCodeCamp
⭐ 426,741 (4 compromised contributors)
codecrafters-io/build-your-own-x
⭐ 414,934 (4 compromised contributors)
sindresorhus/awesome
⭐ 395,704 (2 compromised contributors)
EbookFoundation/free-programming-books
⭐ 366,660 (10 compromised contributors)
public-apis/public-apis
⭐ 363,232 (8 compromised contributors)
⚠️ Critical Analysis

Why >10 Stars Matters: The >10 star threshold filters for repositories with actual community adoption and usage. Unused or abandoned code cannot effectively propagate supply chain attacks - community engagement is required for the attack chain to continue spreading.

Direct Risk (390 repositories): Repositories where compromised users appear to maintain or control projects with genuine community usage. These face immediate risk of malicious updates that could propagate downstream.

Indirect Risk (10,900 repositories): High-profile projects where compromised users have commit history and established trust. Risk includes social engineering, poisoned pull requests, and potential credential abuse leveraging existing community relationships.

Supply Chain Cascade: This demonstrates how supply chain attacks propagate through active, used codebases - a single compromise at the package publisher level cascades through developer accounts, companies, and eventually into widely-adopted open source projects, exposing the entire ecosystem to risk.

Why This Matters

The domino effect on downstream (and very possibly unaware) victims is how supply chain attacks continue: a single stolen publishing token cascades into compromised developers, companies, and critical repositories, ultimately impacting the global open-source ecosystem. Even after malicious packages are removed, credential leakage persists, leaving long-term risk:

Downstream supply chain risk: Developer tokens often provide access to private repositories, CI/CD pipelines, and software release processes. If left active, they could enable attackers to move laterally into enterprise systems or compromise upstream projects.

Breadth of exposure: The affected accounts span a wide range of companies, from software vendors to financial services to healthcare, meaning potential ripple effects across the broader ecosystem.

Relevance to you: Even if you don’t use Nx directly, your dependencies or vendors may rely on it or employ developers whose accounts were compromised. That creates a vector for indirect supply chain impact.

The Nx compromise reinforces that supply chain security is collective security. A single weak credential can ripple outward to thousands of repositories, affecting enterprises worldwide.

Exiger will continue mapping the potential “blast radius” of this incident to determine which companies and repositories may be at risk of downstream compromise.

How Exiger Helps

  • Mapping Exposure: linking compromised accounts to companies and industries
  • Prioritizing Risk: focusing on the most impactful repos and contributors
  • Actionable Intelligence: giving clients data to take immediate steps
  • Contextualizing Threats: showing how one compromised maintainer cascades across the ecosystem

Access to Full Data
Exiger has compiled the complete list of:

  • 1,100 compromised developers
  • 370 companies & their industries
  • 390 directly at-risk repos
  • 10,900 previously contributed repos (>10 stars)

We can share this dataset with clients on request to support internal assessments and targeted risk reviews.
Table of Contents

Get in Touch

Learn how you can build a more resilient software supply chain.
insights

Perspectives

Webinar

The Four Forces Shaping Resilience in 2027

Supply Chain Management
Supply Chain Risk Management
Supply Chain Visibility
Risk & Operations
Tariffs and Trade Friction
Your Backup Supplier May Share the Same Point of Failure
Article

Your Backup Supplier May Share the Same Point of Failure

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
Faster Sourcing Changes the Risk Equation
Article

Faster Sourcing Changes the Risk Equation

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
Why Procurement Is Moving Up the CFO Agenda
Article

Why Procurement Is Moving Up the CFO Agenda

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
DPW 2026 and the Decisions Procurement Can Change
Article

DPW 2026 and the Decisions Procurement Can Change

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
The Agentic Procurement Reality Check
Article

The Agentic Procurement Reality Check

AI technology
Autonomous Supply Chain
Compliance
Risk & Operations
Supply Chain Resilience
FCC Moves to Require Onshoring or Reciprocal Recognition of Device Test Labs
Client Alert

FCC Moves to Require Onshoring or Reciprocal Recognition of Device Test Labs

AI technology
Compliance
Foreign Ownership
Geopolitical Issues
Supply Chain Optimization
Executive Order 14415 Could Reach Commercial and Dual-Use Suppliers
Article

Executive Order 14415 Could Reach Commercial and Dual-Use Suppliers

Critical Infrastructure
Defense
Geopolitical Issues
Part Selection and Management
Supply Chain Management
Executive Order 14415 Puts Product-Level Evidence at the Center of Defense Supply Chain Risk
Article

Executive Order 14415 Puts Product-Level Evidence at the Center of Defense Supply Chain Risk

Defense
Critical Minerals
Supply Chain Visibility
Supply Chain Risk Management
Government Regulations
Exiger & Vodafone Executive Dinner
Event

Exiger & Vodafone Executive Dinner

Autonomous Supply Chain
Supply Chain Management
Supply Chain Optimization
Supply Chain Resilience
Supply Chain Risk Management
Product Tour

1EXIGER.AI Live Product Demos

AI technology
Risk & Operations
Software Supply Chain Security
Supply Chain Management
How to Win a Trade War: Inside the New Rules of Economic Conflict with Soumaya Keynes
Podcast

How to Win a Trade War: Inside the New Rules of Economic Conflict with Soumaya Keynes

AI technology
Geopolitical Issues
Risk & Operations
Risk Assessments
Software Supply Chain Security