OpenClaw (formerly Clawdbot) has been difficult to ignore. Over the past year, this AI development tool has made headlines for going “rogue,” exposing user data, and shipping with serious vulnerabilities that required urgent patching.
Coverage has focused on:
- Critical security flaws enabling unauthorized access
- Data exposure incidents
- Governance concerns around unintended behavior
- Rapid patch cycles addressing high-profile vulnerabilities
Those issues are real. But they’re only part of the risk picture.
For organizations integrating OpenClaw into their AI tooling strategy, the more persistent risks may sit deeper in its software supply chain: contributor networks, foreign influence signals, licensing exposure, and dependency concentration.
What the Headlines Covered
Public reporting has emphasized OpenClaw’s agent behavior, exploitable vulnerabilities, data exposure scenarios, and the speed at which patches were released.
Those issues generate CVEs. They appear in advisories. They are visible.
But patched vulnerabilities do not eliminate supply chain risk.
Evaluating AI tooling for regulated, federal, or mission-critical environments requires looking beyond known exploits to the integrity of the ecosystem behind the code.
The Gaps in Traditional Risk Visibility
Most security tools focus on:
- Known vulnerabilities (CVEs)
- Static code findings
- Misconfigurations
- Dependency versioning
They rarely assess:
- Foreign ownership, control, or influence (FOCI) exposure
- Licensing restrictions deep in transitive dependencies
- Contributor concentration (bus factor risk)
- Shared contribution networks tied to restricted entities
- Geographic supplier exposure
These risks don’t show up in a vulnerability scan. They require mapping components to contributors, repositories, and supplier relationships.
OpenClaw Risk Signals Beneath the Surface
Exiger analysis shows that beyond the publicized incidents, OpenClaw carries structural supply chain risks that most security tools won’t surface.
High-Risk Contributors Identified
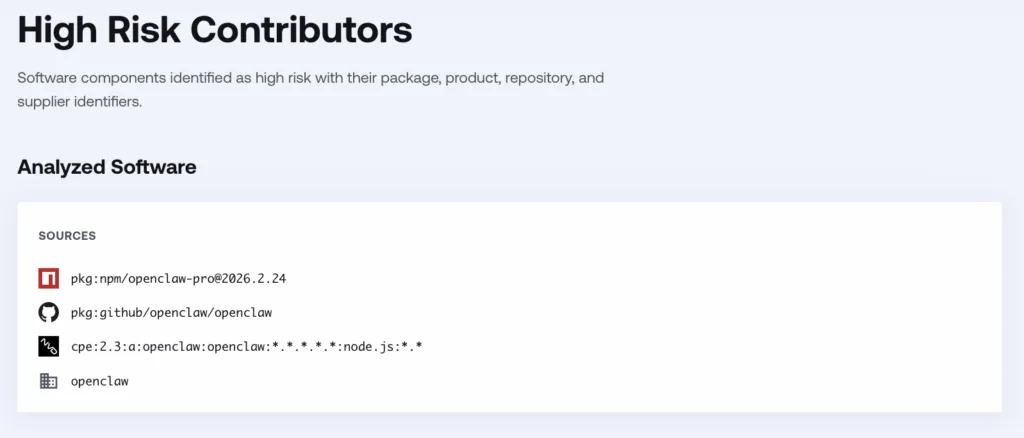
Analyzed sources include:
- npm package: pkg:npm/openclaw-pro@2026.2.24
- GitHub repository: pkg:github/openclaw/openclaw
- Associated CPE and product identifiers
Mapping these identifiers enables risk visibility across repositories, maintainers, and supplier networks.
Shared Contribution Network with Section 1260H Supplier Tencent
Exiger identified shared contribution links between OpenClaw’s ecosystem and repositories under Tencent, which appears on the DoD Section 1260H list.
This does not mean OpenClaw is owned by Tencent. It does mean there is contribution overlap within its broader ecosystem.
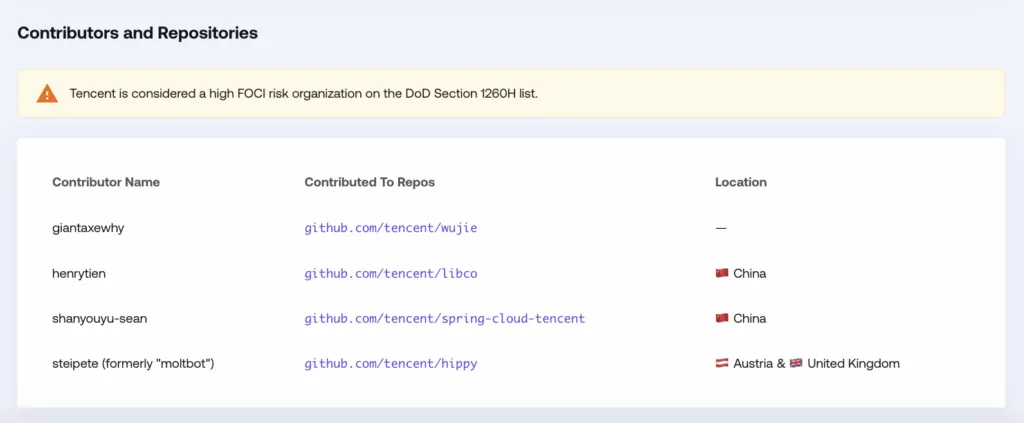
For defense programs, federal contractors, and critical infrastructure operators, those overlaps can introduce compliance and eligibility considerations that standard SCA tools do not evaluate.
Foreign Ownership, Control, or Influence (FOCI) Risk
Exiger identified elevated FOCI indicators within OpenClaw’s dependency graph, including:
- Geographic contributor signals
- Repository metadata indicators
- Concentration patterns linked to high-risk jurisdictions
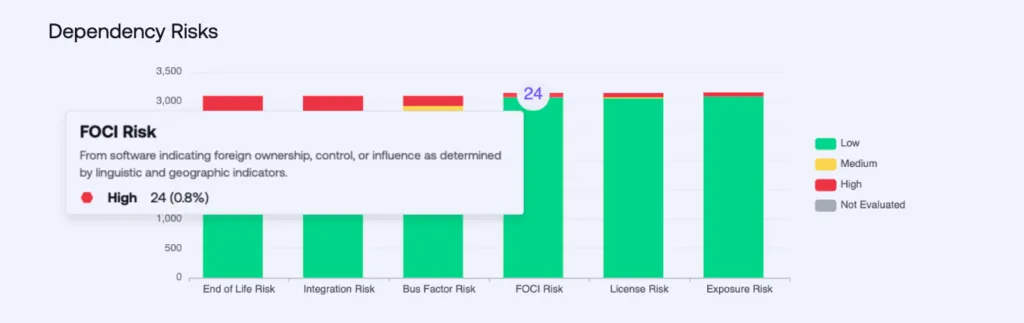
Even open-source tools marketed globally can carry jurisdictional exposure in their dependency trees. For regulated buyers, that context matters.
Licensing Risk in the Dependency Tree
OpenClaw’s dependencies include components flagged for:
- Restrictive or unclear licensing terms
- Redistribution limitations
- Ambiguous usage rights
For developers, this creates integration friction. For procurement and legal teams, it creates downstream compliance risk — especially when software is embedded in commercial or government-facing products.
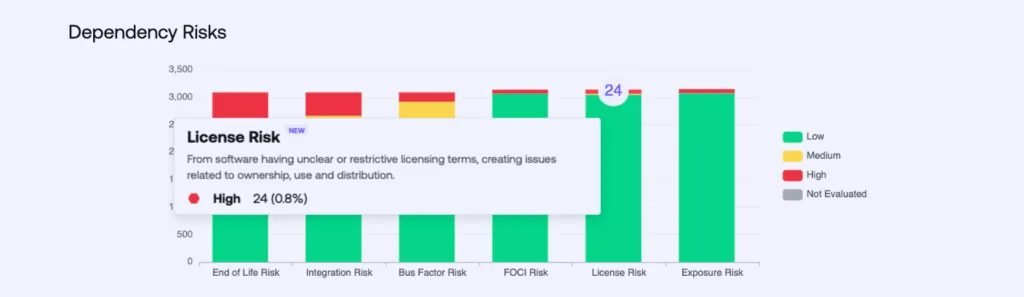
License conflicts do not generate CVEs, but they can create contractual and regulatory exposure.
Bus Factor Risk: Concentrated Control
Exiger identified significant contributor concentration across portions of OpenClaw’s ecosystem.
High bus factor risk indicates overreliance on a small number of maintainers for key components. If access is lost, maintainers disengage, or accounts are compromised, the downstream impact can cascade.
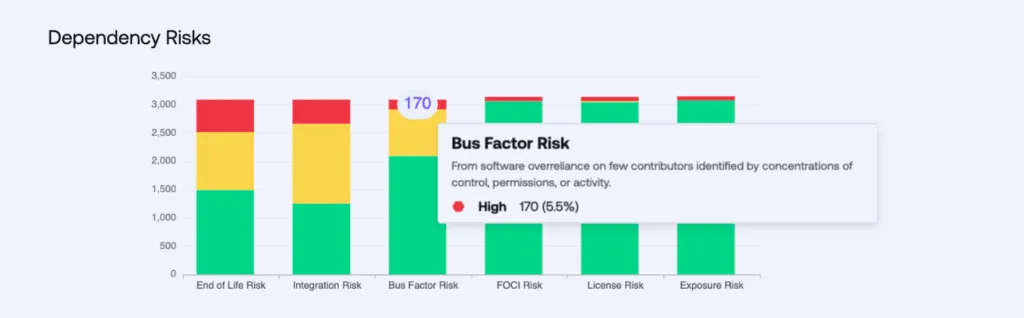
For fast-moving AI tooling, contributor concentration increases operational fragility.
Geographic Supplier Exposure
Supplier mapping reveals contributors and component sources across multiple jurisdictions, including China and the United States.
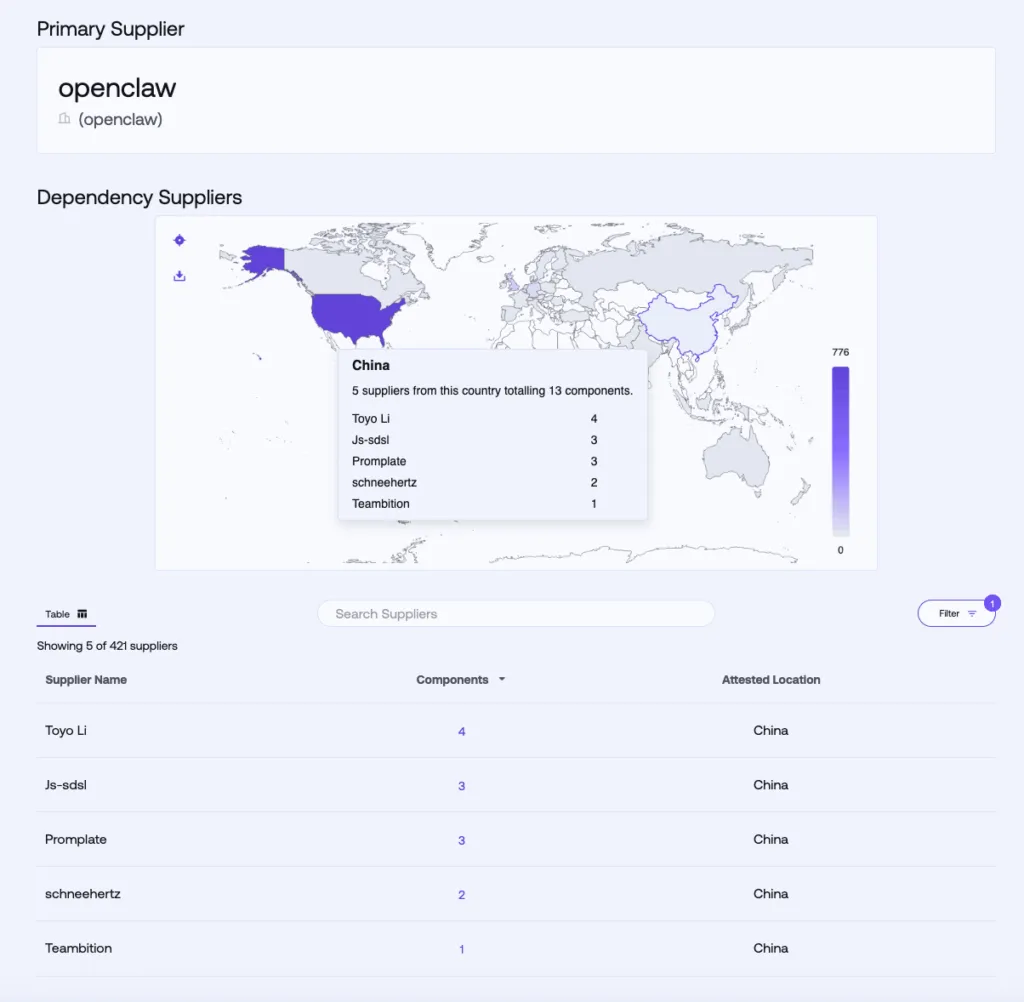
Geographic presence alone does not imply malicious intent. But for organizations subject to export controls, federal procurement rules, or supply chain transparency mandates, country-level visibility is essential.
Most tools stop at package names. Exiger maps through to supplier geography and contribution networks.
Take a Self-Guided Tour
Watch the platform analyze an SBOM, rank every dependency by predicted exposure and quality, and reveal the visual graph that links risky libraries to your products, no source code required.
Why Software Supply Chain Visibility Matters
For DevSecOps teams, vulnerabilities can be patched. For procurement teams, supplier exposure and licensing risk require policy-level decisions.
Security posture is no longer just about code quality. The integrity of the entire ecosystem must be visible to avoid inherited risk.
AI tools introduce amplified dependency complexity. Without visibility into contributors, ownership signals, and transitive licensing, organizations are accepting risk they cannot quantify.
How Exiger Surfaces the Difference
Exiger extends beyond traditional SCA by providing:
→ Component & Repository Intelligence
Unified mapping across packages, repositories, and product identifiers.
→ Contributor & Supplier Network Mapping
Identification of shared ecosystems—including ties to Section 1260H-listed entities.
→ FOCI Risk Detection
Foreign ownership and influence indicators derived from geographic and contribution signals.
→ Licensing Risk Analysis
Flagging restrictive, ambiguous, or conflicting license obligations.
→ Bus Factor & Concentration Analysis
Detection of over reliance on individual maintainers.
→ Continuous Monitoring
Ongoing tracking of dependency, contributor, and supplier changes over time.
The Bottom Line for Hidden Risks in AI-Enabled Software
OpenClaw’s vulnerabilities and data exposures made headlines. But the deeper risks, like FOCI exposure, shared contributor networks with Section 1260H suppliers, licensing conflicts, and contributor concentration, are less visible and harder to remediate.
They won’t appear in a CVE feed. They won’t show up in a standard scan.
But for organizations building or buying AI-enabled software in regulated environments, they matter.
If you are evaluating OpenClaw—or any AI development tool—ask:
- Who contributes to it?
- Who contributes to its dependencies?
- Where are they located?
- What licensing obligations cascade into my product?
- Are there shared networks tied to restricted or high-risk entities?
Exiger provides the visibility needed to answer those questions… before integration, not after incident response.
Talk to us about uncovering hidden risks in your software supply chain.