As the cyber risk landscape evolves, checking a box for certification is no longer sufficient. The most resilient organizations are looking beyond traditional cybersecurity metrics to evaluate the financial, operational, and cultural integrity of their suppliers. Risks run in packs and when systems fail, it’s often the result of broader organizational weaknesses — not just technical ones.
At S4x25, JC Herz, SVP of Exiger Cyber Supply Chain, called attention to a critical blind spot in traditional cybersecurity assessments: non-security metrics. Factors such as financial fragility, operational disarray, and leadership churn aren’t tangential to cyber risk; they are cyber risk. These overlooked indicators should inform how we assess and manage risk across the supply chain to improve software supply chain security.
Cybersecurity doesn’t operate in isolation — it reflects the broader operational hygiene of a company. From attention to detail to hiring practices and executive turnover, non-security signals offer a window into how a business performs under pressure.
Financial and HR Red Flags as Risk Indicators
Security is a cost center — and that makes it vulnerable to budget pressures. Layoffs, reduced capex/opex, or delayed renewals can all signal weakening defenses. Tools like LinkedIn and Glassdoor offer insight into organizational structure, cybersecurity headcount, and employee sentiment, which can all reflect the true investment in cyber resilience.
- Cash Flow
- Layoffs
- Rule of 40
- Revenue Growth
- Return on Equity
- Debt-to-Equity Ratio
- Profitability
- Regulatory Filings
- Corporate Credit Scores
- Liquidity
Legal, Regulatory, and Product Risk: It All Connects
A company’s litigation history, regulatory penalties, or association with sanctioned entities can be early warning signs. Product recalls and equipment failures illustrate how technical debt and supply chain dependencies can cascade into failures with national security implications.
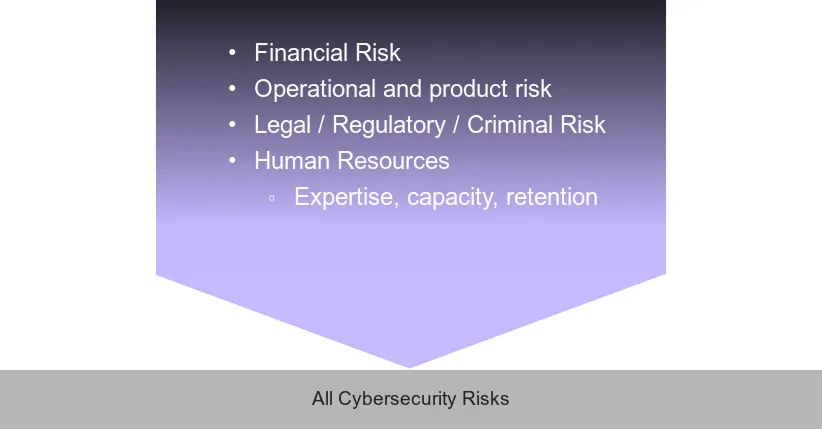
- Financial Risk
- Operational and product risk
- Legal / Regulatory / Criminal Risk
- Human Resources
- Expertise, capacity, retention
All Cybersecurity Risks
The Cyber Poverty Line — and the Obesity Index
While many SMBs struggle to afford baseline compliance, some enterprises have bloated operations rife with technical debt. Both extremes signal cybersecurity fragility. The key is building a repeatable playbook — like DoD’s SPRS and CMMC metrics — to drive consistency and accountability. Exiger’s Supply Chain Product Assurance Playbook is valuable resource to get started.
From Intelligence to Action: Use Non-Security Metrics Wisely
The to-do list is clear: use third-party risk management (TPRM) to integrate these metrics into your assessment. Monitor for CMMC compliance, track federal exclusion lists, and don’t be afraid to walk down the hall to Procurement and pull risk information about your vendors.
Don’t shy away from applying procurement carrots — and sticks.
As JC Herz notes, this is an intelligence problem — one that large organizations are investing years of research into solving. But we don’t need to reinvent the wheel. We can draft off existing efforts, and most importantly, use what we already know about how companies work (or don’t) to stay one step ahead.