Executive Summary
The U.S. Department of Commerce’s Bureau of Industry and Security (BIS) finalized rule blocks the import or sale of new “connected” vehicles and certain key software and components if they rely on software tied to China or Russia. Think all those cloud-connected systems like cameras, microphones, and GPS systems that are now standard on modern vehicles.
The requirements will be phased in, with software starting with Model Year 2027, and vehicle-connectivity hardware following in Model Year 2030.
Annual Declarations of Conformity will be required via BIS’s CARS portal.
Why Is This a Problem for Automakers?
After years of outsourcing software modules to their suppliers, automakers are discovering they don’t know what’s inside their sprawling, multi-tier software supply chains. Over time, “software from suppliers” stopped meaning a few clearly labeled features and started looking like big, bundled packages with limited visibility into who wrote what. Even with contracts and documentation, code often pulls in third-party libraries and subcontracted work many layers down.
So when the government asks, “show us where it came from,” many companies are scrambling to map ownership, provenance, and update paths across thousands of components. Russian or Chinese-linked code can be buried deep in supplier packages, including embedded systems and middleware. Replacing it can mean expensive rewrites, fresh safety and reliability testing, supplier changes, and potential delays to vehicle launches. And demonstrating compliance needs to be done every year.
Exiger Makes It Easy
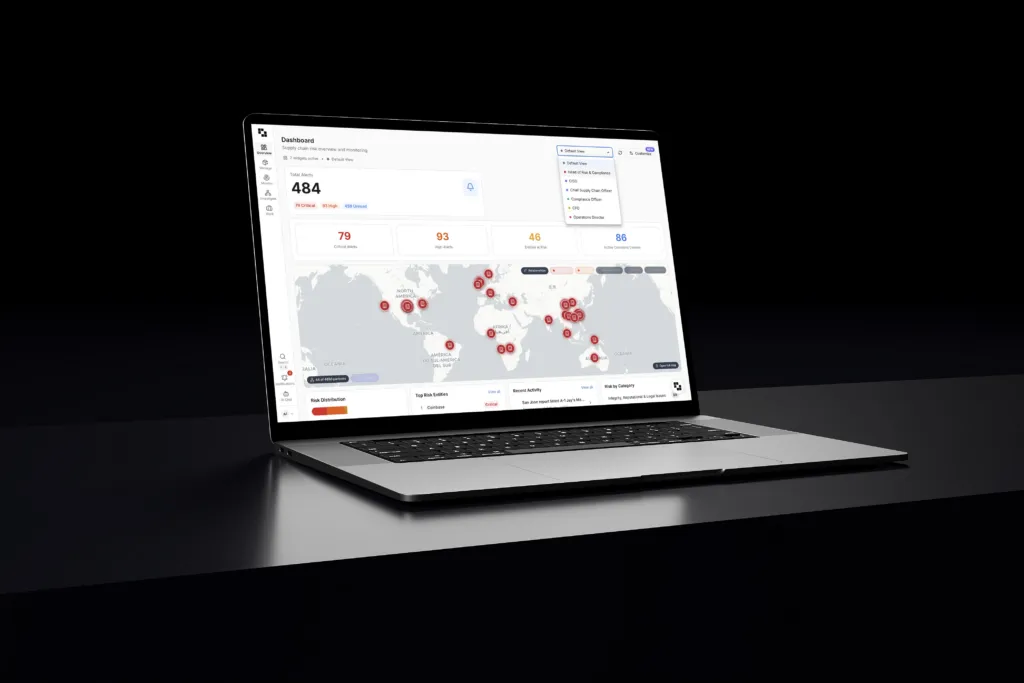
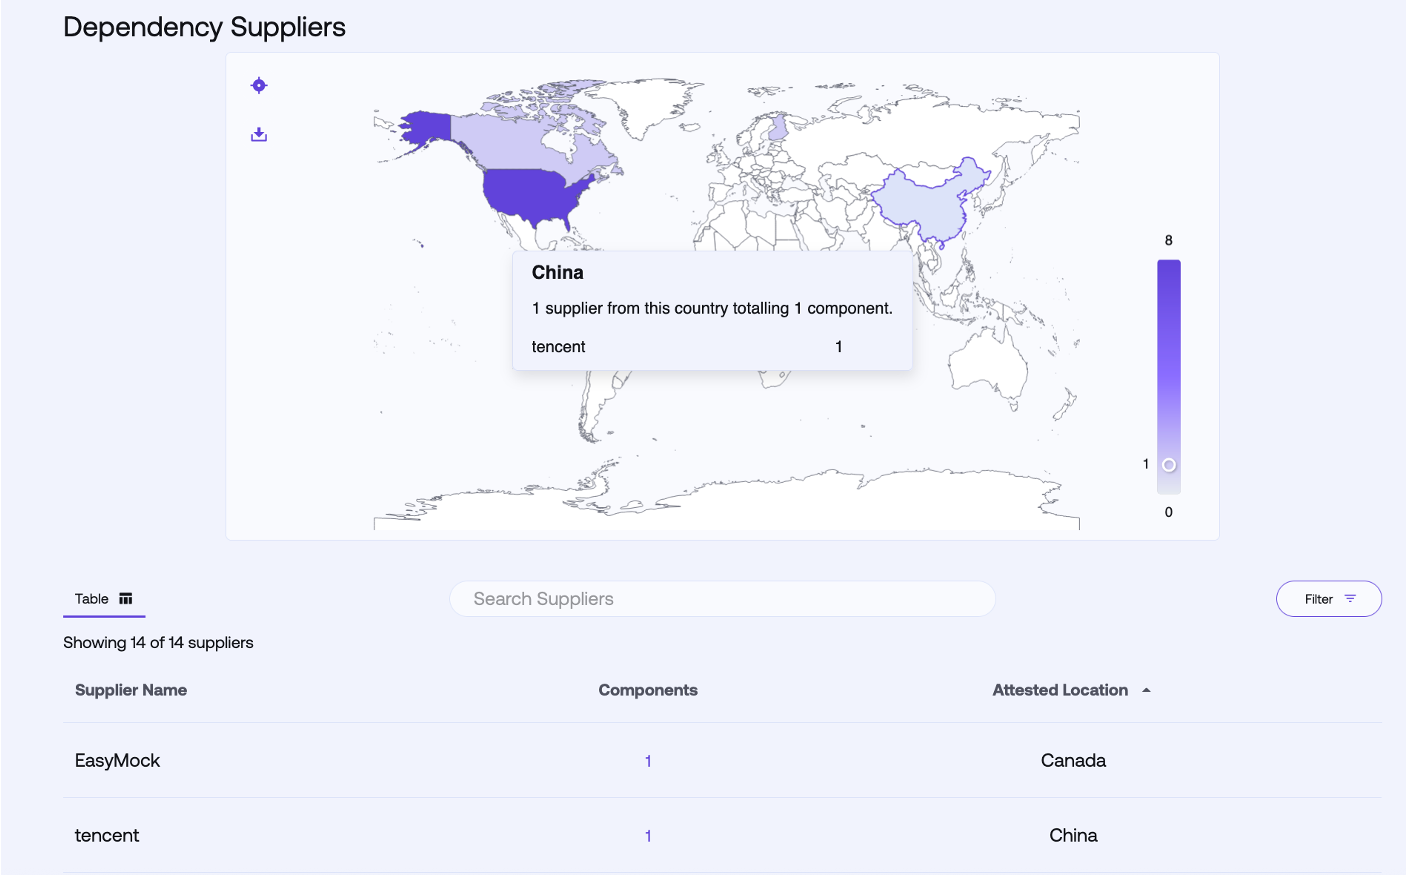
Exiger Cyber instantly finds FOCI (foreign ownership, control, or influence) signals deep inside software supply chains. It monitors and analyzes 500M+ repositories, 150M+ packages, and more than 68M verified supplies.
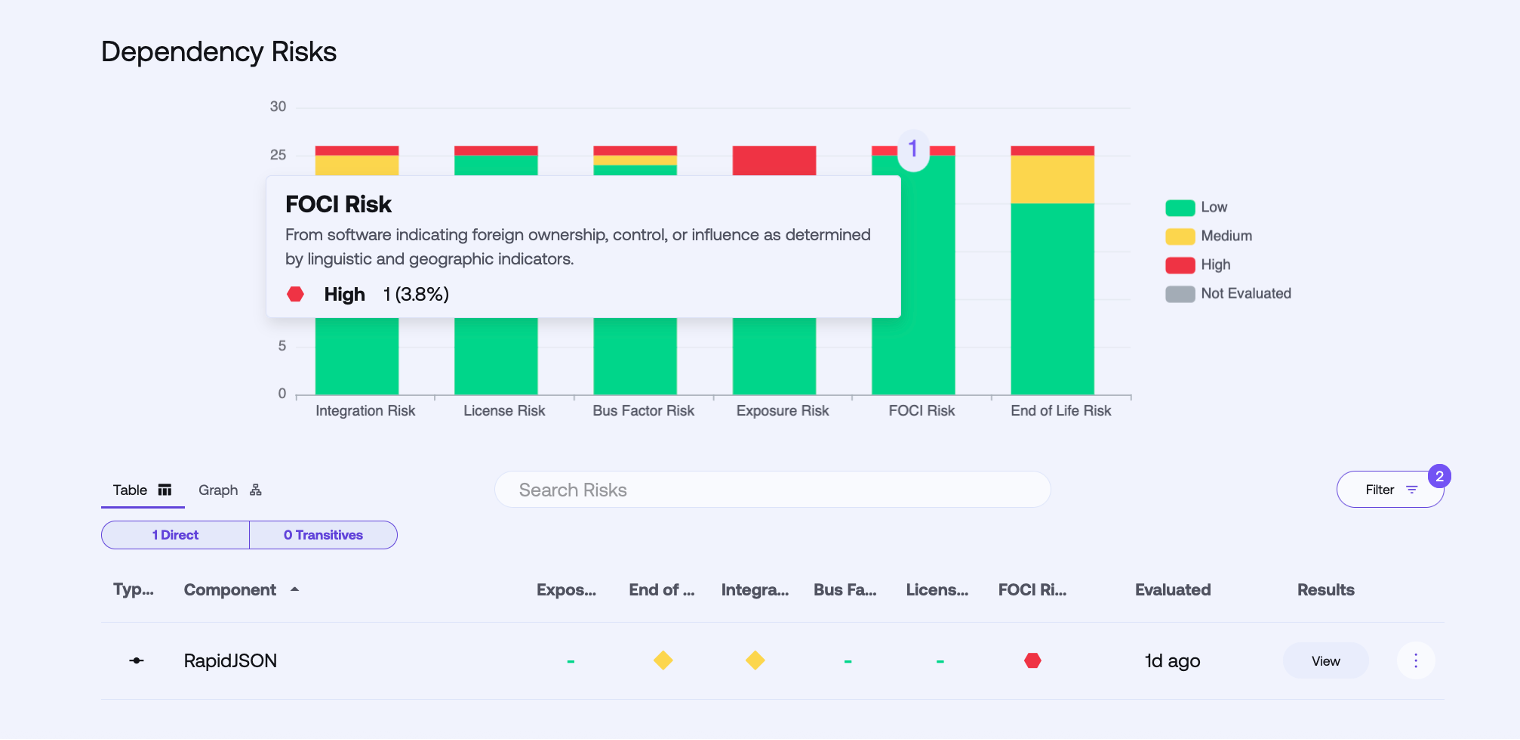
By continuously monitoring software, contributors, and supplier relationships across billions of records, Exiger Cyber surfaces risky contributors and FOCI-linked code even when it’s buried deep in your supply chain.
Take a Self-Guided Tour
Watch the platform analyze an SBOM, rank every dependency by predicted exposure and quality, and reveal the visual graph that links risky libraries to your products, no source code required.
Why This Matters
This new regulation highlights three critical questions for every automaker:
Do you have full visibility into your software supply chain including all dependencies?
→ It’s not enough to track the software from the “Tier-1” suppliers you know about. You need visibility into the full dependency trees, and not just for compliance reasons. Removing adversarial software reduces risk.
How quickly can you identify Chinese or Russian software components?
→ Manually researching all software, and all dependency trees is impractical, slow, and expensive.
Are you continuously monitoring all existing and new software for FOCI risk?
→ Software components aren’t static and new contributors to software libraries and components can change. Automatically monitoring compliance minimizes your risk and costs.
Talk to us about moving from manual, days-long investigations to automated identification in seconds, cutting the time-to-answer and enabling immediate mitigation.