Software Supply Chain Security
Exiger secures the software supply chain with unmatched transparency, giving organizations full visibility over software and firmware.
Exiger Serves 150+ Fortune 500 Companies and More Than 60 U.S. Federal Agencies


Software Supply Chain Security for Continuous Protection at Scale
Exiger analyzes Software Bill of Materials (SBOMs)—whether provided or generated from binaries—and continuously monitors for risk. Our platform enables security and procurement teams to meet regulatory requirements, prevent disruption, and enforce vendor accountability.
With rising threats and regulatory pressure, cyber supply chain risk management (C-SCRM) is no longer optional. 1EXIGER.AI combined with unmatched data coverage and continuous monitoring of leading risk indicators, equips organizations with the intelligence needed to manage software supply chain risk at scale.
Software Supplier Risk Analysis
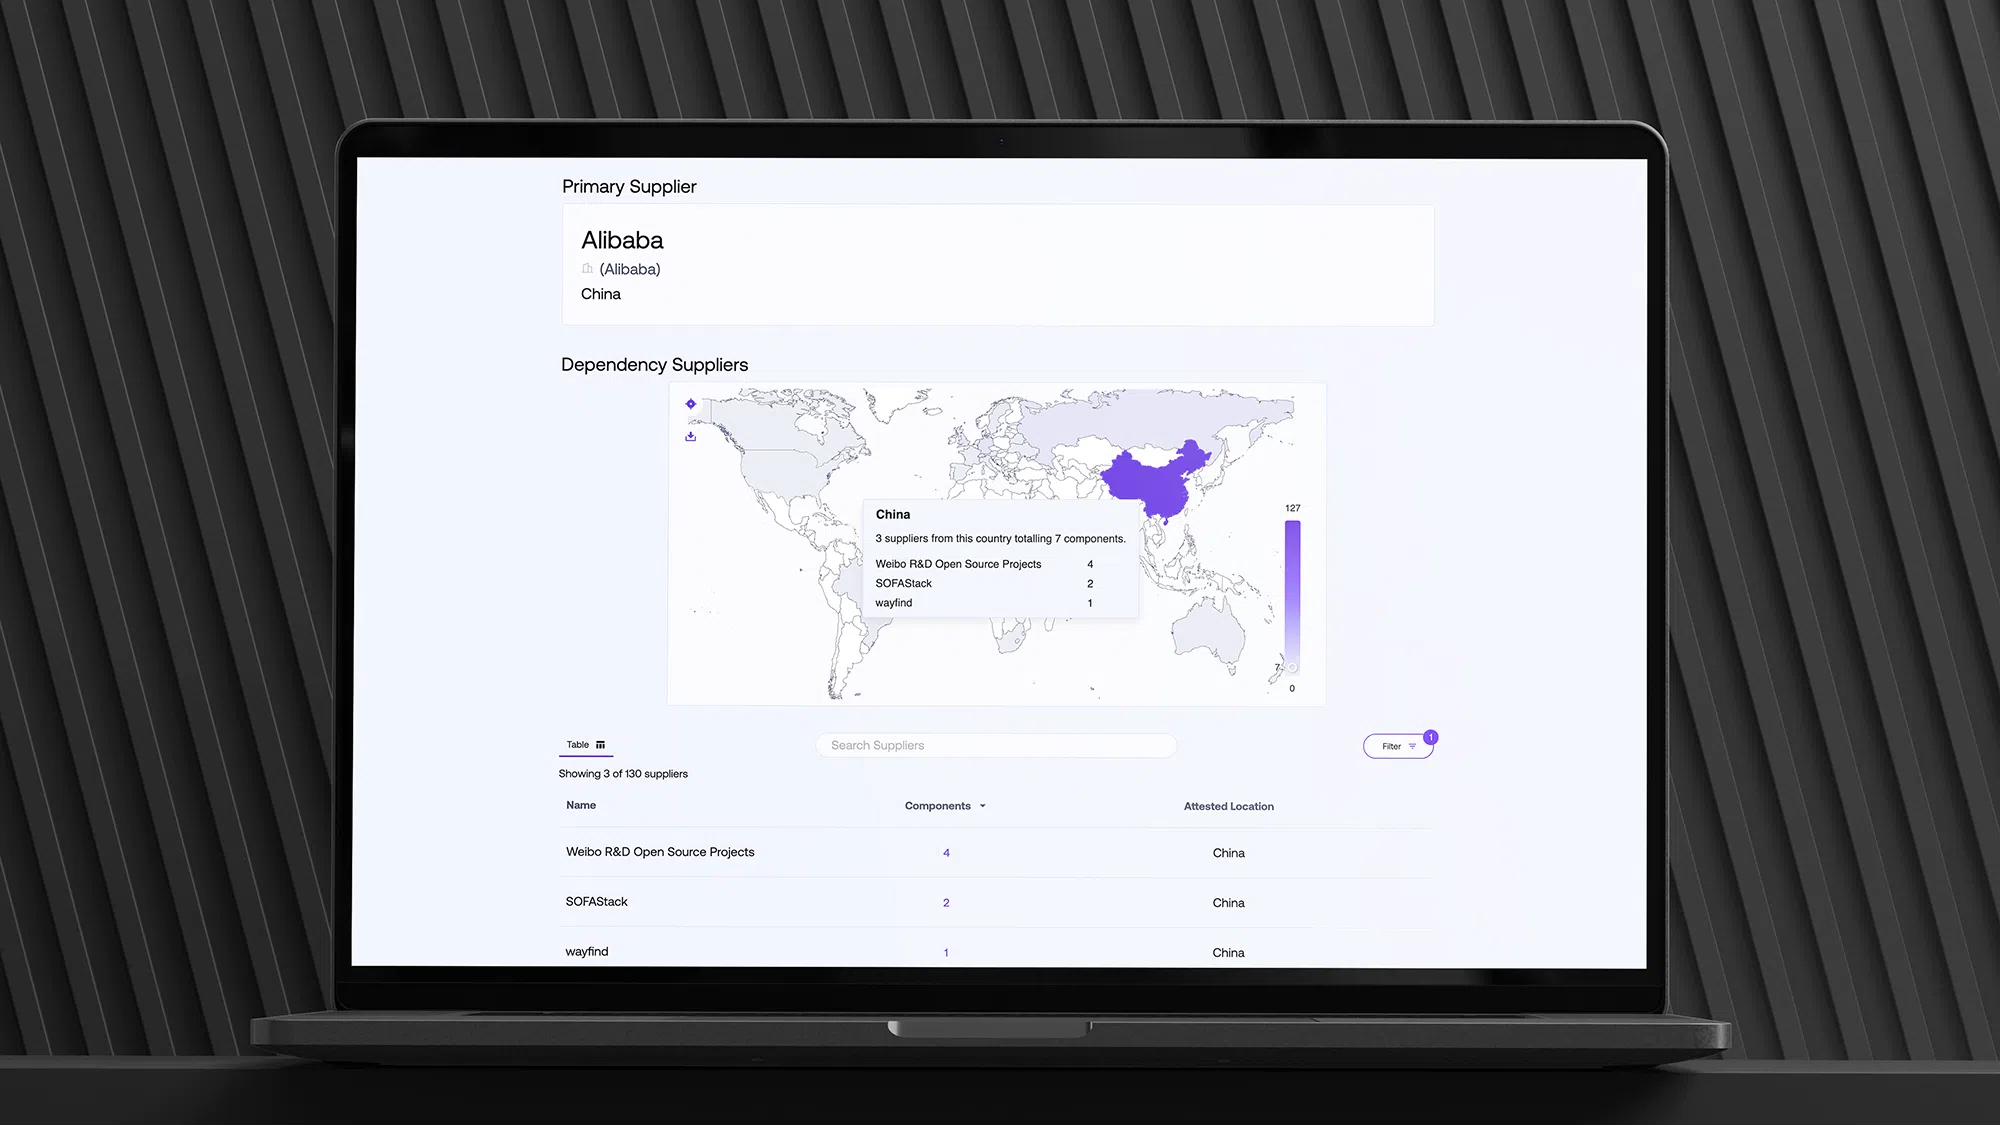
Beyond the software itself, Exiger provides insights into the software’s suppliers and contributors.
Exiger uncovers FOCI risks (even if intentionally obfuscated), sanctioned or prohibited suppliers, and shows your exposure to untrustworthy entities.
Open Source Software and SBOM Analysis
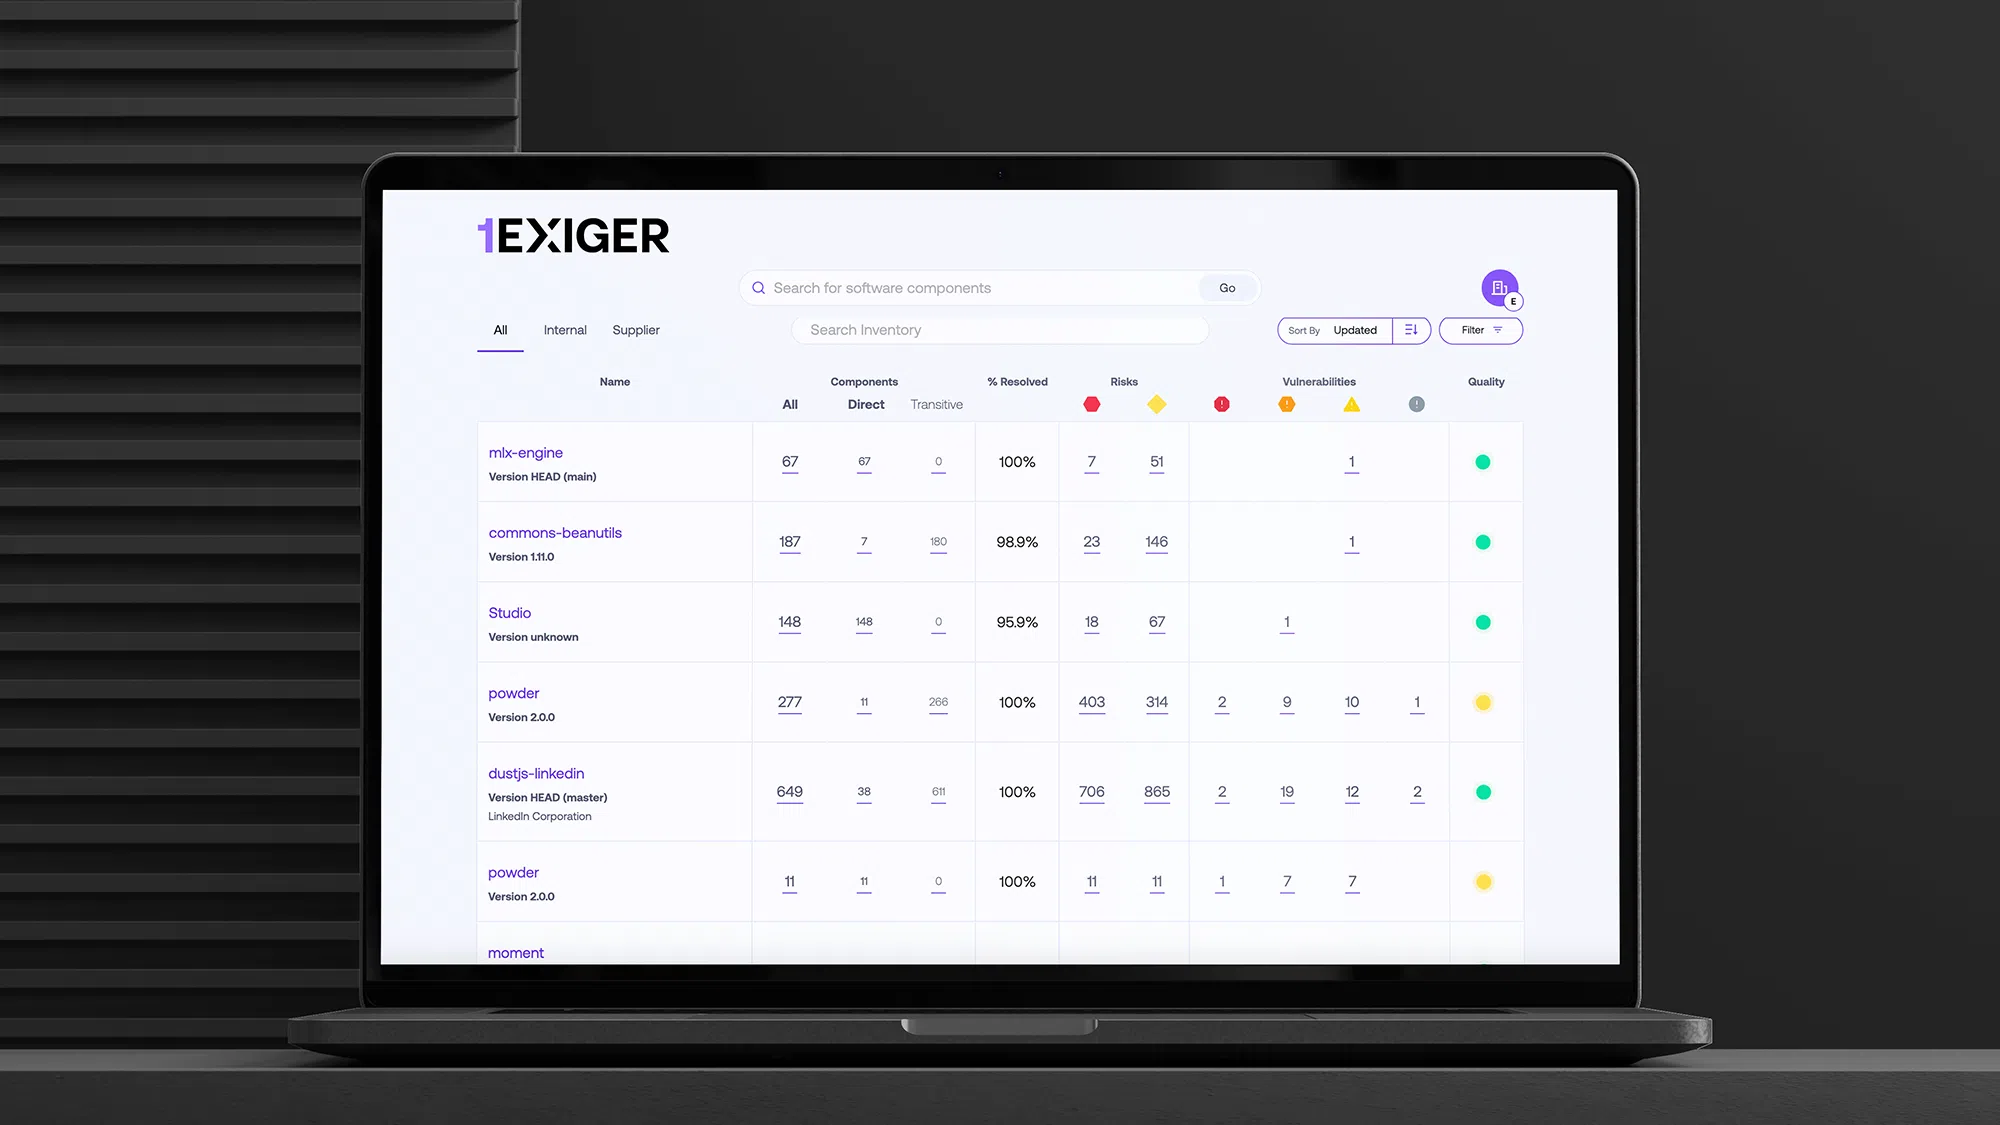
Over 90% of software relies on open source software, and waiting for CVE disclosures leaves you 8–12 months behind emerging threats.
Exiger SBOM analysis uses leading risk indicators to deliver early insights, highlight trustworthy third parties, and flag potential ransomware or breach impacts—providing systematic protection across your software supply chain.
Binary Analysis and SBOM Generation
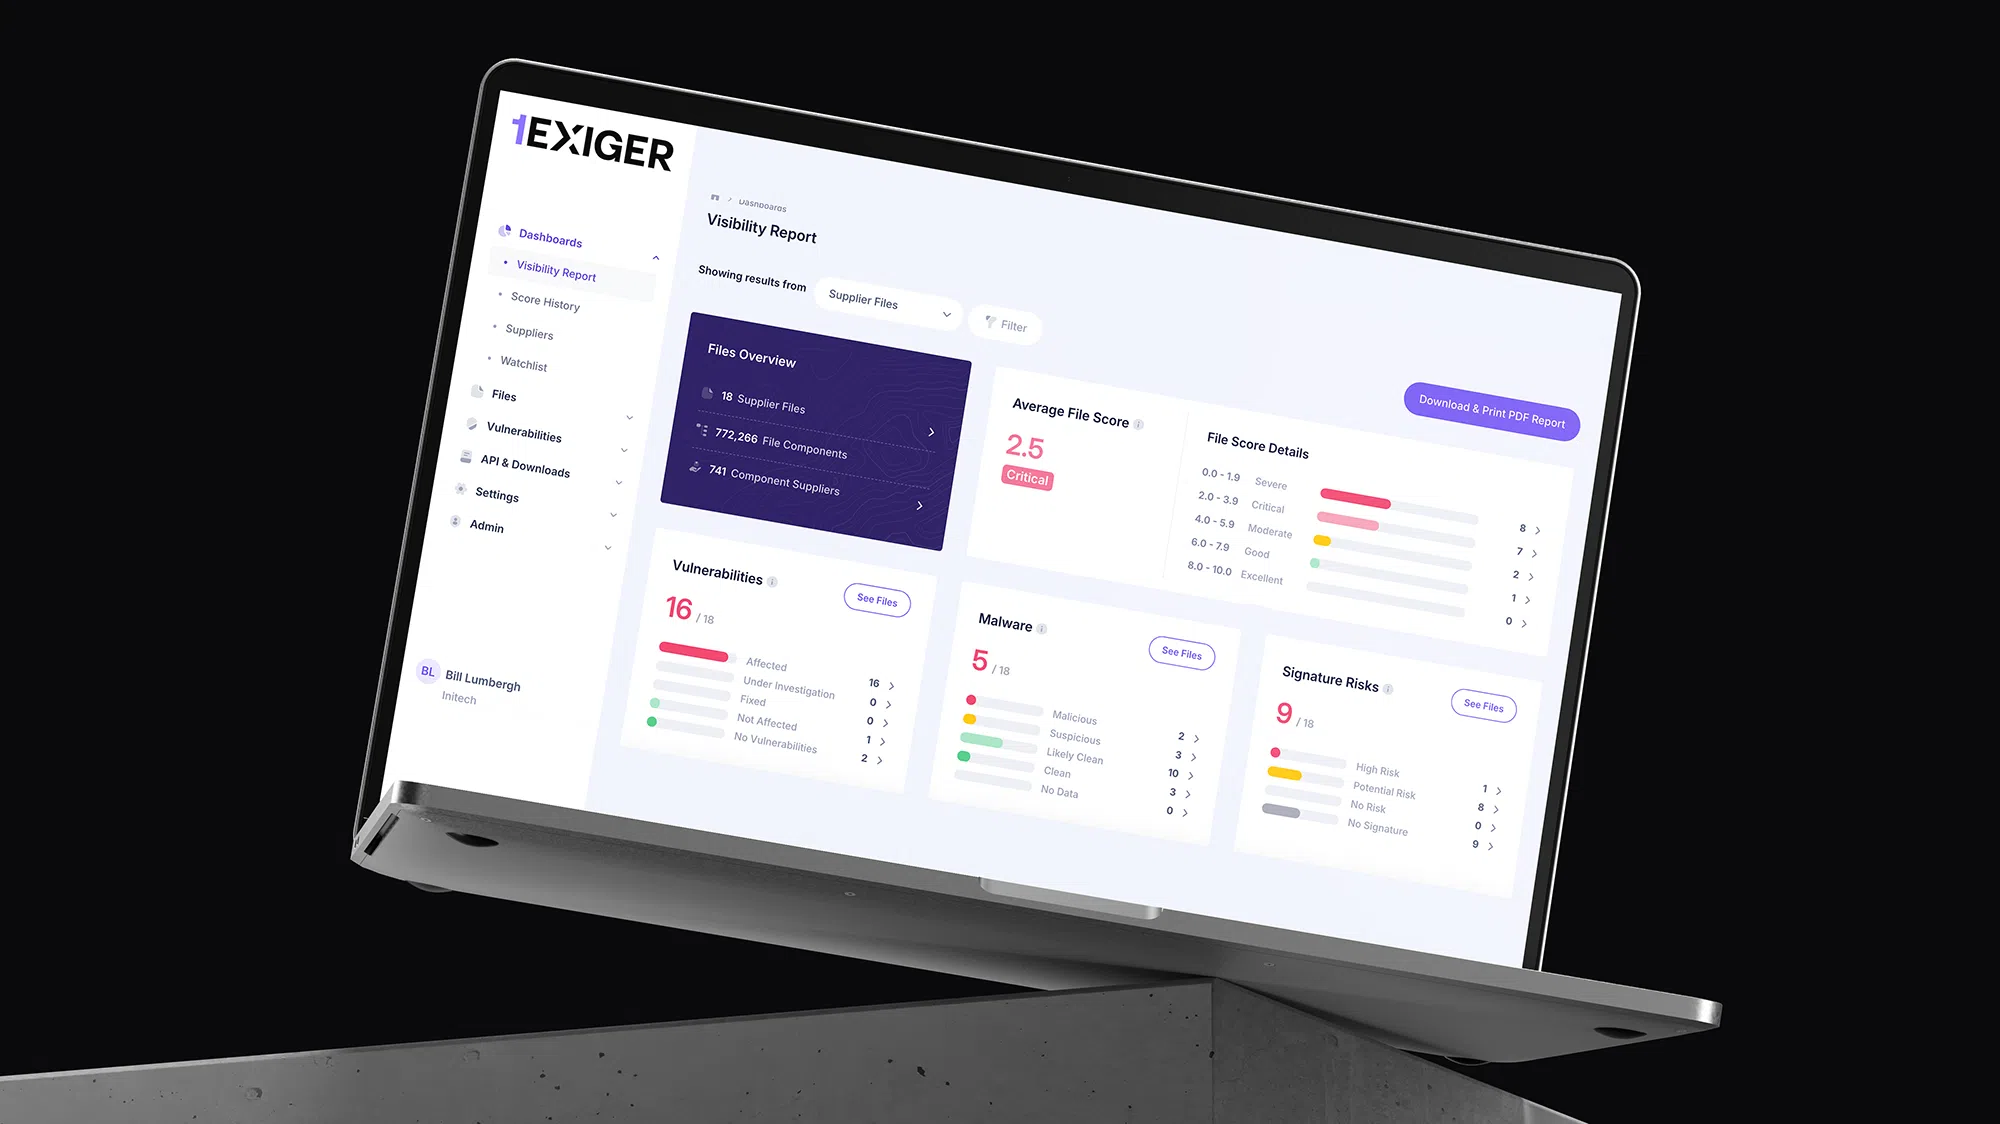
Accurate, independently generated SBOMs with detailed risk analysis, continuous vulnerability monitoring, and verified software provenance.
Eliminate false positives and get a clear, prioritized view of risk, so you can meet regulatory requirements, hold vendors accountable, and ensure your software is safe to purchase, ship, and install.
Customer case studies
Responding to Customer Demands for SBOMs
Customer case studies
Detecting Undeclared Sanctioned Hardware via Firmware Analysis
Customer case studies
Inherited Vendor Cyber Risk – Microsoft Exchange Server Zero Day Vulnerability
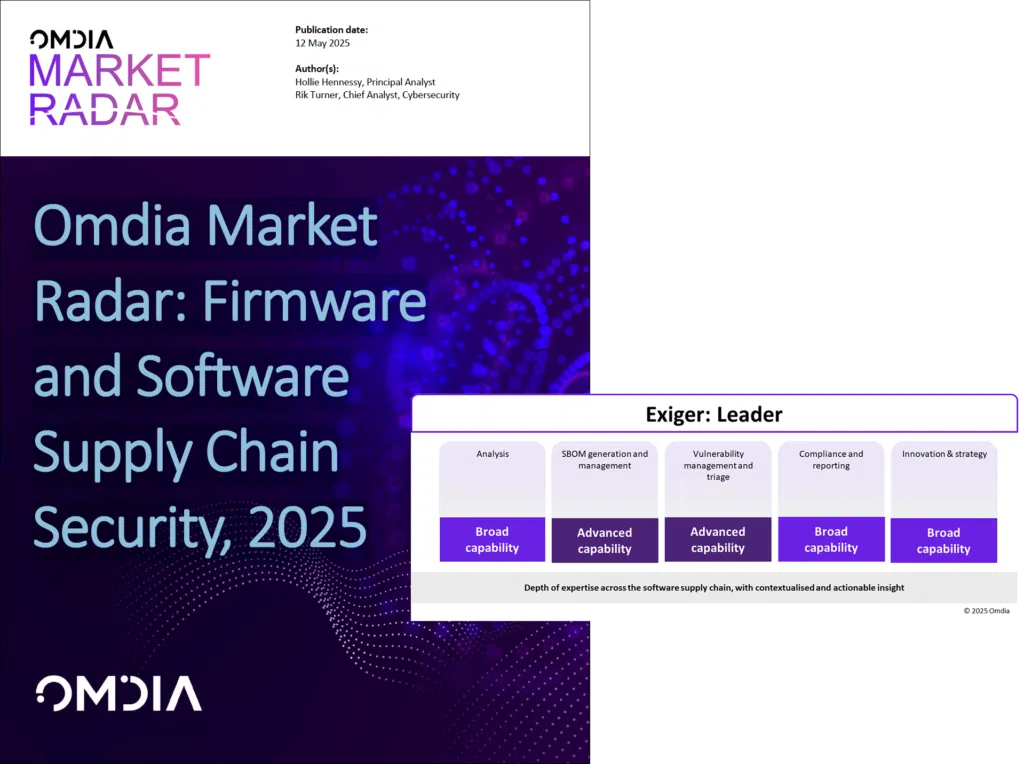
Exiger named a Leader in the Omdia Market Radar: Firmware and Software Supply Chain Security
Exiger delivers on key cyber capabilities assessed by analyst firm Omdia, including firmware and software analysis, SBOM creation and management, vulnerability management and triage, compliance and reporting, and overall innovation.
The P1 Solutions Marketplace is a digital repository of post-competition, readily awardable pitch videos that address the Department of Defense’s (DoD) most significant challenges in hardware, software and service solutions. Awardable solutions have been assessed through complex scoring rubrics and competitive procedures and are available to Government customers with a Marketplace account.

Exiger named a Winter 2026 leader in Governance, Risk, and Compliance
Exiger is a mission-driven, market-moving force redefining AI-powered supply chain resilience.
Exiger Named Value Leader in The Hackett Group’s Spring 2026 SolutionMap for Procurement Technology.

We were able to achieve our own security objectives and satisfy customer demands.
Exiger Named Winner of TPRA 2024 Third Party Risk Management Service Provider Innovator Award
Exiger Named in Fast Company’s List of Brands That Matter for Second Consecutive Year
Three Exiger Executives Awarded 2024 Pros to Know by Supply & Demand Chain Executive
Exiger and Oshkosh Recognized by Supply & Demand Chain Executive with 2023 Top Supply Chain Projects Award

Exiger tops ProcureTech100 for the 3rd consecutive year
Have Questions? We Have Answers.
Exiger’s approach gives transparency beyond CVE scanning, mapping who built your software, where it came from, and why it matters for risk and resilience.
Read why Exiger was deemed a Leader in the Omdia Market Radar: Firmware and Software Supply Chain Security (SSCS).
It’s important to remember: an SBOM is simply an ingredients list – it doesn’t include any risk analysis on its own. To gain value from an SBOM, you need the kind of analysis Exiger provides.
Explore how the latest Executive Order strengthens software supply chain security — and what it means for your organization.
Understand the impact of the European Cyber Resilience Act (CRA) and how businesses can prepare for compliance.
Discover practical steps for financial institutions to meet DORA requirements with confidence.
So which SBOM should I use? That’s probably not the right question. Think of differently produced SBOMs like differently produced medical images. They each provide a different view into the contents of a package.
They each have pros and cons: SCA analysis provides early vulnerability detection, but it can suffer from incomplete dependency information, and it tends to generate more false positive results. It’s also only available if you have the source code, making it not an option for many legacy products or for asset owners who lack access to source code.
Binary Composition Analysis (BCA) offers an accurate reflection of the software’s contents in its entirety. It also occurs downstream of tampering opportunities so it can detect compromises introduced at a late stage. It can also generate SBOMs in the absence of source code. BCA, however, does require the significant expertise and file format intelligence provided by Exiger solutions.
Learn more on When to Generate an SBOM.
We also track supplier responsiveness (time-to-remediation) and use high-precision component attribution to reduce false positives, so teams focus on fixes that materially cut blast radius.
Binary executable file formats such as MZDOS and ELFs
Installers such as VISE, UPX, MSI, CABs, INNO, and InstallShield
Archives such as ZIPs, GZ/Tarballs, Freeze, and CPIO
Operating Systems such as Windows, Linux, VxWorks, QNX, and other RTOS
Common IT file systems such as NTFS, FAT32, and EXT
Embedded file systems such as LittleFS, SquashFS, JFFS2
Backup images such as WIM, Acronis Files & Directories, Clonezilla/GPart
Programming language identification for BASH, C#, and C/C++ source files
Contact us for the most up to date and detailed list as it grows continuously.
We also map blast radius across your portfolio so responders know what to quarantine first—see our analysis of recent npm compromises for how this works in practice.
Learn more about this governance angle in the Supply Chain Product Assurance Playbook.
Our customer-proven integrations, offering endpoints to generate/ingest SBOMs, apply exploitability context, and automate workflows.
Contact us or details on incorporating Exiger’s software supply chain visibility into your wider cybersecurity programs.
Solutions Based on Your Needs
1EXIGER.AI
AI-native operating system for supply chain execution, accelerating procurement, reducing costs, and multiplying your team’s capacity.
Risk & Compliance
Comprehensive solutions for Trade Compliance, Supplier Risk Management, Enhanced Due Diligence, TPRM, and Know Your Customer.
Supply Chain
Identify and map multi-tier suppliers, track risks and disruptions, and improve cost, lead time, and sustainability performance.
Software Supply Chain Security
Transform software supply chain security with unmatched visibility, resilience, and compliance at scale.